Engineering Evidence
The machine-readable files and the Terraform draft.
Files in this report folder
Every file the run publishes, with what it is for. A name links to the file when it is in this folder and you opened this page from it. The size and the sha256 of every file are in manifest.json: this page is written before the manifest and a file cannot state its own size, so only the files of the Terraform draft show theirs here.
| File | What it is | In this report | Size in bytes |
|---|---|---|---|
assessment.json | The full assessment: every unit, finding and count, machine-readable. Every number in this workspace is read from it. | Yes | – |
engineering/architect-report.md | The assessment in words: the run status and its checks, and for each unit the class, the confidence and the STACKIT target proposed. | Yes | – |
engineering/analysis-details.md | The working behind engineering/architect-report.md: the relations and combinations the engine evaluated for the decisions that depend on them. Nothing here is a second decision. | Yes | – |
architecture/dependencies.mmd | The source and the target architecture as a diagram in Mermaid text, for tools that draw it. The Architecture section of this page draws the same units itself. | Yes | – |
migration/technical-sequencing.md | A draft order of work: waves computed from the dependencies between units. A starting point for the architect's plan, not a schedule. | Yes | – |
engineering/review.csv | One row per unit for spreadsheet review. | Yes | – |
engineering/review-edges.csv | One row per dependency between units, for the architect to confirm, correct or complete. | Yes | – |
workspace.json | The compact model the pages show, machine-readable. No page embeds it: the pages are complete without it, and a tool reads the model from this file. | Yes | – |
index.html | The front page: the header, the navigation and the Overview. The other sections are the pages in pages/. | Yes | – |
pages/applications.html | The Applications section as a page of its own, with the same header and navigation. Which application each unit belongs to, and each application's migration strategy. | Yes | – |
pages/architecture.html | The Architecture section as a page of its own, with the same header and navigation. The units of the estate and what the assessment decided for each. | Yes | – |
pages/decisions.html | The Decisions section as a page of its own, with the same header and navigation. The decisions people must take, aggregated, with their options, owners and deadlines. | Yes | – |
pages/target-fit.html | The Target Fit section as a page of its own, with the same header and navigation. How well each STACKIT target fits: service, interface, Terraform, region, maturity, quota, lifecycle, operability, support and security. | Yes | – |
pages/migration.html | The Migration Plan section as a page of its own, with the same header and navigation. Waves, prerequisites, data movement and the order of work. | Yes | – |
pages/security-assurance.html | The Security & Resilience section as a page of its own, with the same header and navigation. What has been proven about security and resilience, what has not, and what needs evidence from outside; the resilience of each unit, where this run assesses it, is on the Operations page. | Yes | – |
pages/sovereignty.html | The Sovereignty section as a page of its own, with the same header and navigation. Dependencies, jurisdiction, data placement, key control and exit paths, source against target. | Yes | – |
pages/operations.html | The Operations section as a page of its own, with the same header and navigation. Whether the target can be run: identity, audit, observability, backup, restore, support and lifecycle. | Yes | – |
pages/cost.html | The Costs section as a page of its own, with the same header and navigation. Priced and unpriced coverage, and the inputs a cost estimate needs. | Yes | – |
pages/evidence.html | The Evidence section as a page of its own, with the same header and navigation. The counts, versions and sources behind every statement in this workspace. | Yes | – |
pages/engineering.html | The Engineering Evidence section as a page of its own, with the same header and navigation. The machine-readable files and the Terraform draft. | Yes | – |
pages/work-board.html | The Work Board section as a page of its own, with the same header and navigation. Every job of the migration in one list, in four queues: who does it, what it waits for, what closes it and which file it carries out. | Yes | – |
pages/decisions/ | The group pages of the Decisions section: the full cards of the records the page does not hold, one page per work package (the page of the section lists the groups), and, for a very large estate, its long lists cut into pages of a size a browser opens. Present only when the register has more records than the page holds cards. | Yes | – |
decisions.json | The decision register, machine-readable, with a template of the decisions file to fill in. | Yes | – |
migration/decisions.csv | The decision records as rows for a spreadsheet. | Yes | – |
executive/decisions.md | The decision records in words. | Yes | – |
executive/brief.md | The five-minute answer as a document: the run summary, what holds the estate back, what people must decide, the shape of the target and what has and has not been established. It restates numbers this file holds and scores nothing. | Yes | – |
migration/applications.csv | One row per application of the applications file you gave, with the values as you wrote them (a value you did not write is marked not provided), and one row per unit claimed by several applications. Header only without an applications file. | Yes | – |
migration/waves.csv | The dependency order of the units, one row per unit: the wave, WITHHELD when a part of the source was not read in full, or REFUSED for a unit the partial draft refuses for a missing input (in no wave). An order of work, not a schedule. | Yes | – |
migration/actions.csv | The register of what a person has to do, decide or establish before the draft is deployed, one typed row per item: gaps in the reading of the source, critical semantics left open, open decisions and manual actions of the plans, workload items that wait for evidence, and validation rows not yet established. Every member of decisions.json is a row; each row names the decision record that holds it. It lists what is open and decides nothing. | Yes | – |
migration/work-board.csv | The Work Board as a sheet: one row per job of the migration, in one of four queues (provide information, approve a design, perform migration work, verify), with its owner, priority, what it waits for, what closes it, its evidence, the files it carries out and the steps of the execution plan it holds. Every step of the plan is in exactly one job, or listed as not taken; pages/work-board.html shows the same jobs. Header only when the run wrote no execution plan. | Yes | – |
migration/source-target.csv | Each source unit beside its STACKIT target, one row per unit: the target service and its resources, or in words that there is none, that the unit is refused or that the source switches it off, and how many of its settings are kept (PRESERVED), changed (TRANSFORMED), accepted (ACCEPTED_*) or still to do (everything else, including anything not known). Counted from the rows of assurance/equivalence-ledger.csv; a unit with no ledger row has four zeros, which says nothing was counted, not that nothing is left to do. Header only when the Workspace holds no counts. | Yes | – |
migration/application-chain.csv | The drill-down from each application of the customer's file and each group the run suggested (PROPOSED: a reading of the source, not confirmed by anyone), one row per member unit: the AWS resource, the STACKIT target in the words of migration/source-target.csv, the ids of the decisions that still ask something about the unit, the steps of the execution plan that carry it with the number an answer leaves not taken, the Kubernetes manifest objects that tie to it by an exact literal match, and what the code scan says of the application. A run that read no plan or built no register marks those cells as not assessed, which is not an empty list. Header only when the Workspace holds none. | Yes | – |
migration/prerequisites.md | For each unit, the open decisions and manual actions that stand between its draft and its deployment, as its plan states them. | Yes | – |
migration/data-movement.csv | One row per stateful source unit (a database, a cache, a volume, a file share, an object store): its source and target service, the data class, RPO and downtime tolerance you stated (or marked not provided), the provisioned capacity the source states (not the size of the data) and the cutover dependency. The mechanism of every unit is UNKNOWN: StackToIT never moves data. | Yes | – |
migration/data-movement.md | The same units in words, with what the source and the plans do and do not state about each. No size, change rate, duration, transfer rate or downtime is ever stated, and no mechanism is chosen. | Yes | – |
migration/data-movement.json | The data_movement block of workspace.json with every stateful source unit (the facets, the unknowns, the provisioned capacity and where each fact is read from), as a file of its own, with the run it belongs to. workspace.json carries the tally of the units. | Yes | – |
architecture/current.mmd | The units of the estate and the dependencies among them as a Mermaid flowchart, with the units of each application drawn together. | Yes | – |
architecture/target.mmd | The same units with the STACKIT service proposed for each, its class and confidence, as a Mermaid flowchart. | Yes | – |
architecture/delta.mmd | The same units with what the move changes for each: its class, whether it has a target, and how many properties the draft names as not carried. | Yes | – |
architecture/current.svg | The drawing of the source architecture of the Architecture section, as a file of its own, without the links of the page. | Yes | – |
architecture/target.svg | The drawing of the proposed STACKIT target of the Architecture section, as a file of its own. | Yes | – |
architecture/delta.svg | The drawing of what the move changes, as a file of its own. | Yes | – |
assurance/safety.md | What has and has not been established about the draft, row by row, with the global invariants. It approves nothing and asserts neither equivalence nor that the draft is safe to apply. | Yes | – |
assurance/source-compatibility.md | How much of the source was read, the source providers the assessment saw and the source types the knowledge base does not know. | Yes | – |
assurance/target-readiness.md | How the STACKIT targets of the units stand in the capability catalogue and in the pinned provider (maturity, lifecycle), and the readiness dimensions. | Yes | – |
assurance/operational-readiness.md | The workload readiness of the units (installation, source artifacts, target preconditions, cutover, day 2) and the support options STACKIT evidences. Terraform generated is not workload ready. | Yes | – |
assurance/compliance-evidence.md | For each STACKIT service of the draft and each framework in scope, the state of the provider's own evidence. It says nothing about the compliance of your workload. | Yes | – |
assurance/compliance-evidence.csv | The cells of compliance-evidence.md as rows for a spreadsheet. | Yes | – |
assurance/equivalence-ledger.csv | The equivalence ledger: one row per unit and semantic of the assessment that the source states (workspace.json counts those it does not state), and one row per unit and property for the properties the draft does not carry, no semantic accounts for or that are critical and still open. Each row says how the source states the value, what proves the disposition, where the draft carries it and what stays open. Dispositions are the words the assessment uses today; PRESERVED appears only where the assessment or the draft's plan states it. | Yes | – |
assurance/evidence-ledger.csv | The evidence the ledger and the other blocks cite, one row per document, with what it backs, the date it was checked, the date after which it is to be checked again and its state. Evidence that states no such dates is UNDATED, never CURRENT. | Yes | – |
assurance/critical-semantics.json | The open critical semantics, one row per unit and semantic, with the disposition the contract result gives, the cause code, the sentences that say why the semantic is open and what would close it, the instances of a repeated unit and the alarm card where there is one. These are the rows the decision records name as their members; workspace.json carries the tally of them, with the run it belongs to. | Yes | – |
assurance/resilience.md | The RTO and RPO you stated (or that none was stated) and, for each unit that holds state or states a zone, replication or backup fact, what the source states. No unit is called resilient and no intent is chosen. | Yes | – |
assurance/resilience.json | The resilience block of workspace.json with every unit that states a failure-domain, replication or backup fact or holds state (the quoted source facts, the state and where each fact is read from), as a file of its own, with the run it belongs to. workspace.json carries the tally of the units. | Yes | – |
assurance/identity-transition.md | For each unit that runs as an identity or is one: the identities the source names, the static credential the knowledge base reads, the federation facts, the attachment the identity plan holds and its state. It makes no claim that federation is an option; privilege delta, break-glass access and human identity are not assessed. | Yes | – |
assurance/sovereignty.md | The sovereignty requirement (not provided unless your applications file states one), the dimensions of sovereignty with what the source shows and what the target is proposed to be, the dependencies and the exitability. Sovereignty is not residency; it holds no score and certifies no legal compliance. | Yes | – |
assurance/sovereignty.json | The sovereignty block of workspace.json as a file of its own, with the run it belongs to. | Yes | – |
financial/price-snapshot.json | The price_snapshot block of workspace.json as a file of its own, with the run it belongs to: which snapshot of the public STACKIT price list this run cites (source, retrieval date, sha256, currency, net list price) and how many of the drafted resources it priced. It holds list prices only: no quantity is read, no total is built, and no usage and no egress is computed. | Yes | – |
financial/cost-model.json | The cost model of the run, line by line: for each component of the AWS source (EC2 instances and EBS volumes) and of the STACKIT target (servers and volumes) its quantity (a value, a range or unknown, and where it comes from), its price record or the reason there is none, its pricing state and its amount; then the totals of the estate and of each service for each side (full, partial or none), the comparison of source and target with the reason a saving is or is not given, the price sources (the local price cache) and the assumptions the figures rest on. An estimate under one labelled scenario, not a bill. | Yes | – |
financial/priced-resources.csv | One row for each line of the cost model (financial/cost-model.json), source and target: the quantity with its provenance, the price record (SKU, rate, unit, the date it is valid from, the snapshot it comes from) or the state and the reason there is none, and the amount of a priced line. An empty amount is a line that is not priced, never a zero. | Yes | – |
financial/mapping.csv | The technical mapping beside the prices: for each server, boot disk, disk and database whose source and target are both in the computed group of the cost model, what each side states about vCPU, memory, CPU model, disk capacity, IOPS, throughput and high availability. The source side is read from the attributes of the source resource, the target side from the catalogue snapshot of the region; a fact a side does not state is the words not stated. A machine type is one of the types of the catalogue with at least the vCPUs and memory of the source (a burstable source may be offered shared types); a storage class is the one the draft names (the customer's answer or the variable's default), shown with the catalogue's own IOPS and throughput. The table states sizes; it is not a statement about the performance of the target against the source (no benchmark was run, and a CPU model that a side does not state is shown as not stated). The last six columns add, for a disk, the fee of the selected performance class (the cost model's own amount) with the assumption behind the class, whether the class covers the IOPS and throughput of the source volume, and the smaller classes of the catalogue that still cover them with their fee and change (an alternative with the same or better figures than the source; not a recommendation), and, for a server, whether the flavor is with or without CPU overprovisioning (the documentation's terms, by the overcommit the catalogue states) and what STACKIT states of its lifecycle (a deprecated type says so, with the sentence of the documentation). The size match columns state the comparison of a server's machine type with the source instance and of a database's PostgreSQL Flex flavor with the RDS instance class (vCPUs, memory and the kind, single node or replica set, against Multi-AZ) as proven, to review, not met or unknown, with the sentence that says what was compared; a basis names a size only where the size match is proven. | Yes | – |
financial/cost-coverage.md | What the cost model covers: the price sources it looked at, the lines by pricing state for each side, the totals with their state (full, partial or none), the comparison of source and target and why a saving is or is not given, the assumptions, and what the list prices of the STACKIT snapshot cover, with what is known of the terms of reuse of the price data. | Yes | – |
engineering/not-carried.csv | One row per property the draft names as not carried: the unit, the node and the property, what the assessment states about it (the class and closure of the critical-property gate, the draft's own reason, the contract semantic that reads it, what closes that semantic while it is open) and the place of the node in the source. A cell the assessment states nothing for is empty. | Yes | – |
engineering/not-carried-summary.csv | The units for which the draft names properties as not carried, with how many, and the units that have no count (their draft block was not accounted, or they need no resource of their own). | Yes | – |
engineering/evidence-index.json | The reverse table of the evidence index: one entry per block of the draft, with the units it comes from, whether it is an HCL block, a comment or not placed, and its file and line, with the hop table and the checks over the draft. workspace.json carries the tally of the entries and, on each unit, the forward hops; this file is the mirror of them, with the run it belongs to. | Yes | – |
engineering/trace/ | The full comment of each block of the Terraform draft that has one: the draft keeps a one-paragraph comment above the block (where it comes from, why its values are what they are, what is not carried, which decision is open) and a `# trace: TR-...` line, and the section of this folder that line names holds the whole comment the generators wrote, unabridged: the rule and knowledge-base stamp, the references with their digests, the evidence of each chosen value and the reason of each attribute that is not written. One file for each file of the draft that has such a block, named after it with the extension .md, one section for each block under an anchor that is its trace id; the blocks are linked to their file by `trace_file` and their anchor `trace_id` in engineering/evidence-index.json. This run wrote 8 files with 48 sections. | Yes | – |
engineering/trace-index.csv | One row per block with a trace: the trace id, the block, the draft file, the source units, the lines of the comment as the generators wrote it and the lines the draft keeps, and the pointer of the block (the trace file and the anchor of its section). | Yes | 11125 |
terraform/ | The proposed STACKIT Terraform. A draft: architect review is required before any use. Present only when the run produced it. | Yes | – |
terraform/README.md | How to read the draft: what was generated, what is left to a person, and how to check it with OpenTofu. | Yes | 45081 |
terraform/applications/carts.json | A file of the proposed STACKIT Terraform. | Yes | 13666 |
terraform/applications/carts.templates.yaml | A file of the proposed STACKIT Terraform. | Yes | 1370 |
terraform/applications/catalog.json | A file of the proposed STACKIT Terraform. | Yes | 15487 |
terraform/applications/catalog.templates.yaml | A file of the proposed STACKIT Terraform. | Yes | 1386 |
terraform/applications/checkout.json | A file of the proposed STACKIT Terraform. | Yes | 11130 |
terraform/applications/checkout.templates.yaml | A file of the proposed STACKIT Terraform. | Yes | 1394 |
terraform/applications/orders.json | A file of the proposed STACKIT Terraform. | Yes | 13896 |
terraform/applications/orders.templates.yaml | A file of the proposed STACKIT Terraform. | Yes | 1958 |
terraform/applications/ui.json | A file of the proposed STACKIT Terraform. | Yes | 6912 |
terraform/applications/ui.templates.yaml | A file of the proposed STACKIT Terraform. | Yes | 1346 |
terraform/data.tf | Proposed STACKIT resources of one area of the target (data). | Yes | 40322 |
terraform/handover/cache-dependencies_checkout_elasticache_redis_default/data-move.md | A file of the proposed STACKIT Terraform. | Yes | 30132 |
terraform/handover/cluster-access/kubeconfig.md | A file of the proposed STACKIT Terraform. | Yes | 5269 |
terraform/handover/database-dependencies_catalog_rds_this/data-move.md | A file of the proposed STACKIT Terraform. | Yes | 30820 |
terraform/handover/database-dependencies_orders_rds_this/data-move.md | A file of the proposed STACKIT Terraform. | Yes | 23836 |
terraform/handover/search-dependencies_catalog_opensearch_this/data-move.md | A file of the proposed STACKIT Terraform. | Yes | 16387 |
terraform/handover/table-dependencies_dynamodb_carts_this/data-move.md | A file of the proposed STACKIT Terraform. | Yes | 16273 |
terraform/identity.tf | Proposed STACKIT resources of one area of the target (identity). | Yes | 35863 |
terraform/kubernetes.tf | Proposed STACKIT resources of one area of the target (kubernetes). | Yes | 9091 |
terraform/kubernetes/carts/manifests.yaml | A file of the proposed STACKIT Terraform. | Yes | 9388 |
terraform/kubernetes/catalog/manifests.yaml | A file of the proposed STACKIT Terraform. | Yes | 9675 |
terraform/kubernetes/checkout/manifests.yaml | A file of the proposed STACKIT Terraform. | Yes | 9459 |
terraform/kubernetes/orders/manifests.yaml | A file of the proposed STACKIT Terraform. | Yes | 10784 |
terraform/kubernetes/ui/manifests.yaml | A file of the proposed STACKIT Terraform. | Yes | 10834 |
terraform/loadbalancing.tf | Proposed STACKIT resources of one area of the target (loadbalancing). | Yes | 6549 |
terraform/messaging.tf | Proposed STACKIT resources of one area of the target (messaging). | Yes | 6499 |
terraform/network.tf | Proposed STACKIT resources of one area of the target (network). | Yes | 12996 |
terraform/observability.tf | Proposed STACKIT resources of one area of the target (observability). | Yes | 5182 |
terraform/security.tf | Proposed STACKIT resources of one area of the target (security). | Yes | 50469 |
terraform/terraform.tf | The OpenTofu and provider version requirements of the draft. | Yes | 439 |
terraform/variables.tf | The input variables of the draft: the values a person fills in. | Yes | 39928 |
target-plan.json | The canonical TargetPlans the draft was generated from, machine-readable: one plan for each family of the draft that is written from a plan (the security groups of each source cloud, routing, identity, log sources, servers), each with how the draft wrote every resource of it (a resource, a comment only, or a statement about a block another generator writes). The run read it back against the draft before it was published: every resource of a plan is, or is not, a block of the draft as the file says. Present only when the run produced the draft. | Yes | – |
execution/ | The execution package: execution/README.md is the entry point for carrying the migration out (the verdict for the resources with a typed plan and the draft files it does not cover, what is created, what is not migrated, the decisions, the credentials, the order of the steps, the OpenTofu and API commands, the manual steps, the checks and the rollback); execution/terraform/apply.md, one request file and one script per STACKIT API call under execution/api/, execution/manual/actions.md and execution/verify/checks.md beside it. A rendering of execution-plan.json and of nothing else; nothing in it has been run, and a script stops before it calls anything when its step waits for a decision. Present only when the run produced the draft. | Yes | – |
migration/execution-actions.csv | One row per step of execution-plan.json for a spreadsheet: id, phase, mode, source, target, dependencies, owner, status, file, risks, rollback, whether it is executable and the decisions it waits for. The steps to carry out, not the register of open items (migration/actions.csv). Present only when the run produced the draft. | Yes | – |
migration/work-packages.csv | One row per work package of the manual steps of execution-plan.json for a spreadsheet: the steps of one phase, one owner role and one kind of work that one person carries out together, with their number, the resources they touch, the decisions they rest on and wait for, the strictest state among them, their success conditions and the ids of the steps. Every manual step is in exactly one package; execution/README.md lists the same packages. Present only when the run produced the draft. | Yes | – |
architecture/network-security.mmd | The network and security view as a Mermaid flowchart, or, in an estate with more than 120 units in it, the partition map of the files under architecture/partitions/ (one box for each partition, the arrows between partitions counted, every unknown edge accounted for). Drawn from the TargetPlans of the draft and the assessment: the internet, public IPs, load balancers, networks, subnets, servers, databases, security groups and their rules, network ACLs and routing. A path the sources do not state is a dashed edge labelled unknown with its reason, never a connection that was not read. Present only when the run produced the draft. | Yes | – |
architecture/identity.mmd | The identity view as a Mermaid flowchart (an estate with more principals than a drawing keeps legible gets one sentence that names assurance/identity-transition.md, which lists every identity, instead of a drawing): the AWS principal, the decision the assessment and the plan hold for it, the STACKIT identity it moves to, the role assignment and its scope. A step the typed plan does not hold (the role assignment) is drawn as manual, and a step it leaves open is a dashed edge labelled unknown. Present only when the run produced the draft. | Yes | – |
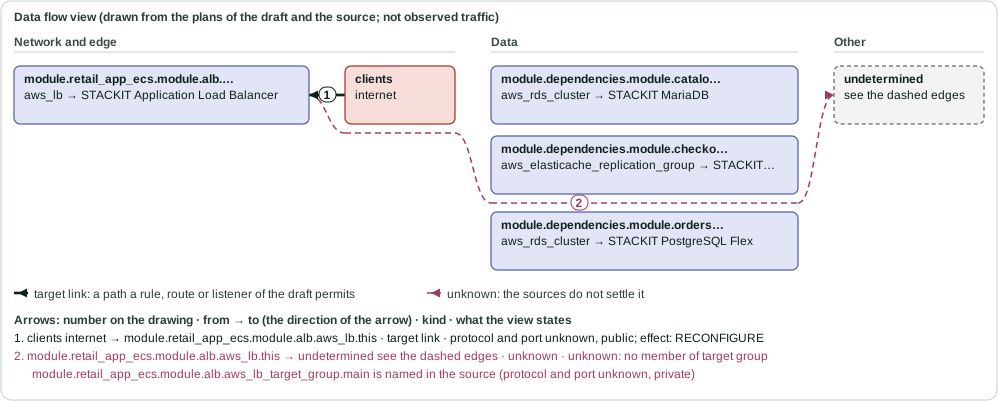
architecture/data-flows.mmd | The data flows as a Mermaid flowchart, or, in an estate with more than 120 units in it, the partition map of the files under architecture/partitions/ (one box for each partition, the arrows between partitions counted, every unknown edge accounted for): clients, load balancers, applications, databases, object storage and registries, with the protocol and port of each flow where the source states them, public or private, and the migration effect on the unit that carries it; what the source does not state is written unknown. The flows are the paths the listeners and security group rules permit, not observed traffic. Present only when the run produced the draft. | Yes | – |
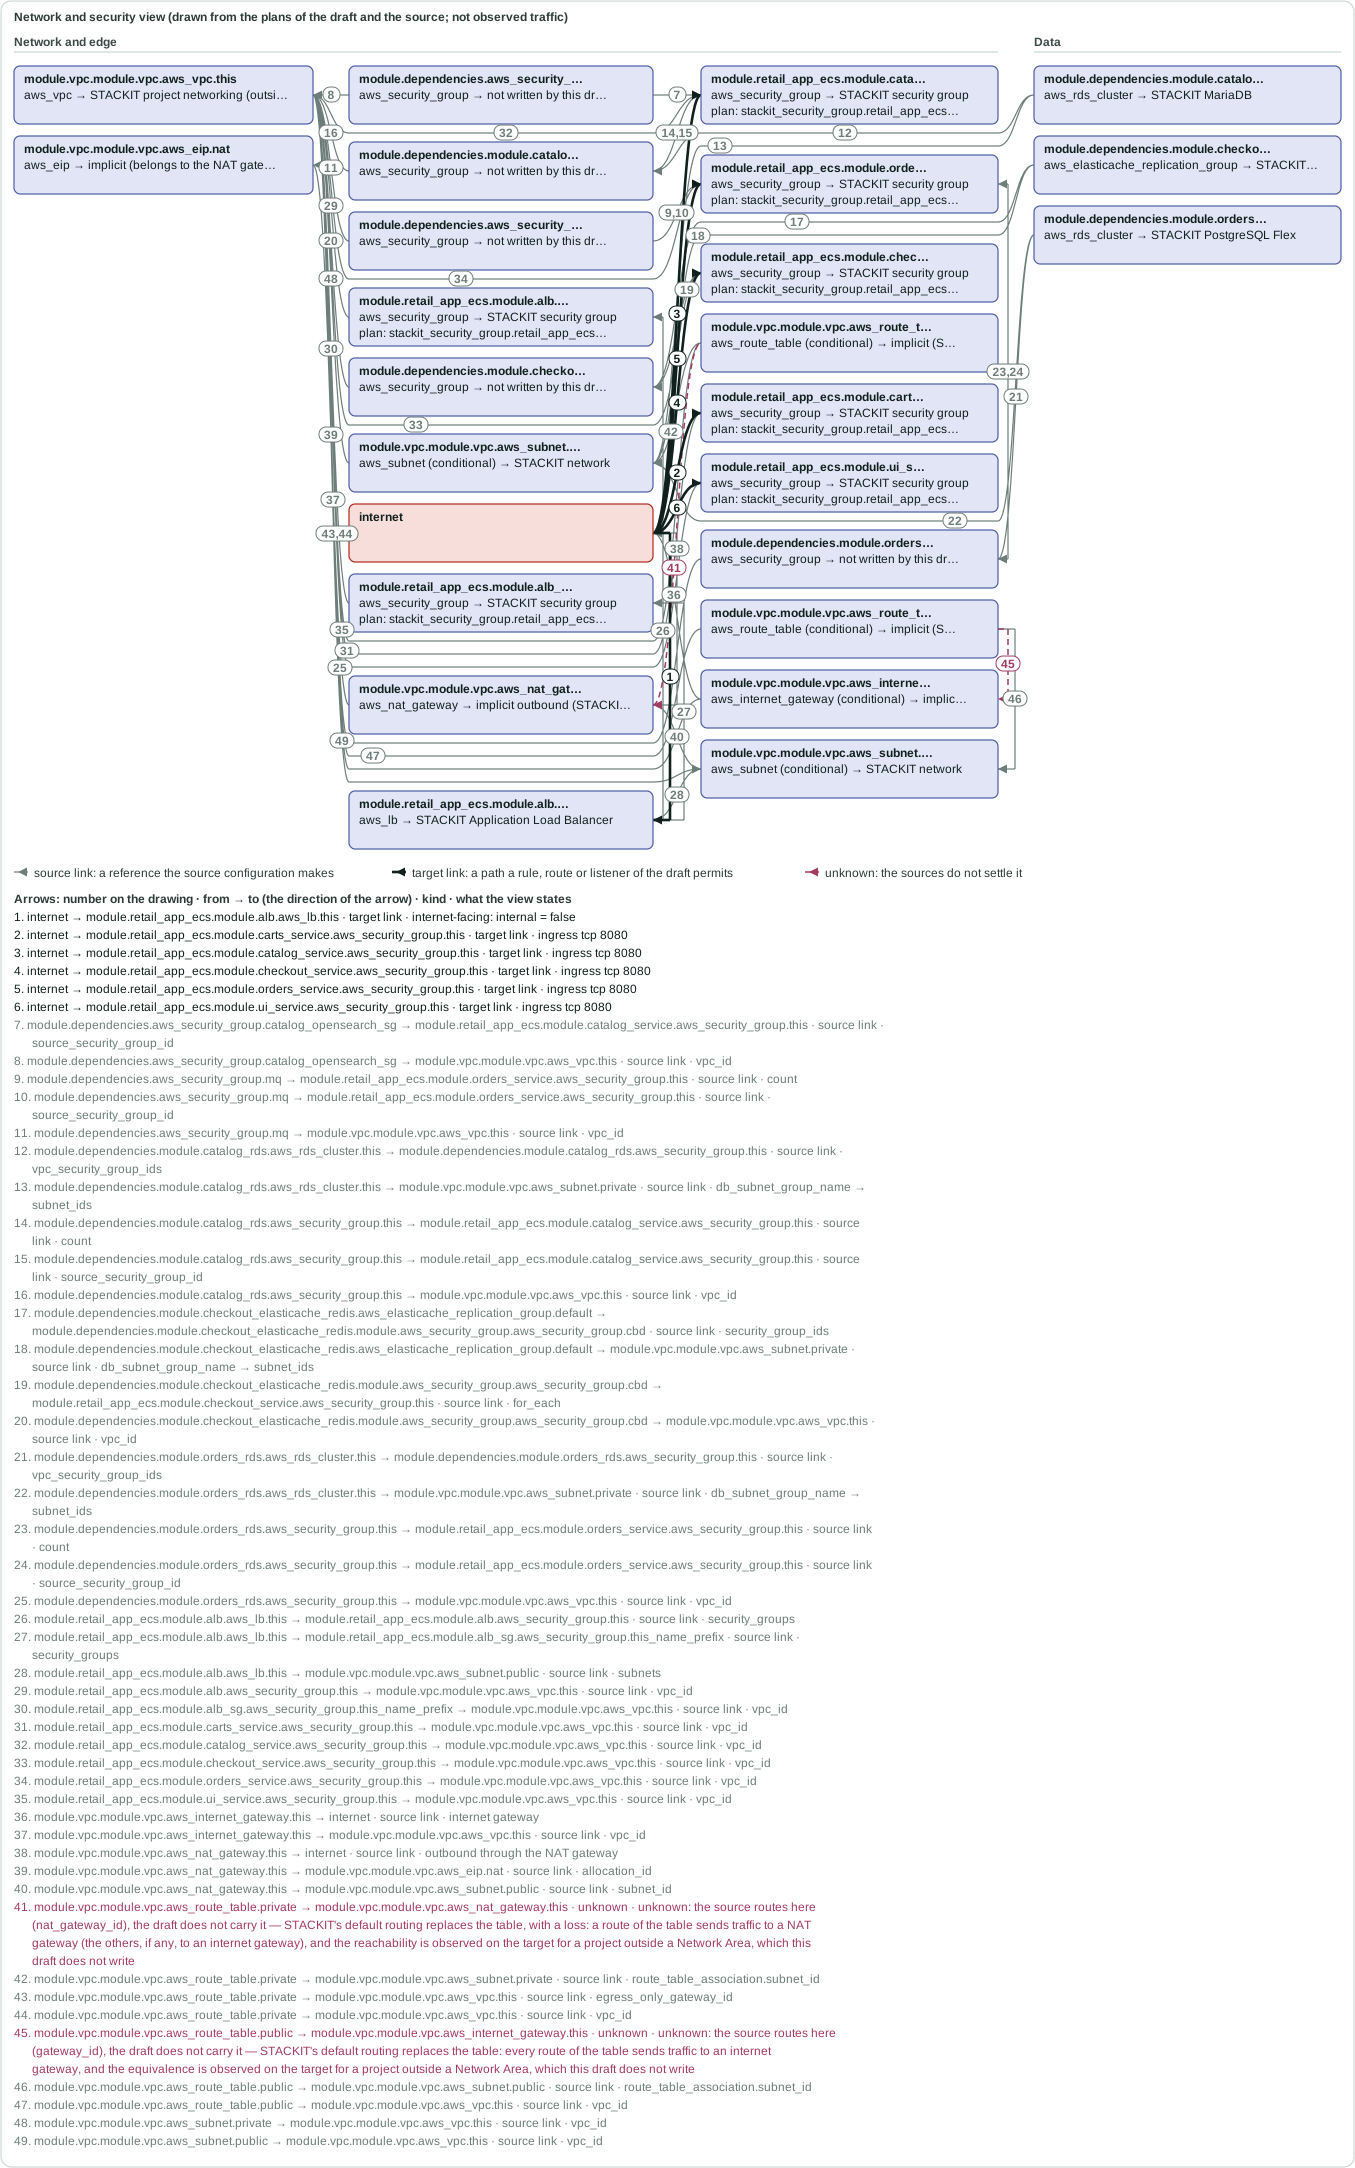
architecture/network-security.svg | The network and security view drawn offline: the same boxes and arrows as architecture/network-security.mmd, each arrow numbered, with a key that gives its two ends in the direction of the arrow and its words (protocol, port and direction of a rule; the attribute of a reference). Source links, target links (what a rule, route or listener of the draft permits), links an answer of the inputs file changed and unknowns are drawn apart and named in the legend. A view that is not drawn whole (a partition map above 120 units) is one sentence. Present only when the run produced the draft. | Yes | – |
architecture/data-flows.svg | The data flow view drawn offline: the same boxes and arrows as architecture/data-flows.mmd, each flow numbered, with a key that gives its two ends in the direction of the flow, its protocol and port, public or private, and the migration effect. Source links, target links and unknowns are drawn apart and named in the legend. A view that is not drawn whole (a partition map above 120 units) is one sentence. Present only when the run produced the draft. | Yes | – |
migration/roadmap.md | The execution plan laid out in ten waves: wave 0 the decisions some step waits for, then the landing zone, network and security, data services, platform, workloads, data migration, cutover, verification and decommission. Each step names what it does, the AWS resource, the mode, what it depends on and whether it is ready, blocked by a decision, not ready or refused. It holds the steps of execution-plan.json only. Present only when the run produced the draft. | Yes | – |
migration/landing-zone-requirements.md | What the STACKIT organization and project have to provide before the first apply: organization and project, network area and region, address ranges, routing, DNS, identity, service enablement, quotas to check, API access, Terraform permissions, external dependencies and the customer decisions. Read from the TargetPlans, the execution plan and the assessment; what they do not state is written as unknown and no limit or role name is invented. Present only when the run produced the draft. | Yes | – |
engineering/explain-index.json | Where, in this folder's files, the entries and ledger rows of each unit sit, as byte offsets: the explain command (stacktoit explain) reads a unit's chain from it without parsing the whole files. Machine-only: it is not an exchange document and states nothing the files it points into do not state; without it, or when it does not fit the files, explain reads them in full and prints the same answer. | Yes | – |
manifest.json | The run's identity (run id, source digest) and the list of the files it published, each with its sha256 and size; its status says whether the run is COMPLETE, PARTIAL or FAILED. | Yes | – |
migration/strategies.csv | Not produced in this build: a migration strategy for each application. No run writes this file, and nothing links to it. | No | – |
assurance/preflight.md | Not produced in this build: the preflight checks in words. No run writes this file, and nothing links to it. | No | – |
assurance/terraform-operability.md | Not produced in this build: how the draft is operated with OpenTofu. No run writes this file, and nothing links to it. | No | – |
financial/business-case.md | Not produced in this build: a business case. No run writes this file, and nothing links to it. | No | – |
financial/finops-readiness.md | Not produced in this build: the FinOps readiness. No run writes this file, and nothing links to it. | No | – |
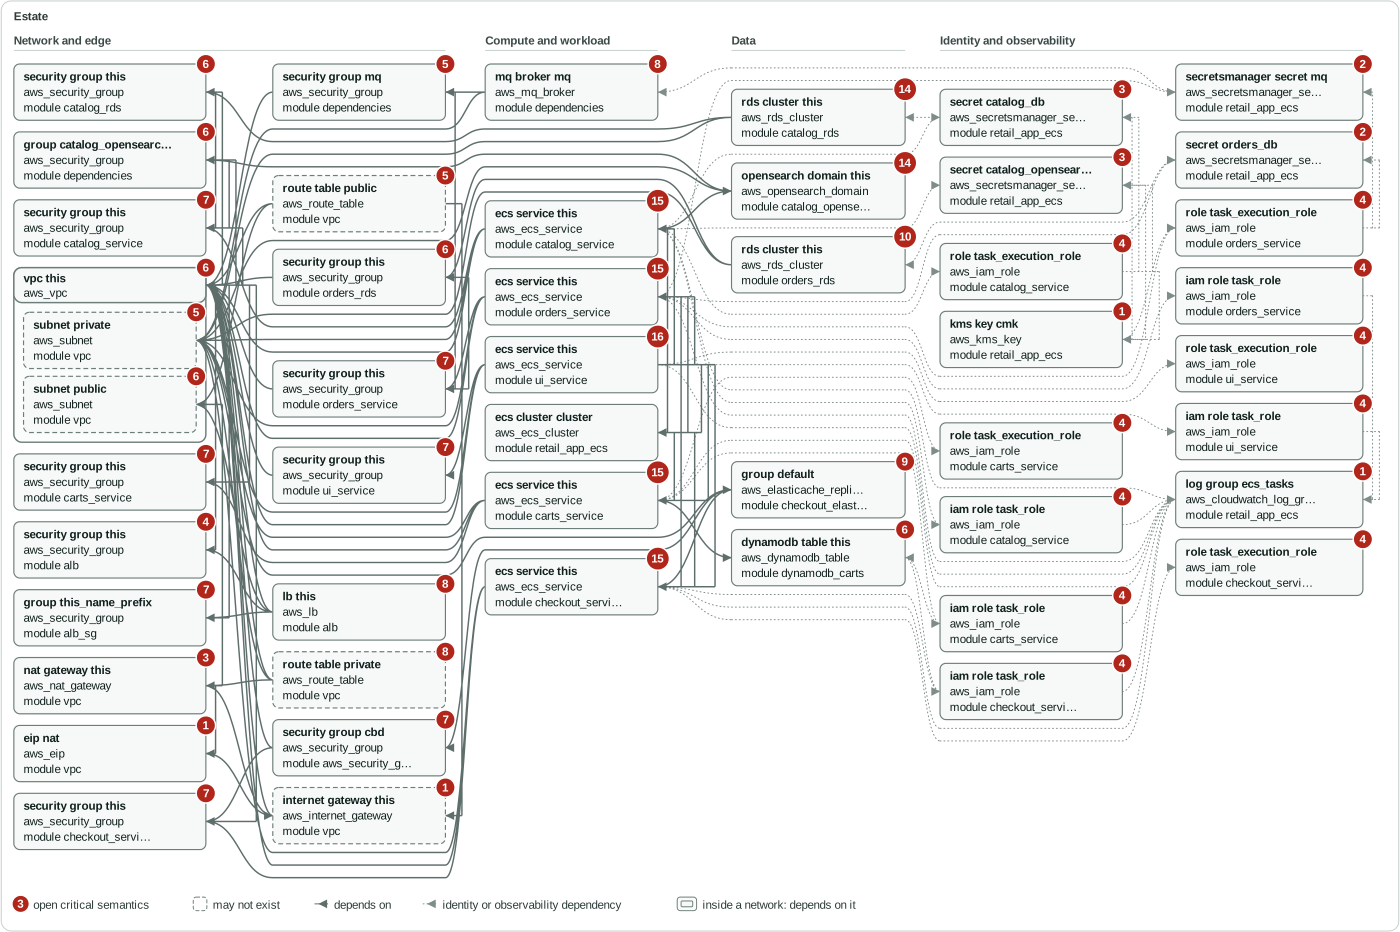
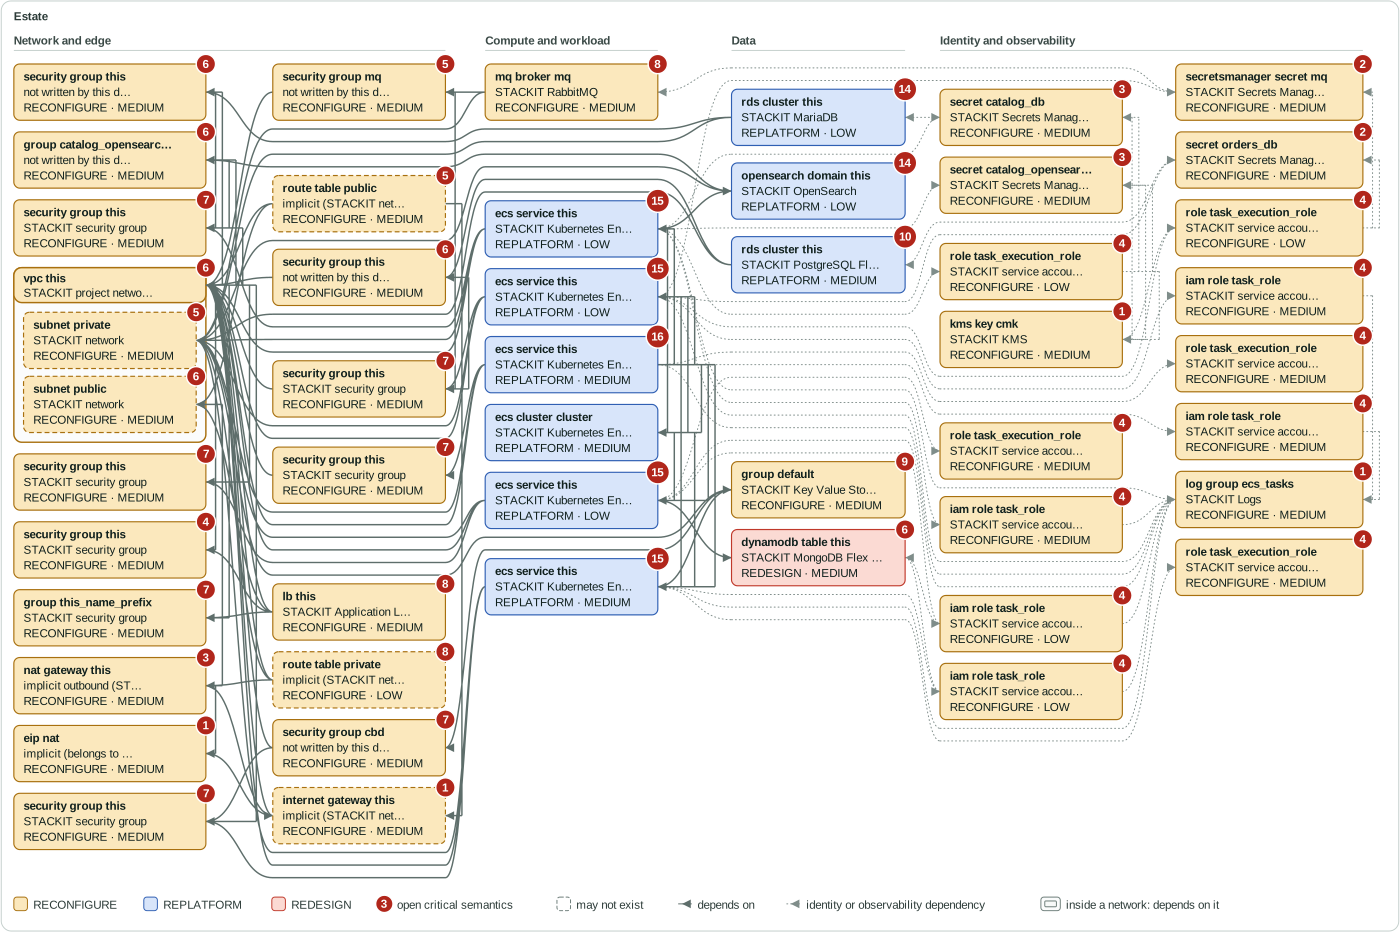
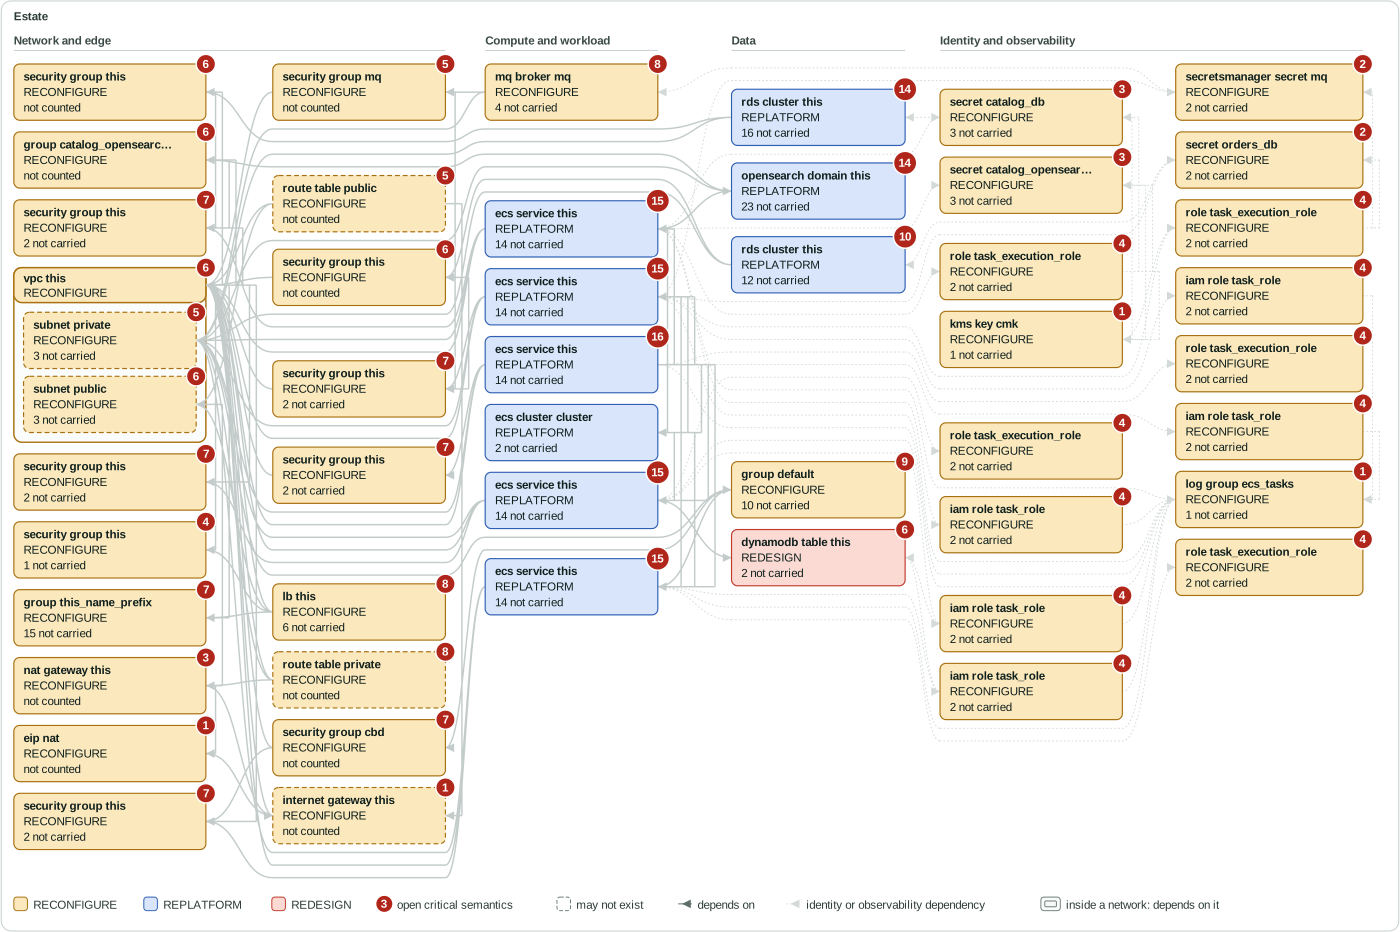
Evidence traces
Each drawer follows one resource from the source to its STACKIT target: source, evidence, resolution proof, semantic claim, intent, target capability, transformation, render, validation and the differences that remain. A step says what holds, what is open and where its machine artefact is. Nothing here is decided by this page. The expert view of a step lists the identifiers behind it.
module.dependencies.aws_mq_broker.mq
-
Source Established
module.dependencies.aws_mq_broker.mq is a resource of the source, declared in ../../lib/dependencies/mq.tf (lines 12-31). It is part of module.dependencies. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.dependencies.aws_mq_broker.mq (../../lib/dependencies/mq.tf:12) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/30
module.dependencies.aws_mq_broker.mq- knowledge base case: rabbitmq
- knowledge base rule: aws.mq_broker
- source type: aws_mq_broker
- unit: module.dependencies.aws_mq_broker.mq
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- the credential of the clients of stackit_rabbitmq_instance.dependencies_mq: the instance has no host, port, user or password attribute (pinned provider).
- host, hosts, port, username, password, uri, uris, management, http_api_uri and http_api_uris are computed attributes of this credential (password and uri are sensitive); the provider schema describes none of them.
- A RabbitMQ credential is a user of the whole instance: the broker users of the source (and their tags and permissions) are not copied, and the vhosts, queues and exchanges of the broker are created in the instance outside Terraform.
- STACKIT generates the password; the sensitive output dependencies_mq_rabbitmq_credential_password exposes it (a reference to this resource, never a value).
- Read it after the apply and give it to every client before the cutover; the state holds it in plain text and the draft creates no secret for it.
- DEFAULT plan_name: var.dependencies_mq_plan_name defaults to stackit-rabbitmq-8.16.50-replica (broker instance type mq.m5.large has 2 vCPU and 8 GiB (AWS price list, mq_broker_sizes.json), and the broker is a single instance: the smallest replica (three nodes, high availability) RabbitMQ plan of …
- The decision DEC-GEN-CONVERT-SIZE-FROM-SOURCE (alias `convert:module.dependencies.aws_mq_broker.mq:dependencies_mq_plan_name:SIZE_FROM_SOURCE`) stays open: check it, and answer choose-the-size in decisions.yaml if the plan is wrong; the next run then writes no default.
- DEFAULT: reachable on STACKIT from the egress addresses of stackit_ske_cluster.retail_app_ecs_cluster (its pods), the clients of this service, and from no other address; change the list with var.dependencies_mq_allowed_cidrs or answer the decision DEC-GEN-CONVERT-EXPOSURE-WIDENED (alias …
- and 3 further explanations of the values of the block; the trace file of the block holds all of them
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: engine-version-upgrade
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.mq_broker/rabbitmq · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-6212f52df434
- recorded: trace: TR-9aa24821e695
-
Semantic claim Open items
The engine read 14 statements the source makes about this resource and decided what happens to each; 14 of them are critical settings, 12 of those still open.
- 1 kept as it is
- 1 kept in another form
- 12 left to a person to review
- 30 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/30
module.dependencies.aws_mq_broker.mq- claim: broker-network = UNKNOWN, CRITICAL, REVIEW
- claim: broker-users = KNOWN, CRITICAL, REVIEW
- claim: engine = KNOWN, CRITICAL, TRANSFORMED
- claim: engine-type = KNOWN, CRITICAL, PRESERVED
- claim: engine-version = KNOWN, CRITICAL, REVIEW
- claim: network-exposure = KNOWN, CRITICAL, REVIEW
- claim: tc-mq-broker-broker-name = KNOWN, CRITICAL, REVIEW
- claim: tc-user--password = KNOWN, CRITICAL, REVIEW
- claim: tc-user--username = KNOWN, CRITICAL, REVIEW
- claim: tcp-deployment-mode = KNOWN, CRITICAL, REVIEW
- claim: tcp-engine-type = KNOWN, CRITICAL, REVIEW
- claim: tcp-engine-version = KNOWN, CRITICAL, REVIEW
- claim: tcp-security-groups = KNOWN, CRITICAL, REVIEW
- claim: tcp-subnet-ids = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_rabbitmq_credential.dependencies_mq: written as an active resource (terraform/messaging.tf, lines 34-37); the whole comment of the block is in engineering/trace/messaging.md
- stackit_rabbitmq_instance.dependencies_mq: written as an active resource (terraform/messaging.tf, lines 17-25); the whole comment of the block is in engineering/trace/messaging.md
In terraform/messaging.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/messaging.tf
stackit_rabbitmq_credential.dependencies_mq- block in the draft: stackit_rabbitmq_credential.dependencies_mq
- block in the draft: stackit_rabbitmq_instance.dependencies_mq
- block in the draft: terraform/messaging.tf:17-25
- block in the draft: terraform/messaging.tf:34-37
- trace: TR-6212f52df434
- trace: TR-9aa24821e695
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 2 findings, 2 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.dependencies.aws_mq_broker.mq): user — the broker users are not copied: the draft writes one stackit_rabbitmq_credential for the instance, a user whose username and password STACKIT generates (both computed, pinned provider) — clients get new credentials.
- NOT CARRIED (module.dependencies.aws_mq_broker.mq): apply_immediately = true — when a change reaches the broker is not carried: Amazon MQ applies a change in the next maintenance window unless apply_immediately applies it at once, with a brief downtime as the broker reboots (aws provider 6.66.0, …
- NOT CARRIED (module.dependencies.aws_mq_broker.mq): auto_minor_version_upgrade = true — the minor-version upgrade policy is not carried: Amazon MQ upgrades the broker to new minor versions as it releases them when auto_minor_version_upgrade is true (aws provider 6.66.0, aws_mq_broker), while …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: Engine version UPGRADE: the source runs RabbitMQ 3.13 (engine_version); STACKIT RabbitMQ in eu01 offers 4.1 (service catalogue of eu01, read 2026-10-18), none of them the source's version.
- 2 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-SIZE-FROM-SOURCE/module.dependencies.aws_mq_broker.mq(aliasconvert:module.dependencies.aws_mq_broker.mq:dependencies_mq_plan_name:SIZE_FROM_SOURCE) - decision:
DEC-GEN-CONVERT-EXPOSURE-WIDENED/module.dependencies.aws_mq_broker.mq(aliasconvert:module.dependencies.aws_mq_broker.mq:exposure:EXPOSURE_WIDENED)
module.dependencies.aws_security_group.catalog_opensearch_sg
-
Source Established
module.dependencies.aws_security_group.catalog_opensearch_sg is an AWS security group, declared in ../../lib/dependencies/catalog_opensearch.tf (lines 14-18). It is part of module.dependencies. It states 1 rule.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/23
module.dependencies.aws_security_group.catalog_opensearch_sg- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.aws_security_group.catalog_opensearch_sg
-
Evidence Open items
The source states 1 rule for this unit. 0 rules are stated exactly; 1 rule names a security group that is not proven.
- ingress tcp port 443 from a security group that is not resolved
In the source: ../../lib/dependencies/catalog_opensearch.tf, lines 14-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/dependencies/catalog_opensearch.tf lines 14-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.dependencies.aws_security_group_rule.allow_https_from_client
-
Resolution proof Open items
3 references are resolved for this unit: 1 proven, 1 named but not proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.aws_security_group.catalog_opensearch_sg: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the group of the rule resource module.dependencies.aws_security_group_rule.allow_https_from_client: refers to module.dependencies.aws_security_group.catalog_opensearch_sg, proven by a direct reference
- ingress tcp port 443 from a security group that is not resolved: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.dependencies.aws_security_group.catalog_opensearch_sg- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.dependencies.aws_security_group.catalog_opensearch_sg vpc_id
- proof cause: not-a-reference at module.dependencies.aws_security_group_rule.allow_https_from_client source_security_group_id
- proof: DIRECT_REFERENCE/EXACT at module.dependencies.aws_security_group_rule.allow_https_from_client security_group_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.dependencies.aws_security_group.catalog_opensearch_sg vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.aws_security_group_rule.allow_https_from_client source_security_group_id
-
Semantic claim Open items
The engine read 8 statements the source makes about this group and decided what happens to each; 8 of them are critical settings, 8 of those still open.
- 1 not supported on STACKIT
- 7 left to a person to review
- 108 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/23
module.dependencies.aws_security_group.catalog_opensearch_sg- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-not-generated = KNOWN, CRITICAL, REVIEW
- claim: standalone-rule-remote-not-resolved = UNKNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Established
The unit stands for 1 security group with 1 rule in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.aws_security_group.catalog_opensearch_sg: 1 rule
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.aws_security_group.catalog_opensearch_sg- intent family: SECURITY_POLICY
- intent: security:module.dependencies.aws_security_group.catalog_opensearch_sg
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this (stackit_opensearch_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
-
Residual difference Open items
The plan records 1 remaining difference between this unit and its STACKIT target. None is accepted yet.
- module.dependencies.aws_security_group.catalog_opensearch_sg: No STACKIT group is produced for this unit.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.dependencies.aws_security_group.catalog_opensearch_sg [group not produced]: source: an aws_security_group unit with 1 ingress, 0 egress and 0 other rules; target: no stackit_security_group and no rule is produced: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this (stackit_opensearch_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
module.dependencies.aws_security_group.mq
-
Source Established
module.dependencies.aws_security_group.mq is an AWS security group, declared in ../../lib/dependencies/mq.tf (lines 33-43). It is part of module.dependencies. It states 1 rule.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/24
module.dependencies.aws_security_group.mq- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.aws_security_group.mq
-
Evidence Open items
The source states 1 rule for this unit. 0 rules are stated exactly; 1 rule names a security group that is not proven.
- ingress tcp port 5671 from a security group that is not resolved
In the source: ../../lib/dependencies/mq.tf, lines 33-43.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/dependencies/mq.tf lines 33-43
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.dependencies.aws_security_group_rule.mq[0]
-
Resolution proof Open items
3 references are resolved for this unit: 1 proven, 1 named but not proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.aws_security_group.mq: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the group of the rule resource module.dependencies.aws_security_group_rule.mq[0]: refers to module.dependencies.aws_security_group.mq, proven by a direct reference
- ingress tcp port 5671 from a security group that is not resolved: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.dependencies.aws_security_group.mq- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.dependencies.aws_security_group.mq vpc_id
- proof cause: not-a-reference at module.dependencies.aws_security_group_rule.mq source_security_group_id
- proof: DIRECT_REFERENCE/EXACT at module.dependencies.aws_security_group_rule.mq security_group_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.dependencies.aws_security_group.mq vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.aws_security_group_rule.mq source_security_group_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 6 left to a person to review
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/24
module.dependencies.aws_security_group.mq- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-not-generated = KNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 1 rule in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.aws_security_group.mq: 1 rule
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.aws_security_group.mq- intent family: SECURITY_POLICY
- intent: security:module.dependencies.aws_security_group.mq
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.aws_mq_broker.mq (stackit_rabbitmq_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
-
Residual difference Open items
The plan records 1 remaining difference between this unit and its STACKIT target. None is accepted yet.
- module.dependencies.aws_security_group.mq: No STACKIT group is produced for this unit.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.dependencies.aws_security_group.mq [group not produced]: source: an aws_security_group unit with 1 ingress, 0 egress and 0 other rules; target: no stackit_security_group and no rule is produced: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.aws_mq_broker.mq (stackit_rabbitmq_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this
-
Source Established
module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this is a log group (a named store of log events with a retention of its own), declared in .terraform/modules/dependencies.catalog_opensearch/main.tf (lines 405-415). It is switched off in the source. It is part of module.dependencies.module.catalog_opensearch. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/44
module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this
-
Evidence Open items
The source states the retention and 0 settings and parts of this log group.
- The source states a retention that is stated
In the source: .terraform/modules/dependencies.catalog_opensearch/main.tf, lines 405-415.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.catalog_opensearch/main.tf lines 405-415
- retention key: retention_in_days
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states a retention that is stated
- The unit has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this- intent family: OBSERVABILITY
- intent: logs:module.dependencies.module.catalog_opensearch.aws_cloudwatch_log_group.this
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- provider version: 0.121.0
-
Transformation Established
No STACKIT resource is planned for this unit: the source creates no instance of it, switches it off, or states a destination that STACKIT Logs does not take, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the log source (count or for_each yields none, or it is switched off): no stackit_logs_instance is drafted
- plan producer: stacktoit-stackitlogs 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this
-
Source Established
module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this is a resource of the source, declared in .terraform/modules/dependencies.catalog_opensearch/main.tf (lines 29-233). It is part of module.dependencies.module.catalog_opensearch. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this (.terraform/modules/dependencies.catalog_opensearch/main.tf:29) — REPLATFORM / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/31
module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this- knowledge base case: opensearch
- knowledge base rule: aws.opensearch
- source type: aws_opensearch_domain
- unit: module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- the credential of the clients of stackit_opensearch_instance.dependencies_catalog_opensearch_this: the instance has no host, port, user or password attribute (pinned provider).
- host, hosts, port, scheme, username, password and uri are computed attributes of this credential (password and uri are sensitive); the provider schema gives host and hosts no description, so read both.
- STACKIT OpenSearch issues credentials with full access and has no per-principal or per-index permission: the access policy, the fine-grained users and the roles of the source are not copied; who may connect is the network list parameters.sgw_acl and whoever holds this credential.
- STACKIT generates the password; the sensitive output dependencies_catalog_opensearch_this_opensearch_credential_password exposes it (a reference to this resource, never a value).
- Read it after the apply and give it to every client before the cutover; the state holds it in plain text and the draft creates no secret for it.
- module.dependencies.module.catalog_opensearch.aws_opensearch_domain_saml_options.this: switched off in the source (count = 0); nothing of it is migrated unless it is switched on
- module.dependencies.module.catalog_opensearch.aws_opensearch_outbound_connection.this: switched off in the source (for_each = 0); nothing of it is migrated unless it is switched on
- module.dependencies.module.catalog_opensearch.aws_opensearch_package_association.this: switched off in the source (for_each = 0); nothing of it is migrated unless it is switched on
- and 6 further explanations of the values of the block; the trace file of the block holds all of them
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: engine-version-downgrade
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.opensearch/opensearch · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-5efbbe752c59
- recorded: trace: TR-71c158d59d3e
-
Semantic claim Open items
The engine read 14 statements the source makes about this resource and decided what happens to each; 14 of them are critical settings, 14 of those still open.
- 2 not supported on STACKIT
- 12 left to a person to review
- 21 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/31
module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this- claim: access-and-encryption-settings = KNOWN, CRITICAL, REVIEW
- claim: cluster-layout-settings = KNOWN, CRITICAL, REVIEW
- claim: credentials-and-keys-settings = KNOWN, CRITICAL, UNSUPPORTED
- claim: domain-credentials-and-keys = KNOWN, CRITICAL, UNSUPPORTED
- claim: domain-settings = KNOWN, CRITICAL, REVIEW
- claim: encryption-at-rest = KNOWN, CRITICAL, REVIEW
- claim: engine-version = KNOWN, CRITICAL, REVIEW
- claim: fine-grained-access = KNOWN, CRITICAL, REVIEW
- claim: nbr-aws-opensearch-domain-policy = KNOWN, CRITICAL, REVIEW
- claim: network-settings = KNOWN, CRITICAL, REVIEW
- claim: opensearch-domain-policy-resource = KNOWN, CRITICAL, REVIEW
- claim: private-endpoint = KNOWN, CRITICAL, REVIEW
- claim: storage-settings = KNOWN, CRITICAL, REVIEW
- claim: tc-opensearch-domain-domain-name = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_opensearch_credential.dependencies_catalog_opensearch_this: written as an active resource (terraform/data.tf, lines 221-224); the whole comment of the block is in engineering/trace/data.md
- stackit_opensearch_instance.dependencies_catalog_opensearch_this: written as an active resource (terraform/data.tf, lines 204-212); the whole comment of the block is in engineering/trace/data.md
In terraform/data.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/data.tf
stackit_opensearch_credential.dependencies_catalog_opensearch_this- block in the draft: stackit_opensearch_credential.dependencies_catalog_opensearch_this
- block in the draft: stackit_opensearch_instance.dependencies_catalog_opensearch_this
- block in the draft: terraform/data.tf:204-212
- block in the draft: terraform/data.tf:221-224
- trace: TR-5efbbe752c59
- trace: TR-71c158d59d3e
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 2 findings, 3 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this): cluster_config — the plan (plan_name) sets the size of a stackit_opensearch_instance (pinned provider): the cluster's instance types and counts, dedicated masters and zone awareness are not carried — choose the …
- NOT CARRIED (module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this): advanced_options, advanced_security_options, domain_endpoint_options, ebs_options, encrypt_at_rest, engine_version = OpenSearch_3.3, node_to_node_encryption, vpc_options — a stackit_opensearch_instance takes a …
- NOT CARRIED (module.dependencies.module.catalog_opensearch.aws_opensearch_domain_policy.this): access_policies — the access policy of the domain: Statement[0] allows any principal es:* (with a condition or a part that is not visible statically): a stackit_opensearch_instance grants access by …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- critical: Engine version DOWNGRADE: the source runs OpenSearch 3.3 (engine_version); STACKIT OpenSearch in eu01 offers 2 (service catalogue of eu01, read 2026-10-18), older than the source.
- 3 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-DATA-MOVEMENT/module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this(aliasconvert:module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this:data:DATA_MOVEMENT) - decision:
DEC-GEN-CONVERT-EXPOSURE-WIDENED/module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this(aliasconvert:module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this:exposure:EXPOSURE_WIDENED) - decision:
DEC-GEN-CONVERT-ENGINE-VERSION-DOWNGRADE(aliasconvert:module.dependencies.module.catalog_opensearch.aws_opensearch_domain.this:version:ENGINE_VERSION_DOWNGRADE)
module.dependencies.module.catalog_opensearch.aws_security_group.this
-
Source Established
module.dependencies.module.catalog_opensearch.aws_security_group.this is an AWS security group, declared in .terraform/modules/dependencies.catalog_opensearch/main.tf (lines 472-486). It is switched off in the source. It is part of module.dependencies.module.catalog_opensearch. It states 0 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/46
module.dependencies.module.catalog_opensearch.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.module.catalog_opensearch.aws_security_group.this
-
Evidence Established
The source states no rule for this unit.
In the source: .terraform/modules/dependencies.catalog_opensearch/main.tf, lines 472-486.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.catalog_opensearch/main.tf lines 472-486
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.module.catalog_opensearch.aws_security_group.this: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.dependencies.module.catalog_opensearch.aws_security_group.this- proof cause: source-not-present at module.dependencies.module.catalog_opensearch.aws_security_group.this vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.module.catalog_opensearch.aws_security_group.this vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Established
The unit stands for 1 security group with 0 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.module.catalog_opensearch.aws_security_group.this: 0 rules
- it has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.module.catalog_opensearch.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.dependencies.module.catalog_opensearch.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the group (count or for_each yields none, or it is switched off): no stackit_security_group is drafted
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this
-
Source Established
module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this is a log group (a named store of log events with a retention of its own), declared in .terraform/modules/dependencies.catalog_rds/main.tf (lines 445-453). It is switched off in the source. It is part of module.dependencies.module.catalog_rds. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/47
module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this
-
Evidence Open items
The source states the retention and 0 settings and parts of this log group.
- The source states a retention that is stated
In the source: .terraform/modules/dependencies.catalog_rds/main.tf, lines 445-453.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.catalog_rds/main.tf lines 445-453
- retention key: retention_in_days
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states a retention that is stated
- The unit has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this- intent family: OBSERVABILITY
- intent: logs:module.dependencies.module.catalog_rds.aws_cloudwatch_log_group.this
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- provider version: 0.121.0
-
Transformation Established
No STACKIT resource is planned for this unit: the source creates no instance of it, switches it off, or states a destination that STACKIT Logs does not take, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the log source (count or for_each yields none, or it is switched off): no stackit_logs_instance is drafted
- plan producer: stacktoit-stackitlogs 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.dependencies.module.catalog_rds.aws_rds_cluster.this
-
Source Established
module.dependencies.module.catalog_rds.aws_rds_cluster.this is a resource of the source, declared in .terraform/modules/dependencies.catalog_rds/main.tf (lines 61-169). It is part of module.dependencies.module.catalog_rds. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.dependencies.module.catalog_rds.aws_rds_cluster.this (.terraform/modules/dependencies.catalog_rds/main.tf:61) — REPLATFORM / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/32
module.dependencies.module.catalog_rds.aws_rds_cluster.this- knowledge base case: aurora-mysql
- knowledge base rule: aws.rds_cluster
- source type: aws_rds_cluster
- unit: module.dependencies.module.catalog_rds.aws_rds_cluster.this
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- the credential's username and password are computed by STACKIT (pinned provider); the source master username is not set.
- DEFAULT: STACKIT generates the password of this user (stackit_mariadb_credential.password is computed and sensitive, pinned provider; no STACKIT user takes a password) and the sensitive output dependencies_catalog_rds_this_admin_password exposes it; the source password and its Secrets Manager …
- STACKIT has no MySQL; test the application against MariaDB before cutover.
- REVIEW: the source is not proven publicly accessible, so the connectivity of the STACKIT instance is a decision: stackit_mariadb_instance has no private-network option in the pinned provider, its endpoint is public and limited by var.dependencies_catalog_rds_this_allowed_cidrs — an accepted change …
- DEFAULT: reachable on STACKIT from the egress addresses of stackit_ske_cluster.retail_app_ecs_cluster (its pods), the clients of this service, and from no other address; change the list with var.dependencies_catalog_rds_this_allowed_cidrs or answer the decision DEC-GEN-CONVERT-EXPOSURE-WIDENED …
- The clients are module.retail_app_ecs.module.catalog_service.aws_ecs_service.this, the members of module.retail_app_ecs.module.catalog_service.aws_security_group.this (named by module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress[0]), the only clients the source admitted; …
- module.dependencies.module.catalog_rds.aws_appautoscaling_policy.this: switched off in the source (count = 0); nothing of it is migrated unless it is switched on
- module.dependencies.module.catalog_rds.aws_appautoscaling_target.this: switched off in the source (count = 0); nothing of it is migrated unless it is switched on
- and 5 further explanations of the values of the block; the trace file of the block holds all of them
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: aurora-mysql-mariadb-auth
- recorded: finding: aurora-mysql-mariadb-collation
- recorded: finding: aurora-mysql-mariadb-json
- recorded: finding: aurora-mysql-mariadb-sql-mode
- recorded: finding: aurora-storage-encrypted-mariadb
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.rds_cluster/aurora-mysql · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-2fa350496480
- recorded: trace: TR-c392beafd341
-
Semantic claim Open items
The engine read 24 statements the source makes about this resource and decided what happens to each; 24 of them are critical settings, 20 of those still open.
- 1 kept as it is
- 19 left to a person to review
- 3 not applicable here
- 1 carried into the draft and listed in the ledger
- 89 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/32
module.dependencies.module.catalog_rds.aws_rds_cluster.this- claim: admin-password = UNKNOWN, CRITICAL, REVIEW
- claim: admin-username-not-carried = KNOWN, CRITICAL, REVIEW
- claim: backup-retention = KNOWN, CRITICAL, LEDGER
- claim: db-network-placement = UNKNOWN, CRITICAL, REVIEW
- claim: engine = KNOWN, CRITICAL, REVIEW
- claim: engine-version = KNOWN, CRITICAL, REVIEW
- claim: final-snapshot = KNOWN, CRITICAL, REVIEW
- claim: log-exports-none = KNOWN, CRITICAL, PRESERVED
- claim: member-engine = KNOWN, CRITICAL, REVIEW
- claim: member-settings = UNKNOWN, CRITICAL, REVIEW
- claim: multiaz-high-availability = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: multiaz-network-exposure = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: parameter-and-option-groups = UNKNOWN, CRITICAL, REVIEW
- claim: readable-standbys = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: security-groups = UNKNOWN, CRITICAL, REVIEW
- claim: storage-encryption = KNOWN, CRITICAL, REVIEW
- claim: tc-database-name = KNOWN, CRITICAL, REVIEW
- claim: tcf-rds-cluster-instance--identifier = KNOWN, CRITICAL, REVIEW
- claim: tcfp-rds-cluster-instance--engine = KNOWN, CRITICAL, REVIEW
- claim: tcfp-rds-cluster-instance--engine-version = KNOWN, CRITICAL, REVIEW
- claim: tcp-backup-retention-period = KNOWN, CRITICAL, REVIEW
- claim: tcp-db-cluster-parameter-group-name = KNOWN, CRITICAL, REVIEW
- claim: tcp-db-subnet-group-name = UNKNOWN, CRITICAL, REVIEW
- claim: tcp-vpc-security-group-ids = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_mariadb_credential.dependencies_catalog_rds_this: written as an active resource (terraform/data.tf, lines 49-52); the whole comment of the block is in engineering/trace/data.md
- stackit_mariadb_instance.dependencies_catalog_rds_this: written as an active resource (terraform/data.tf, lines 35-43); the whole comment of the block is in engineering/trace/data.md
In terraform/data.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/data.tf
stackit_mariadb_credential.dependencies_catalog_rds_this- block in the draft: stackit_mariadb_credential.dependencies_catalog_rds_this
- block in the draft: stackit_mariadb_instance.dependencies_catalog_rds_this
- block in the draft: terraform/data.tf:35-43
- block in the draft: terraform/data.tf:49-52
- trace: TR-2fa350496480
- trace: TR-c392beafd341
-
Residual difference Open items
The draft states, for this unit: 11 properties it does not carry, 1 open ledger row, 6 findings, 2 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress): source_security_group_id — the members of a security group the scan cannot name reach the source listener (port 3306) through this rule; the access list is a list of strings with no security-group …
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): db_subnet_group_name — stackit_mariadb_instance has no subnet, availability-zone or IP-family attribute (pinned provider): clients reach the instance at the endpoint STACKIT assigns.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): port = 3306 — stackit_mariadb_instance has no port setting (pinned provider): clients use the port of the STACKIT endpoint.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): master_username = root — stackit_mariadb_credential takes no username: the username and the password are computed by STACKIT (pinned provider) — clients get new credentials.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): master_password — the source password is not copied: stackit_mariadb_credential has no password input, STACKIT generates it (the password is computed and sensitive, pinned provider) — hand the new one to the application.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): database_name = catalog — stackit_mariadb_instance has no database attribute (pinned provider): create the database after connecting.
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): preferred_maintenance_window = sun:05:00-sun:06:00, allow_major_version_upgrade = true, db_cluster_parameter_group_name — stackit_mariadb_instance has no maintenance window, version-upgrade policy, extended-support, …
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): backup_retention_period = 7, preferred_backup_window = 02:00-03:00 — stackit_mariadb_instance has no backup setting (pinned provider).
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster.this): skip_final_snapshot = true — stackit_mariadb_instance has no final-snapshot or delete-time backup-retention setting (pinned provider): the instance is deleted immediately (and its automated backups may be removed …
- NOT CARRIED (module.dependencies.module.catalog_rds.aws_rds_cluster_instance.this): identifier = (reads a variable; its default is not printed), db_subnet_group_name, preferred_maintenance_window = sun:05:00-sun:06:00, db_parameter_group_name — cluster members are not separate STACKIT resources — …
- and 1 further properties the draft does not carry; the trace file of the block holds all of them
- Ledger: backup retention: 7 days → service-managed backups, retention not set in this draft — REVIEW
- warning: Storage is encrypted at rest with an AWS-managed key.
- warning: The source engine is MySQL 8 and its accounts do not move.
- warning: MariaDB stores JSON as text, not in a binary format as MySQL: its JSON data type is an alias for LONGTEXT, so the JSON columns of the source become text columns and JSON values are compared as strings, where MySQL compares them as JSON values.
- warning: The defaults of the character set and the collation differ: MySQL 8.0 uses utf8mb4 and utf8mb4_0900_ai_ci, MariaDB 10.11 uses latin1 or utf8 and latin1_swedish_ci or utf8_general_ci, and MariaDB names utf8mb4_uca1400_ai_ci as the counterpart default only from 11.4.
- and 2 further findings; the trace file of the block holds all of them
- 2 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-DATA-MOVEMENT/module.dependencies.module.catalog_rds.aws_rds_cluster.this(aliasconvert:module.dependencies.module.catalog_rds.aws_rds_cluster.this:data:DATA_MOVEMENT) - decision:
DEC-GEN-CONVERT-EXPOSURE-WIDENED/module.dependencies.module.catalog_rds.aws_rds_cluster.this(aliasconvert:module.dependencies.module.catalog_rds.aws_rds_cluster.this:exposure:EXPOSURE_WIDENED)
module.dependencies.module.catalog_rds.aws_security_group.this
-
Source Established
module.dependencies.module.catalog_rds.aws_security_group.this is an AWS security group, declared in .terraform/modules/dependencies.catalog_rds/main.tf (lines 321-334). It is part of module.dependencies.module.catalog_rds. It states 1 rule.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/25
module.dependencies.module.catalog_rds.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.module.catalog_rds.aws_security_group.this
-
Evidence Open items
The source states 1 rule for this unit. 0 rules are stated exactly; 1 rule names a security group that is not proven.
- ingress tcp port 3306 from a security group that is not resolved
In the source: .terraform/modules/dependencies.catalog_rds/main.tf, lines 321-334.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.catalog_rds/main.tf lines 321-334
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress[0]
-
Resolution proof Open items
3 references are resolved for this unit: 1 proven, 1 named but not proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.module.catalog_rds.aws_security_group.this[0]: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the group of the rule resource module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress[0]: refers to module.dependencies.module.catalog_rds.aws_security_group.this[0], proven by a reference to one instance
- ingress tcp port 3306 from a security group that is not resolved: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.dependencies.module.catalog_rds.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.dependencies.module.catalog_rds.aws_security_group.this vpc_id
- proof cause: not-a-reference at module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress source_security_group_id
- proof: INDEXED_REFERENCE/EXACT at module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress security_group_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.dependencies.module.catalog_rds.aws_security_group.this vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.module.catalog_rds.aws_security_group_rule.default_ingress source_security_group_id
-
Semantic claim Open items
The engine read 8 statements the source makes about this group and decided what happens to each; 8 of them are critical settings, 8 of those still open.
- 1 not supported on STACKIT
- 7 left to a person to review
- 108 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/25
module.dependencies.module.catalog_rds.aws_security_group.this- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-values = KNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 1 rule in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.module.catalog_rds.aws_security_group.this[0]: 1 rule
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.module.catalog_rds.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.dependencies.module.catalog_rds.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.catalog_rds.aws_rds_cluster.this (stackit_mariadb_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
-
Residual difference Open items
The plan records 1 remaining difference between this unit and its STACKIT target. None is accepted yet.
- module.dependencies.module.catalog_rds.aws_security_group.this: No STACKIT group is produced for this unit.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.dependencies.module.catalog_rds.aws_security_group.this [group not produced]: source: an aws_security_group unit with 1 ingress, 0 egress and 0 other rules; target: no stackit_security_group and no rule is produced: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.catalog_rds.aws_rds_cluster.this (stackit_mariadb_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default
-
Source Established
module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default is a resource of the source, declared in .terraform/modules/dependencies.checkout_elasticache_redis/main.tf (lines 115-164). It is part of module.dependencies.module.checkout_elasticache_redis. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default (.terraform/modules/dependencies.checkout_elasticache_redis/main.tf:115) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/33
module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default- knowledge base case: redis-valkey
- knowledge base rule: aws.elasticache
- source type: aws_elasticache_replication_group
- unit: module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- the credential of the clients of stackit_valkey_instance.dependencies_checkout_elasticache_redis_default: the instance has no host, port, user or password attribute (pinned provider).
- host, hosts, load_balanced_host, port, username, password and uri are computed attributes of this credential; the provider schema gives host and load_balanced_host no description, so read both.
- A service key authenticates fully against the instance; a test on a STACKIT project on 2026-09-24 found it denied CONFIG, ACL and MODULE (docs.stackit.cloud, Key Value Store, credentials). The AUTH token, the users and the ACL of the source are not copied: limits a client relied on move to …
- STACKIT generates the password; the sensitive output dependencies_checkout_elasticache_redis_default_valkey_credential_password exposes it (a reference to this resource, never a value).
- Read it after the apply and give it to every client before the cutover; the state holds it in plain text and the draft creates no secret for it.
- DEFAULT plan_name: var.dependencies_checkout_elasticache_redis_default_plan_name defaults to stackit-keyvalue-1.4.10-single (node type cache.t3.micro has 2 vCPU and 0.5 GiB (AWS price list, cache_node_sizes.json), and the source is a single node: the smallest single-node Key Value Store plan of the …
- The decision DEC-GEN-CONVERT-SIZE-FROM-SOURCE (alias `convert:module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default:dependencies_checkout_elasticache_redis_default_plan_name:SIZE_FROM_SOURCE`) stays open: check it, and answer choose-the-size in …
- REVIEW: reachable on STACKIT from the addresses of var.dependencies_checkout_elasticache_redis_default_allowed_cidrs instead of only from the private subnets (module.vpc.module.vpc.aws_subnet.private) — an accepted change in exposure, not a preserved property: decide it with the decision …
- and 6 further explanations of the values of the block; the trace file of the block holds all of them
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: engine-version-upgrade
- recorded: finding: redis-transit-encryption-off
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.elasticache/redis-valkey · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-31aa12c1dfa8
- recorded: trace: TR-6a8844a36ea2
-
Semantic claim Open items
The engine read 12 statements the source makes about this resource and decided what happens to each; 12 of them are critical settings, 11 of those still open.
- 1 kept in another form
- 11 left to a person to review
- 56 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/33
module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default- claim: at-rest-encryption-off = KNOWN, CRITICAL, REVIEW
- claim: engine-version = KNOWN, CRITICAL, TRANSFORMED
- claim: failover-off = KNOWN, CRITICAL, REVIEW
- claim: network-placement = UNKNOWN, CRITICAL, REVIEW
- claim: parameter-group = UNKNOWN, CRITICAL, REVIEW
- claim: parameter-group-default = UNKNOWN, CRITICAL, REVIEW
- claim: seed-snapshot = KNOWN, CRITICAL, REVIEW
- claim: snapshots-off = KNOWN, CRITICAL, REVIEW
- claim: tc-elasticache-replication-group-replication-group-id = KNOWN, CRITICAL, REVIEW
- claim: tcp-elasticache-replication-group-at-rest-encryption-enabled = KNOWN, CRITICAL, REVIEW
- claim: tcp-elasticache-replication-group-num-cache-clusters = KNOWN, CRITICAL, REVIEW
- claim: tcp-elasticache-replication-group-transit-encryption-enabled = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_valkey_credential.dependencies_checkout_elasticache_redis_default: written as an active resource (terraform/data.tf, lines 175-178); the whole comment of the block is in engineering/trace/data.md
- stackit_valkey_instance.dependencies_checkout_elasticache_redis_default: written as an active resource (terraform/data.tf, lines 158-166); the whole comment of the block is in engineering/trace/data.md
In terraform/data.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/data.tf
stackit_valkey_credential.dependencies_checkout_elasticache_redis_default- block in the draft: stackit_valkey_credential.dependencies_checkout_elasticache_redis_default
- block in the draft: stackit_valkey_instance.dependencies_checkout_elasticache_redis_default
- block in the draft: terraform/data.tf:158-166
- block in the draft: terraform/data.tf:175-178
- trace: TR-31aa12c1dfa8
- trace: TR-6a8844a36ea2
-
Residual difference Open items
The draft states, for this unit: 7 properties it does not carry, 3 findings, 1 open item, 3 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): subnet_group_name, security_group_ids — stackit_valkey_instance has no subnet, security-group, zone or IP-family attribute (pinned provider); the draft limits access with …
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): port = 6379 — the port is the one stackit_valkey_credential returns (port is computed, pinned provider); clients switch to it.
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): maintenance_window = wed:03:00-wed:04:00, notification_topic_arn = "", data_tiering_enabled = false — stackit_valkey_instance has no maintenance window, minor-upgrade switch, notification …
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): snapshot_window = 06:30-07:30 — the snapshot time is not carried: stackit_valkey_instance takes parameters.snapshot (pinned provider), not generated — decide it.
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): snapshot_arns — the instance is created empty: seeding it from an ElastiCache snapshot is not generated — migrate the data (e.g. RDB export and import, or replication).
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): parameter_group_name — the parameter group is not translated: stackit_valkey_instance takes selected settings under parameters (maxmemory_policy, maxclients, notify_keyspace_events, …; …
- NOT CARRIED (module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default): num_cache_clusters = 1 — the plan (plan_name) defines the nodes and replicas of a STACKIT Valkey instance (pinned provider).
- warning: The source cache runs without TLS (transit_encryption_enabled = false).
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: Engine version UPGRADE: the source runs Valkey 4.0.10 (engine_version); STACKIT Valkey in eu01 offers 8 (service catalogue of eu01, read 2026-10-18), none of them the source's version.
- Open: parameters.sgw_acl is set from var.dependencies_checkout_elasticache_redis_default_allowed_cidrs, which has no default: without a list STACKIT applies its default ACL, every STACKIT customer's addresses. List the clients' CIDRs before planning.
- 3 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-DATA-MOVEMENT/module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default(aliasconvert:module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default:data:DATA_MOVEMENT) - decision:
DEC-GEN-CONVERT-SIZE-FROM-SOURCE/module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default(aliasconvert:module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default:dependencies_checkout_elasticache_redis_default_plan_name:SIZE_FROM_SOURCE) - decision:
DEC-GEN-CONVERT-EXPOSURE-WIDENED/module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default(aliasconvert:module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default:exposure:EXPOSURE_WIDENED)
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd
-
Source Established
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd is an AWS security group, declared in .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf (lines 81-139). It is part of module.dependencies.module.checkout_elasticache_redis.module.aws_security_group. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/26
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd
-
Evidence Open items
The source states 2 rules for this unit. 1 rule is stated exactly; 1 has a value that is not visible statically and is never read as permissive.
- egress any protocol to 0.0.0.0/0, ::/0
- ingress tcp port 6379 from a source that is not visible statically
In the source: .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf, lines 81-139.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf lines 81-139
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed["_allow_all_egress_"]
- source rule: module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed["in#in#sg#0"]
-
Resolution proof Open items
3 references are resolved for this unit: 0 proven, 1 named but not proven, 2 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd[0]: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the group of the rule resource module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed["_allow_all_egress_"]: no resource could be named, so the reference is not resolved
- the group of the rule resource module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed["in#in#sg#0"]: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd vpc_id
- proof cause: not-a-reference at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed security_group_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group_rule.keyed security_group_id
-
Semantic claim Open items
The engine read 10 statements the source makes about this group and decided what happens to each; 9 of them are critical settings, 9 of those still open.
- 1 not supported on STACKIT
- 8 left to a person to review
- 1 not applicable here
- 106 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/26
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: revoke-rules-on-delete = KNOWN, NON_CRITICAL, NOT_APPLICABLE
- claim: rule-ports = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-empty-sources = KNOWN, CRITICAL, REVIEW
- claim: standalone-rule-other-sources = KNOWN, CRITICAL, REVIEW
- claim: standalone-rule-values = KNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd[0]: 2 rules
- 1 set whose members are not all visible statically
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd- intent family: SECURITY_POLICY
- intent: security:module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default (stackit_valkey_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
-
Residual difference Open items
The plan records 1 remaining difference between this unit and its STACKIT target. None is accepted yet.
- module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd: No STACKIT group is produced for this unit.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.cbd [group not produced]: source: an aws_security_group unit with 1 ingress, 1 egress and 0 other rules; target: no stackit_security_group and no rule is produced: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.checkout_elasticache_redis.aws_elasticache_replication_group.default (stackit_valkey_instance, access list parameters.sgw_acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default
-
Source Established
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default is an AWS security group, declared in .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf (lines 24-79). It is switched off in the source. It is part of module.dependencies.module.checkout_elasticache_redis.module.aws_security_group. It states 0 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/51
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default
-
Evidence Established
The source states no rule for this unit.
In the source: .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf, lines 24-79.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.checkout_elasticache_redis.aws_security_group/main.tf lines 24-79
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default- proof cause: source-not-present at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Established
The unit stands for 1 security group with 0 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default: 0 rules
- it has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default- intent family: SECURITY_POLICY
- intent: security:module.dependencies.module.checkout_elasticache_redis.module.aws_security_group.aws_security_group.default
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the group (count or for_each yields none, or it is switched off): no stackit_security_group is drafted
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this
-
Source Established
module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this is a resource of the source, declared in .terraform/modules/dependencies.dynamodb_carts/main.tf (lines 1-86). It is part of module.dependencies.module.dynamodb_carts. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/0
module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this- knowledge base case: dynamodb
- knowledge base rule: aws.dynamodb_table
- source type: aws_dynamodb_table
- unit: module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- ALTERNATIVE, NOT AN EQUIVALENT: DynamoDB (1 table(s)) → one MongoDB Flex instance, each table a collection — rule aws.dynamodb_table/dynamodb · REDESIGN / MEDIUM · KB 0.384.0 · review required.
- The data access layer is rewritten against the MongoDB API; move the data with an export (DynamoDB export to S3 → mongoimport) — nothing replicates it.
- replicas = 3 / Replica: DynamoDB replicates every table across several availability zones of its region; a 3-member replica set keeps redundancy within the STACKIT region.
- backup_schedule is a default (02:00 daily): DynamoDB on-demand backups and AWS Backup plans do not map one to one.
- TABLE module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this (.terraform/modules/dependencies.dynamodb_carts/main.tf:1) → collection "retail-store-ecs-carts": key id → _id (or a unique index on id); GSI idx_global_customerId {customerId: 1} → secondary index (strongly consistent in …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: trace: TR-a2c77bb1d7ef
-
Semantic claim Open items
The engine read 8 statements the source makes about this resource and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 7 left to a person to review
- 36 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/0
module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this- claim: capacity-mode = KNOWN, NON_CRITICAL, UNSUPPORTED
- claim: encryption-at-rest = KNOWN, CRITICAL, REVIEW
- claim: index-projection-and-name = KNOWN, CRITICAL, REVIEW
- claim: key-schema = KNOWN, CRITICAL, REVIEW
- claim: point-in-time-recovery = KNOWN, CRITICAL, REVIEW
- claim: secondary-indexes = KNOWN, CRITICAL, REVIEW
- claim: tc-dynamodb-table-name = KNOWN, CRITICAL, REVIEW
- claim: ttl = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 1 block for this unit, written as active Terraform.
- stackit_mongodbflex_instance.dynamodb_tables: written as an active resource (terraform/data.tf, lines 242-261); the whole comment of the block is in engineering/trace/data.md
In terraform/data.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/data.tf
stackit_mongodbflex_instance.dynamodb_tables- block in the draft: stackit_mongodbflex_instance.dynamodb_tables
- block in the draft: terraform/data.tf:242-261
- trace: TR-a2c77bb1d7ef
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED: capacity modes (provisioned/on-demand, auto scaling — size the flavor instead), DynamoDB Streams (use change streams or an outbox), transaction semantics (TransactWriteItems limits; MongoDB multi-document transactions behave differently), conditional-write expressions, PartiQL, table …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-DATA-MOVEMENT/module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this(aliasconvert:module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this:data:DATA_MOVEMENT)
module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this
-
Source Established
module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this is a log group (a named store of log events with a retention of its own), declared in .terraform/modules/dependencies.orders_rds/main.tf (lines 445-453). It is switched off in the source. It is part of module.dependencies.module.orders_rds. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/55
module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this
-
Evidence Open items
The source states the retention and 0 settings and parts of this log group.
- The source states a retention that is stated
In the source: .terraform/modules/dependencies.orders_rds/main.tf, lines 445-453.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.orders_rds/main.tf lines 445-453
- retention key: retention_in_days
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states a retention that is stated
- The unit has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this- intent family: OBSERVABILITY
- intent: logs:module.dependencies.module.orders_rds.aws_cloudwatch_log_group.this
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- provider version: 0.121.0
-
Transformation Established
No STACKIT resource is planned for this unit: the source creates no instance of it, switches it off, or states a destination that STACKIT Logs does not take, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the log source (count or for_each yields none, or it is switched off): no stackit_logs_instance is drafted
- plan producer: stacktoit-stackitlogs 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.dependencies.module.orders_rds.aws_rds_cluster.this
-
Source Established
module.dependencies.module.orders_rds.aws_rds_cluster.this is a resource of the source, declared in .terraform/modules/dependencies.orders_rds/main.tf (lines 61-169). It is part of module.dependencies.module.orders_rds. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.dependencies.module.orders_rds.aws_rds_cluster.this (.terraform/modules/dependencies.orders_rds/main.tf:61) — REPLATFORM / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/34
module.dependencies.module.orders_rds.aws_rds_cluster.this- knowledge base case: aurora-postgres
- knowledge base rule: aws.rds_cluster
- source type: aws_rds_cluster
- unit: module.dependencies.module.orders_rds.aws_rds_cluster.this
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- owner: the generated master user — the source states no database owner; check that the application expects this one.
- the owner is a user with the login role only: STACKIT accepted that at create (observed on a STACKIT project on 2026-10-15), but its API does not show a database's owner (the database list returns options: null, reading one database is a 404), so whether the owner is applied in the database is …
- flavor_id 2.4 = 2 vCPU / 4 GiB, single-node (eu01 catalogue 2026-10-18).
- REVIEW: the source is not proven publicly accessible, so the connectivity of the STACKIT instance is a decision: its endpoint is public and limited by the list you give — an accepted change in exposure, not a preserved property.
- DEFAULT: reachable on STACKIT from the egress addresses of stackit_ske_cluster.retail_app_ecs_cluster (its pods), the clients of this service, and from no other address; change the list with var.dependencies_orders_rds_this_allowed_cidrs or answer the decision DEC-GEN-CONVERT-EXPOSURE-WIDENED …
- The clients are module.retail_app_ecs.module.orders_service.aws_ecs_service.this, the members of module.retail_app_ecs.module.orders_service.aws_security_group.this (named by module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress[0]), the only clients the source admitted; the …
- PITR on PostgreSQL Flex restores into a new cloned instance; backups are kept 32–90 days.
- module.dependencies.module.orders_rds.aws_appautoscaling_policy.this: switched off in the source (count = 0); nothing of it is migrated unless it is switched on
- and 10 further explanations of the values of the block; the trace file of the block holds all of them
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: aurora-storage-encrypted
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.rds_cluster/aurora-postgres · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-7bc47518665f
- recorded: trace: TR-8ede34dda579
- recorded: trace: TR-e7d38d4bcda5
-
Semantic claim Open items
The engine read 25 statements the source makes about this resource and decided what happens to each; 25 of them are critical settings, 16 of those still open.
- 4 kept as it is
- 1 kept in another form
- 16 left to a person to review
- 3 not applicable here
- 1 carried into the draft and listed in the ledger
- 88 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/34
module.dependencies.module.orders_rds.aws_rds_cluster.this- claim: admin-password = UNKNOWN, CRITICAL, REVIEW
- claim: admin-username-not-carried = KNOWN, CRITICAL, REVIEW
- claim: aurora-extras = KNOWN, CRITICAL, PRESERVED
- claim: backup-retention = KNOWN, CRITICAL, LEDGER
- claim: db-network-placement = UNKNOWN, CRITICAL, REVIEW
- claim: engine = KNOWN, CRITICAL, TRANSFORMED
- claim: engine-version = KNOWN, CRITICAL, PRESERVED
- claim: final-snapshot = KNOWN, CRITICAL, REVIEW
- claim: log-exports-none = KNOWN, CRITICAL, PRESERVED
- claim: member-engine = KNOWN, CRITICAL, PRESERVED
- claim: member-settings = UNKNOWN, CRITICAL, REVIEW
- claim: multiaz-high-availability = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: multiaz-network-exposure = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: parameter-and-option-groups = UNKNOWN, CRITICAL, REVIEW
- claim: readable-standbys = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: security-groups = UNKNOWN, CRITICAL, REVIEW
- claim: storage-encryption = KNOWN, CRITICAL, REVIEW
- claim: tc-database-name = KNOWN, CRITICAL, REVIEW
- claim: tcf-rds-cluster-instance--identifier = KNOWN, CRITICAL, REVIEW
- claim: tcfp-rds-cluster-instance--engine = KNOWN, CRITICAL, REVIEW
- claim: tcfp-rds-cluster-instance--engine-version = KNOWN, CRITICAL, REVIEW
- claim: tcp-backup-retention-period = KNOWN, CRITICAL, REVIEW
- claim: tcp-db-cluster-parameter-group-name = KNOWN, CRITICAL, REVIEW
- claim: tcp-db-subnet-group-name = UNKNOWN, CRITICAL, REVIEW
- claim: tcp-vpc-security-group-ids = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 3 blocks for this unit, written as active Terraform.
- stackit_postgresflex_database.dependencies_orders_rds_this_orders: written as an active resource (terraform/data.tf, lines 128-133); the whole comment of the block is in engineering/trace/data.md
- stackit_postgresflex_instance.dependencies_orders_rds_this: written as an active resource (terraform/data.tf, lines 89-104); the whole comment of the block is in engineering/trace/data.md
- stackit_postgresflex_user.dependencies_orders_rds_this: written as an active resource (terraform/data.tf, lines 110-115); the whole comment of the block is in engineering/trace/data.md
In terraform/data.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/data.tf
stackit_postgresflex_database.dependencies_orders_rds_this_orders- block in the draft: stackit_postgresflex_database.dependencies_orders_rds_this_orders
- block in the draft: stackit_postgresflex_instance.dependencies_orders_rds_this
- block in the draft: stackit_postgresflex_user.dependencies_orders_rds_this
- block in the draft: terraform/data.tf:110-115
- block in the draft: terraform/data.tf:128-133
- block in the draft: terraform/data.tf:89-104
- trace: TR-7bc47518665f
- trace: TR-8ede34dda579
- trace: TR-e7d38d4bcda5
-
Residual difference Open items
The draft states, for this unit: 8 properties it does not carry, 2 findings, 3 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress): source_security_group_id — the members of a security group the scan cannot name reach the source listener (port 5432) through this rule; the access list is a list of strings with no security-group reference …
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster.this): db_subnet_group_name — stackit_postgresflex_instance has no subnet, availability-zone or IP-family attribute (pinned provider): clients reach the instance at the endpoint STACKIT assigns.
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster.this): port = 5432 — stackit_postgresflex_instance has no port setting (pinned provider): clients use the port of the STACKIT endpoint.
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster.this): master_password — the source password is not copied: stackit_postgresflex_user has no password input, STACKIT generates it (the password is computed and sensitive, pinned provider) — hand the new one to the application.
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster.this): preferred_maintenance_window = sun:05:00-sun:06:00, allow_major_version_upgrade = false, db_cluster_parameter_group_name — stackit_postgresflex_instance has no maintenance window, version-upgrade policy, extended-support, …
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster.this): skip_final_snapshot = true — stackit_postgresflex_instance has no final-snapshot or delete-time backup-retention setting (pinned provider): the instance is deleted immediately (and its automated backups may be removed …
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster_instance.this): identifier = (reads a variable; its default is not printed), db_subnet_group_name, preferred_maintenance_window = sun:05:00-sun:06:00, db_parameter_group_name — cluster members are not separate STACKIT resources — …
- NOT CARRIED (module.dependencies.module.orders_rds.aws_rds_cluster_instance.this): monitoring_role_arn — Enhanced Monitoring, Performance Insights and Database Insights have no stackit_postgresflex_instance attribute (pinned provider) — decide how the database is monitored.
- warning: Storage is encrypted at rest with an AWS-managed key; the PostgreSQL Flex encryption block covers customer keys only (the pinned STACKIT provider) and STACKIT does not state the default without it: no STACKIT fact is documented, so at-rest encryption is UNKNOWN until the PostgreSQL Flex …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 3 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-DATA-MOVEMENT/module.dependencies.module.orders_rds.aws_rds_cluster.this(aliasconvert:module.dependencies.module.orders_rds.aws_rds_cluster.this:data:DATA_MOVEMENT) - decision:
DEC-GEN-CONVERT-SIZE-FROM-SOURCE/module.dependencies.module.orders_rds.aws_rds_cluster.this(aliasconvert:module.dependencies.module.orders_rds.aws_rds_cluster.this:dependencies_orders_rds_this_flavor_id:SIZE_FROM_SOURCE) - decision:
DEC-GEN-CONVERT-EXPOSURE-WIDENED/module.dependencies.module.orders_rds.aws_rds_cluster.this(aliasconvert:module.dependencies.module.orders_rds.aws_rds_cluster.this:exposure:EXPOSURE_WIDENED)
module.dependencies.module.orders_rds.aws_security_group.this
-
Source Established
module.dependencies.module.orders_rds.aws_security_group.this is an AWS security group, declared in .terraform/modules/dependencies.orders_rds/main.tf (lines 321-334). It is part of module.dependencies.module.orders_rds. It states 1 rule.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/27
module.dependencies.module.orders_rds.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.dependencies.module.orders_rds.aws_security_group.this
-
Evidence Open items
The source states 1 rule for this unit. 0 rules are stated exactly; 1 rule names a security group that is not proven.
- ingress tcp port 5432 from a security group that is not resolved
In the source: .terraform/modules/dependencies.orders_rds/main.tf, lines 321-334.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/dependencies.orders_rds/main.tf lines 321-334
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress[0]
-
Resolution proof Open items
3 references are resolved for this unit: 1 proven, 1 named but not proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.dependencies.module.orders_rds.aws_security_group.this[0]: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the group of the rule resource module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress[0]: refers to module.dependencies.module.orders_rds.aws_security_group.this[0], proven by a reference to one instance
- ingress tcp port 5432 from a security group that is not resolved: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.dependencies.module.orders_rds.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.dependencies.module.orders_rds.aws_security_group.this vpc_id
- proof cause: not-a-reference at module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress source_security_group_id
- proof: INDEXED_REFERENCE/EXACT at module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress security_group_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.dependencies.module.orders_rds.aws_security_group.this vpc_id
- proof: UNRESOLVED/NONE at module.dependencies.module.orders_rds.aws_security_group_rule.default_ingress source_security_group_id
-
Semantic claim Open items
The engine read 8 statements the source makes about this group and decided what happens to each; 8 of them are critical settings, 8 of those still open.
- 1 not supported on STACKIT
- 7 left to a person to review
- 108 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/27
module.dependencies.module.orders_rds.aws_security_group.this- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-values = KNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 1 rule in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.dependencies.module.orders_rds.aws_security_group.this[0]: 1 rule
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.dependencies.module.orders_rds.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.dependencies.module.orders_rds.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.orders_rds.aws_rds_cluster.this (stackit_postgresflex_instance, access list network.acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
-
Residual difference Open items
The plan records 1 remaining difference between this unit and its STACKIT target. None is accepted yet.
- module.dependencies.module.orders_rds.aws_security_group.this: No STACKIT group is produced for this unit.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.dependencies.module.orders_rds.aws_security_group.this [group not produced]: source: an aws_security_group unit with 1 ingress, 0 egress and 0 other rules; target: no stackit_security_group and no rule is produced: every unit that names the group is a managed data service of STACKIT, and a STACKIT data service has no security group (the pinned provider schema has no attribute that names one) and takes its clients from an access list of its own: module.dependencies.module.orders_rds.aws_rds_cluster.this (stackit_postgresflex_instance, access list network.acl). The group would be listed by no resource, so no stackit_security_group and no rule is drafted for it. What the group admitted reaches the access lists as addresses only, on the one endpoint port of the service: whether the clients of a rule are in the default of a list is stated on the block of the service (its DEFAULT line or its NOT CARRIED lines), and who may connect is the open decision EXPOSURE_WIDENED of the service; a rule whose clients no address names, or that reaches another port, is not carried. The egress rules of the group are about the outbound traffic of the instance itself, which a managed data service exposes no filter for: they are not carried
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights
-
Source Established
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights is a log group (a named store of log events with a retention of its own), declared in ../../lib/ecs/eventbridge.tf (lines 8-16). Whether it exists is decided only when OpenTofu plans. It is part of module.retail_app_ecs. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/58
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights
-
Evidence Open items
The source states the retention and 6 settings and parts of this log group.
- The source states a retention that is decided by a variable or only when OpenTofu plans
- protection against deletion: decided by a variable or only when OpenTofu plans
- a customer-managed encryption key: decided by a variable or only when OpenTofu plans
- a storage or access class: decided by a variable or only when OpenTofu plans
- the name logs are written under: decided by a variable or only when OpenTofu plans
- the name logs are written under: decided by a variable or only when OpenTofu plans
- keeping the logs when the resource is destroyed: decided by a variable or only when OpenTofu plans
In the source: ../../lib/ecs/eventbridge.tf, lines 8-16.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/eventbridge.tf lines 8-16
- retention key: retention_in_days
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights deletion_protection_enabled (DELETION_PROTECTION) = CONDITIONAL
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights kms_key_id (KEY) = CONDITIONAL
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights log_group_class (CLASS) = CONDITIONAL
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights name (NAME) = CONDITIONAL
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights name_prefix (NAME) = CONDITIONAL
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights skip_destroy (KEEP_ON_DESTROY) = CONDITIONAL
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states a retention that is decided by a variable or only when OpenTofu plans
- How many instances of the unit exist is decided by a variable or only when OpenTofu plans
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights- intent family: OBSERVABILITY
- intent: logs:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_container_insights
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- provider version: 0.121.0
-
Transformation Established
No STACKIT resource is planned for this unit: the source creates no instance of it, switches it off, or states a destination that STACKIT Logs does not take, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the log source (count or for_each yields none, or it is switched off): no stackit_logs_instance is drafted
- plan producer: stacktoit-stackitlogs 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks
-
Source Established
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks is a log group (a named store of log events with a retention of its own), declared in ../../lib/ecs/cluster.tf (lines 10-12). It is part of module.retail_app_ecs. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/1
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks
-
Evidence Open items
The source states the retention and 1 setting or part of this log group.
- The source states no retention; the source then keeps its logs for ever
- the name logs are written under: decided by a variable or only when OpenTofu plans
In the source: ../../lib/ecs/cluster.tf, lines 10-12.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/cluster.tf lines 10-12
- retention key: retention_in_days
- setting: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks name (NAME) = CONDITIONAL
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Open items
The engine read 1 statement the source makes about this log source and decided what happens to each; 1 of them are critical settings, 1 of those still open.
- 1 left to a person to review
- 32 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/1
module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks- claim: tc-name = KNOWN, CRITICAL, REVIEW
-
Intent Established
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states no retention; the source then keeps its logs for ever
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks- intent family: OBSERVABILITY
- intent: logs:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- The plan of this unit relies on 4 evidenced facts about STACKIT:
- 2 about limits
- 2 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- constraint relied on: display-name-pattern (LIMIT, stackit_logs_instance.display_name)
- constraint relied on: no-log-group-or-stream-object (SEMANTIC, stackit_logs_instance)
- constraint relied on: retention-1-to-180-days (LIMIT, stackit_logs_instance.retention_days)
- constraint relied on: retention-is-per-instance (SEMANTIC, stackit_logs_instance.retention_days)
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 Logs instance for this unit. Of their 5 fields: 2 carried exactly, 1 needing a value you supply, 1 needing a manual action, 1 without a STACKIT equivalent.
- stackit_logs_instance.logs_retention_180d: node[module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks].retention_in_days has no STACKIT equivalent
- stackit_logs_instance.logs_retention_180d: node[module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks].name needs a manual action
- 3 manual actions, due before the cutover
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_logs_instance.logs_retention_180d- decision:
DEC-OPS-STACKITLOGS-RETENTION-OVER-180-DAYS(aliasstackitlogs:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks:retention_over_180_days) - field: stackit_logs_instance.logs_retention_180d.node[module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks].name = MANUAL_ACTION: the name the source writes to has no object on the target that can hold it
- field: stackit_logs_instance.logs_retention_180d.node[module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks].retention_in_days = UNSUPPORTED: the source keeps its logs for ever (it states no period, or 0); a Logs instance keeps at most 180 days, so the logs of this source are kept for 180 days here and anything older has to be archived elsewhere (for example in Object Storage) if it must be kept
- field: stackit_logs_instance.logs_retention_180d.project_id = VARIABLE_REQUIRED: the instance belongs to a STACKIT project
- manual action:
DEC-OPS-STACKITLOGS-ACTION-ARCHIVE-FLOW(aliasstackitlogs:archive:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks) (CUTOVER_PREREQUISITE): Configure a cold-storage log flow for module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks: send a copy of its logs, in parallel to the Logs instance stackit_logs_instance.logs_retention_180d, to a long-term store (for example a separate Object Storage bucket) that keeps them for the retention beyond 180 days - manual action:
DEC-OPS-STACKITLOGS-ACTION-LABEL-CONVENTION(aliasstackitlogs:label-convention:module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks) (CUTOVER_PREREQUISITE): Choose a static label and send the name of module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks (and of its streams) from its log producers as the value of that label - manual action:
DEC-OPS-STACKITLOGS-ACTION-TARGET-PRECONDITION(aliasstackitlogs:token:stackit_logs_instance.logs_retention_180d) (CUTOVER_PREREQUISITE): Before any log source writes to stackit_logs_instance.logs_retention_180d: create a write access token for the instance (stackit_logs_access_token with the permission write), set the access control list of the instance, and point the shipper at the instance's ingest_url (Loki API) or ingest_otlp_url (OpenTelemetry) - plan producer: stacktoit-stackitlogs 0.1.0
- plan rule: stackitlogs.instance
-
Render Established
The draft writes 1 resource of this unit as active Terraform.
- stackit_logs_instance.logs_retention_180d: written as an active resource (terraform/observability.tf, lines 19-23)
In terraform/observability.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/observability.tf
- block in the draft: terraform/observability.tf:19-23
- file the plan renders into: observability.tf
- resource address: stackit_logs_instance.logs_retention_180d
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every instance written as a resource names a project, a display name the API accepts and a retention of 1 to 180 days or a variable
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added
- Checked: the Logs instances of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_logs_instance reads back from the text as the plan states it: its project, its display name and its retention_days, the variable of an instance whose period is not visible, and no instance the plan does not carry
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the Logs instances of the written files read back as the plan (1 written resources, 3 attributes and 0 references compared in the final files)
- check: instance-complete ok=true: 1 instance block(s) written as resources, each with a project, a display name the API accepts and a retention_days of 1 to 180 days or a variable
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (1 written resources, 3 attributes and 0 references compared in the draft)
- validation requirement: alias
stackitlogs:round-trip(ROUND_TRIP)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks: STACKIT Logs has no log group, workspace or sink object: the source is not created as such, and its logs go to the Logs instance of its retention.
- module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks: A setting of the source has no STACKIT counterpart and is not carried (the longest period a Logs instance keeps is 180 days).
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks (LOG_GROUP) [group not produced]: source: a log group with its own name, settings and facets; target: its logs go to the Logs instance stackit_logs_instance.logs_retention_180d, a label-based store with no group or stream object
- residual: module.retail_app_ecs.aws_cloudwatch_log_group.ecs_tasks retention_in_days [no equivalent on STACKIT]: source: keeps its logs for ever; target: the instance keeps its logs for 180 days at most; older logs are not kept
module.retail_app_ecs.aws_ecs_cluster.cluster
-
Source Established
module.retail_app_ecs.aws_ecs_cluster.cluster is a resource of the source, declared in ../../lib/ecs/cluster.tf (lines 1-8). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.aws_ecs_cluster.cluster (../../lib/ecs/cluster.tf:1) — REPLATFORM / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/2
module.retail_app_ecs.aws_ecs_cluster.cluster- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_cluster
- unit: module.retail_app_ecs.aws_ecs_cluster.cluster
-
Evidence Nothing to show
The block stands for several units, so the generator's explanations of its values are not attributed to this unit; the trace file of the block holds them. These are the generator's own statements in the draft, not checks of the draft.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: trace: TR-364b2c550bbd
-
Semantic claim Nothing to show
The source makes no statement about this resource that is carried anywhere.
- 122 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/2
module.retail_app_ecs.aws_ecs_cluster.clusterNo identifiers.
-
Render Established
The draft holds 1 block for this unit, written as active Terraform.
- stackit_ske_cluster.retail_app_ecs_cluster: written as an active resource (terraform/kubernetes.tf, lines 36-46); it also stands for 5 other units; the whole comment of the block is in engineering/trace/kubernetes.md
In terraform/kubernetes.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/kubernetes.tf
stackit_ske_cluster.retail_app_ecs_cluster- block in the draft: stackit_ske_cluster.retail_app_ecs_cluster
- block in the draft: terraform/kubernetes.tf:36-46
- trace: TR-364b2c550bbd
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 2 open items. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_ecs_cluster.cluster): setting — an ECS cluster setting (container insights, execute-command logging, Service Connect defaults, tags) has no stackit_ske_cluster attribute (pinned provider): observability and the Service Connect namespace are decided on the …
- Open: the name of module.retail_app_ecs.aws_ecs_cluster.cluster is "retail-store-ecs-cluster": an SKE cluster name has 1 to 11 characters (lowercase letters, digits and hyphens) and is distinct in the draft (stackit-api-specifications ske/v2), so the draft names the cluster "reta-7b7ce2" — set the name …
- Open: the node pool's machine type, minimum and maximum replace the capacity of module.retail_app_ecs.aws_ecs_cluster.cluster (Fargate has no nodes): they are variables because the source does not state a node size — size them from the requests in kubernetes/<service>/manifests.yaml. An SKE node pool's …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.aws_kms_key.cmk
-
Source Established
module.retail_app_ecs.aws_kms_key.cmk is a resource of the source, declared in ../../lib/ecs/common.tf (lines 1-4). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.aws_kms_key.cmk (../../lib/ecs/common.tf:1) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/3
module.retail_app_ecs.aws_kms_key.cmk- knowledge base case: kms
- knowledge base rule: aws.kms_key
- source type: aws_kms_key
- unit: module.retail_app_ecs.aws_kms_key.cmk
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- access_scope is var.kms_access_scope, which has no default: without it the STACKIT API makes the key PUBLIC, a choice the source does not state. PUBLIC or SNA is yours.
- display_name made a name the STACKIT KMS API takes (1 to 64 characters of letters, digits, underscores and hyphens); source text: retail-store-ecs CMK
- AWS key material cannot be exported: data encrypted with the old key is re-encrypted during migration.
- One keyring for the migrated keys.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.kms_key/kms · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-af9e2a025af8
- recorded: trace: TR-e47c9c2d3326
-
Semantic claim Open items
The engine read 1 statement the source makes about this resource and decided what happens to each; 1 of them are critical settings, 1 of those still open.
- 1 left to a person to review
- 47 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/3
module.retail_app_ecs.aws_kms_key.cmk- claim: deletion-window = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_kms_key.retail_app_ecs_cmk: written as an active resource (terraform/security.tf, lines 286-294); the whole comment of the block is in engineering/trace/security.md
- stackit_kms_keyring.migrated: written as an active resource (terraform/security.tf, lines 274-277); the whole comment of the block is in engineering/trace/security.md
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
stackit_kms_key.retail_app_ecs_cmk- block in the draft: stackit_kms_key.retail_app_ecs_cmk
- block in the draft: stackit_kms_keyring.migrated
- block in the draft: terraform/security.tf:274-277
- block in the draft: terraform/security.tf:286-294
- trace: TR-af9e2a025af8
- trace: TR-e47c9c2d3326
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_kms_key.cmk): deletion_window_in_days = 7 — STACKIT KMS deletes a key scheduled for deletion after 30 days; stackit_kms_key has no deletion window (pinned provider).
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.aws_secretsmanager_secret.catalog_db
-
Source Established
module.retail_app_ecs.aws_secretsmanager_secret.catalog_db is a resource of the source, declared in ../../lib/ecs/catalog.tf (lines 65-68). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/35
module.retail_app_ecs.aws_secretsmanager_secret.catalog_db- knowledge base case: secret
- knowledge base rule: aws.secretsmanager_secret
- source type: aws_secretsmanager_secret
- unit: module.retail_app_ecs.aws_secretsmanager_secret.catalog_db
-
Evidence Nothing to show
The block stands for several units, so the generator's explanations of its values are not attributed to this unit; the trace file of the block holds them. These are the generator's own statements in the draft, not checks of the draft.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: trace: TR-6003c14a24b3
- recorded: trace: TR-b77494749ed2
-
Semantic claim Open items
The engine read 3 statements the source makes about this resource and decided what happens to each; 3 of them are critical settings, 3 of those still open.
- 3 left to a person to review
- 31 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/35
module.retail_app_ecs.aws_secretsmanager_secret.catalog_db- claim: customer-managed-key = KNOWN, CRITICAL, REVIEW
- claim: secret-value = KNOWN, CRITICAL, REVIEW
- claim: tc-secretsmanager-secret-name = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_secretsmanager_instance.migrated_secrets: written as an active resource (terraform/security.tf, lines 317-320); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
- stackit_secretsmanager_user.migration: written as an active resource (terraform/security.tf, lines 325-330); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
stackit_secretsmanager_instance.migrated_secrets- block in the draft: stackit_secretsmanager_instance.migrated_secrets
- block in the draft: stackit_secretsmanager_user.migration
- block in the draft: terraform/security.tf:317-320
- block in the draft: terraform/security.tf:325-330
- trace: TR-6003c14a24b3
- trace: TR-b77494749ed2
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 1 finding, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.catalog_db): kms_key_id — the source encrypts with a customer-managed key that the draft does not set on the Secrets Manager instance: the instance also holds module.retail_app_ecs.aws_secretsmanager_secret.mq, which states no …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.catalog_db): name — the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.catalog_db writes it into the Secrets Manager instance from a document you supply (the path is its name when the source …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret_version.catalog_db): secret_id, secret_string — a setting of module.retail_app_ecs.aws_secretsmanager_secret.catalog_db: the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.catalog_db writes …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-API-OPT-IN(aliasconvert:api:secrets-manager-vault:v1:unknown:API_OPT_IN)
module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch
-
Source Established
module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch is a resource of the source, declared in ../../lib/ecs/catalog.tf (lines 82-85). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/9
module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch- knowledge base case: secret
- knowledge base rule: aws.secretsmanager_secret
- source type: aws_secretsmanager_secret
- unit: module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch
-
Evidence Nothing to show
The block stands for several units, so the generator's explanations of its values are not attributed to this unit; the trace file of the block holds them. These are the generator's own statements in the draft, not checks of the draft.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: trace: TR-6003c14a24b3
- recorded: trace: TR-b77494749ed2
-
Semantic claim Open items
The engine read 3 statements the source makes about this resource and decided what happens to each; 3 of them are critical settings, 3 of those still open.
- 3 left to a person to review
- 31 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/9
module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch- claim: customer-managed-key = KNOWN, CRITICAL, REVIEW
- claim: secret-value = KNOWN, CRITICAL, REVIEW
- claim: tc-secretsmanager-secret-name = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_secretsmanager_instance.migrated_secrets: written as an active resource (terraform/security.tf, lines 317-320); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
- stackit_secretsmanager_user.migration: written as an active resource (terraform/security.tf, lines 325-330); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
stackit_secretsmanager_instance.migrated_secrets- block in the draft: stackit_secretsmanager_instance.migrated_secrets
- block in the draft: stackit_secretsmanager_user.migration
- block in the draft: terraform/security.tf:317-320
- block in the draft: terraform/security.tf:325-330
- trace: TR-6003c14a24b3
- trace: TR-b77494749ed2
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 1 finding, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch): kms_key_id — the source encrypts with a customer-managed key that the draft does not set on the Secrets Manager instance: the instance also holds module.retail_app_ecs.aws_secretsmanager_secret.mq, which states no …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch): name — the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch writes it into the Secrets Manager instance from a document you supply (the path is its name …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret_version.catalog_opensearch): secret_id, secret_string — a setting of module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch: the API step …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-API-OPT-IN(aliasconvert:api:secrets-manager-vault:v1:unknown:API_OPT_IN)
module.retail_app_ecs.aws_secretsmanager_secret.mq
-
Source Established
module.retail_app_ecs.aws_secretsmanager_secret.mq is a resource of the source, declared in ../../lib/ecs/common.tf (lines 11-13). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/36
module.retail_app_ecs.aws_secretsmanager_secret.mq- knowledge base case: secret
- knowledge base rule: aws.secretsmanager_secret
- source type: aws_secretsmanager_secret
- unit: module.retail_app_ecs.aws_secretsmanager_secret.mq
-
Evidence Nothing to show
The block stands for several units, so the generator's explanations of its values are not attributed to this unit; the trace file of the block holds them. These are the generator's own statements in the draft, not checks of the draft.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: trace: TR-6003c14a24b3
- recorded: trace: TR-b77494749ed2
-
Semantic claim Open items
The engine read 2 statements the source makes about this resource and decided what happens to each; 2 of them are critical settings, 2 of those still open.
- 2 left to a person to review
- 32 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/36
module.retail_app_ecs.aws_secretsmanager_secret.mq- claim: secret-value = KNOWN, CRITICAL, REVIEW
- claim: tc-secretsmanager-secret-name = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_secretsmanager_instance.migrated_secrets: written as an active resource (terraform/security.tf, lines 317-320); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
- stackit_secretsmanager_user.migration: written as an active resource (terraform/security.tf, lines 325-330); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
stackit_secretsmanager_instance.migrated_secrets- block in the draft: stackit_secretsmanager_instance.migrated_secrets
- block in the draft: stackit_secretsmanager_user.migration
- block in the draft: terraform/security.tf:317-320
- block in the draft: terraform/security.tf:325-330
- trace: TR-6003c14a24b3
- trace: TR-b77494749ed2
-
Residual difference Open items
The draft states, for this unit: 2 properties it does not carry, 1 finding, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.mq): name — the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.mq writes it into the Secrets Manager instance from a document you supply (the path is its name when the source states it as a …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret_version.mq): secret_id, secret_string — a setting of module.retail_app_ecs.aws_secretsmanager_secret.mq: the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.mq writes it into the Secrets …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-API-OPT-IN(aliasconvert:api:secrets-manager-vault:v1:unknown:API_OPT_IN)
module.retail_app_ecs.aws_secretsmanager_secret.orders_db
-
Source Established
module.retail_app_ecs.aws_secretsmanager_secret.orders_db is a resource of the source, declared in ../../lib/ecs/orders.tf (lines 68-70). It is part of module.retail_app_ecs. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/37
module.retail_app_ecs.aws_secretsmanager_secret.orders_db- knowledge base case: secret
- knowledge base rule: aws.secretsmanager_secret
- source type: aws_secretsmanager_secret
- unit: module.retail_app_ecs.aws_secretsmanager_secret.orders_db
-
Evidence Nothing to show
The block stands for several units, so the generator's explanations of its values are not attributed to this unit; the trace file of the block holds them. These are the generator's own statements in the draft, not checks of the draft.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: trace: TR-6003c14a24b3
- recorded: trace: TR-b77494749ed2
-
Semantic claim Open items
The engine read 2 statements the source makes about this resource and decided what happens to each; 2 of them are critical settings, 2 of those still open.
- 2 left to a person to review
- 32 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/37
module.retail_app_ecs.aws_secretsmanager_secret.orders_db- claim: secret-value = KNOWN, CRITICAL, REVIEW
- claim: tc-secretsmanager-secret-name = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_secretsmanager_instance.migrated_secrets: written as an active resource (terraform/security.tf, lines 317-320); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
- stackit_secretsmanager_user.migration: written as an active resource (terraform/security.tf, lines 325-330); it also stands for 3 other units; the whole comment of the block is in engineering/trace/security.md
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
stackit_secretsmanager_instance.migrated_secrets- block in the draft: stackit_secretsmanager_instance.migrated_secrets
- block in the draft: stackit_secretsmanager_user.migration
- block in the draft: terraform/security.tf:317-320
- block in the draft: terraform/security.tf:325-330
- trace: TR-6003c14a24b3
- trace: TR-b77494749ed2
-
Residual difference Open items
The draft states, for this unit: 2 properties it does not carry, 1 finding, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret.orders_db): name — the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.orders_db writes it into the Secrets Manager instance from a document you supply (the path is its name when the source …
- NOT CARRIED (module.retail_app_ecs.aws_secretsmanager_secret_version.orders_db): secret_id, secret_string — a setting of module.retail_app_ecs.aws_secretsmanager_secret.orders_db: the API step API/secrets-manager-vault/WriteSecret/module.retail_app_ecs.aws_secretsmanager_secret.orders_db writes it …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-API-OPT-IN(aliasconvert:api:secrets-manager-vault:v1:unknown:API_OPT_IN)
module.retail_app_ecs.module.alb.aws_lb.this
-
Source Established
module.retail_app_ecs.module.alb.aws_lb.this is a resource of the source, declared in .terraform/modules/retail_app_ecs.alb/main.tf (lines 5-63). It is part of module.retail_app_ecs.module.alb. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.alb.aws_lb.this (.terraform/modules/retail_app_ecs.alb/main.tf:5) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/28
module.retail_app_ecs.module.alb.aws_lb.this- knowledge base case: alb
- knowledge base rule: aws.lb
- source type: aws_lb
- unit: module.retail_app_ecs.module.alb.aws_lb.this
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are and which source attribute each setting is written from. These are the generator's own statements in the draft, not checks of the draft.
- listeners[listener-1].http.hosts[*].rules[*].target_pool (default route) from module.retail_app_ecs.module.alb.aws_lb_listener.frontend_http_tcp.default_action
- listeners[listener-1].port from module.retail_app_ecs.module.alb.aws_lb_listener.frontend_http_tcp.port
- listeners[listener-1].protocol from module.retail_app_ecs.module.alb.aws_lb_listener.frontend_http_tcp.protocol
- name from module.retail_app_ecs.module.alb.aws_lb.this.name
- networks[0].network_id SOURCE_UNPROVEN: the load balancer spans several subnets of the source, or a repeated one, and the network the draft places it in is a variable or a choice of the placement, not a setting of the source
- options.ephemeral_address from module.retail_app_ecs.module.alb.aws_lb.this.internal
- plan_id SOURCE_UNPROVEN: a STACKIT Application Load Balancer plan has no setting in the source: it is chosen from the catalogue of the target
- target_pools[retail-app-ecs-alb-main].active_health_check.healthy_threshold from module.retail_app_ecs.module.alb.aws_lb_target_group.main.health_check.healthy_threshold
- and 8 settings of the block with the source attribute each is written from; the trace file of the block holds all of them
- Internet-facing: an ephemeral public address is requested; use external_address with a stackit_public_ip for a fixed one.
- WebSocket: an AWS Application Load Balancer proxies WebSocket upgrades (ws, wss) on every listener and rule without a setting; a STACKIT Application Load Balancer enables them per rule (rules[].web_socket, pinned provider; docs.stackit.cloud, Application Load Balancer, create: "Enable only if your …
- CLIENT ACCESS: public on source, public on target — the rules of module.retail_app_ecs.module.alb.aws_security_group.this, module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix admit every IPv4 address on the listener port(s) 80, and the load balancer drafted here is public and …
- CLIENT ACCESS (assumed): the network ACLs of the subnets of module.retail_app_ecs.module.alb.aws_lb.this is not managed by this source and is taken as unrestricted — not verified; the client access stated for stackit_application_load_balancer.retail_app_ecs_alb_this is an assumption about it and …
- SECURITY_OBSERVATION Plaintext public listener of module.retail_app_ecs.module.alb.aws_lb.this, port 80 (non-blocking): The source load balancer module.retail_app_ecs.module.alb.aws_lb.this is internet-facing and every listener it states is HTTP (port 80 forwards to its targets, no listener is …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.lb/alb · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-c243e261bc0d
-
Semantic claim Open items
The engine read 19 statements the source makes about this resource and decided what happens to each; 18 of them are critical settings, 11 of those still open.
- 4 kept as it is
- 3 kept in another form
- 1 not supported on STACKIT
- 10 left to a person to review
- 1 carried into the draft and listed in the ledger
- 115 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/28
module.retail_app_ecs.module.alb.aws_lb.this- claim: client-restriction = KNOWN, CRITICAL, REVIEW
- claim: cross-zone = KNOWN, CRITICAL, PRESERVED
- claim: deletion-protection = KNOWN, CRITICAL, PRESERVED
- claim: drop-invalid-headers = KNOWN, CRITICAL, PRESERVED
- claim: frontend-http2 = KNOWN, NON_CRITICAL, UNSUPPORTED
- claim: ip-address-type = KNOWN, CRITICAL, PRESERVED
- claim: lb-connection-timeouts = KNOWN, CRITICAL, REVIEW
- claim: lb-routing-and-addressing = KNOWN, CRITICAL, REVIEW
- claim: lb-subnets = UNKNOWN, CRITICAL, REVIEW
- claim: lb-type = KNOWN, CRITICAL, TRANSFORMED
- claim: listener-protocol = KNOWN, CRITICAL, TRANSFORMED
- claim: listeners = KNOWN, CRITICAL, TRANSFORMED
- claim: network-exposure = KNOWN, CRITICAL, LEDGER
- claim: request-handling = KNOWN, CRITICAL, REVIEW
- claim: request-header-options = KNOWN, CRITICAL, REVIEW
- claim: tc-lb-name = KNOWN, CRITICAL, REVIEW
- claim: tcfp-lb-listener--default-action--target-group-arn = UNKNOWN, CRITICAL, REVIEW
- claim: tcfp-lb-listener--default-action--type = KNOWN, CRITICAL, REVIEW
- claim: tcfp-lb-listener--protocol = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 1 block for this unit, written as active Terraform.
- stackit_application_load_balancer.retail_app_ecs_alb_this: written as an active resource (terraform/loadbalancing.tf, lines 21-62); the whole comment of the block is in engineering/trace/loadbalancing.md
In terraform/loadbalancing.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/loadbalancing.tf
stackit_application_load_balancer.retail_app_ecs_alb_this- block in the draft: stackit_application_load_balancer.retail_app_ecs_alb_this
- block in the draft: terraform/loadbalancing.tf:21-62
- trace: TR-c243e261bc0d
-
Residual difference Open items
The draft states, for this unit: 4 properties it does not carry, 1 open ledger row, 1 finding, 3 open items, 2 open decisions of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.alb.aws_lb_target_group.main): deregistration_delay = 30 — a STACKIT target pool has name, target_port, targets, active_health_check and tls_config only (pinned provider): no connection draining delay, slow start or load-balancing algorithm — not generated; …
- NOT CARRIED (module.retail_app_ecs.module.alb.aws_lb.this): security_groups — a STACKIT Application Load Balancer is in no security group, so the attachment of module.retail_app_ecs.module.alb.aws_security_group.this, module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix is not …
- NOT CARRIED (module.retail_app_ecs.module.alb.aws_lb.this): enable_http2 = true, desync_mitigation_mode = defensive, xff_header_processing_mode = append, enable_xff_client_port = true — no attribute for it on the STACKIT load balancers (pinned provider).
- NOT CARRIED (module.retail_app_ecs.module.alb.aws_lb.this): idle_timeout = 60 — the STACKIT Application Load Balancer has no idle timeout; Network Load Balancer listeners take tcp.idle_timeout — not generated (pinned provider).
- Ledger: network exposure: internet-facing → public address (ASSUMPTION: the unmanaged default network ACL of the subnets of module.retail_app_ecs.module.alb.aws_lb.this is taken as unrestricted, not verified) (SECURITY_OBSERVATION Plaintext public listener of module.retail_app_ecs.module.alb.aws_lb.this, …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the source load balancer names every instance of the repeated subnet module.vpc.module.vpc.aws_subnet.public, each a network of its own on STACKIT; the draft places the load balancer in one network (its layout choice; other layouts are a redesign): which instance is the placement is a decision; …
- Open: EXPOSURE PATH: pool retail-app-ecs-alb-main forwards to the ECS service module.retail_app_ecs.module.ui_service.aws_ecs_service.this, drafted as the workload ui on SKE (kubernetes/ui/manifests.yaml): the pool reaches it through the NodePort Service ui-nodeport of the manifest (node port 30000 → …
- Open: module.retail_app_ecs.module.alb.aws_lb.this: which instance of stackit_network.vpc_vpc_public the networks of this block means is not visible in the source (it is repeated); set var.retail_app_ecs_alb_this_network_id_target to its index — no instance is assumed (open decision …
- 2 open decisions of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-AMBIGUOUS-INSTANCE-SELECTION(aliasconvert:module.retail_app_ecs.module.alb.aws_lb.this:network_id:AMBIGUOUS_INSTANCE_SELECTION) - decision:
DEC-GEN-CONVERT-INGRESS-EXPOSURE-PATH(aliasconvert:module.retail_app_ecs.module.alb.aws_lb.this:target_pools:INGRESS_EXPOSURE_PATH)
module.retail_app_ecs.module.alb.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.alb.aws_security_group.this is an AWS security group, declared in .terraform/modules/retail_app_ecs.alb/main.tf (lines 807-824). It is part of module.retail_app_ecs.module.alb. It states 0 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/10
module.retail_app_ecs.module.alb.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.alb.aws_security_group.this
-
Evidence Established
The source states no rule for this unit.
In the source: .terraform/modules/retail_app_ecs.alb/main.tf, lines 807-824.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/retail_app_ecs.alb/main.tf lines 807-824
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.alb.aws_security_group.this[0]: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.alb.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.alb.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.alb.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 4 statements the source makes about this group and decided what happens to each; 4 of them are critical settings, 4 of those still open.
- 1 not supported on STACKIT
- 3 left to a person to review
- 112 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/10
module.retail_app_ecs.module.alb.aws_security_group.this- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Established
The unit stands for 1 security group with 0 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.alb.aws_security_group.this[0]: 0 rules
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.alb.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.alb.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 7 evidenced facts about STACKIT:
- 2 about values the API rejects
- 2 about rules or values it creates by default
- 1 about limits
- 2 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 0 rules for this unit. Of their 11 fields: 1 carried exactly, 2 needing a value you supply, 7 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_alb_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_alb_this: labels needs a value you supply
- stackit_security_group.retail_app_ecs_alb_this: project_id needs a value you supply
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_alb_this- field: stackit_security_group.retail_app_ecs_alb_this.default_egress.ipv4 = SAFE_OMISSION: the source restricts IPv4 egress, and STACKIT creates an allow-all IPv4 egress rule on this group that the draft does not manage; that rule acts on the network interface that lists the group, and no block of the draft lists this one (its members are module.retail_app_ecs.module.alb.aws_lb.this (aws_lb, written without a security group)), so there is no effect to decide about; if you attach the group to an interface by hand, that rule applies to the interface until it is deleted (stackit security-group rule list, then delete with the security group id): decide then
- field: stackit_security_group.retail_app_ecs_alb_this.default_egress.ipv6 = SAFE_OMISSION: the source restricts IPv6 egress, and STACKIT creates an allow-all IPv6 egress rule on this group that the draft does not manage; that rule acts on the network interface that lists the group, and no block of the draft lists this one (its members are module.retail_app_ecs.module.alb.aws_lb.this (aws_lb, written without a security group)), so there is no effect to decide about; if you attach the group to an interface by hand, that rule applies to the interface until it is deleted (stackit security-group rule list, then delete with the security group id): decide then
- field: stackit_security_group.retail_app_ecs_alb_this.labels = VARIABLE_REQUIRED: the source reads a variable for its tags; the labels are a variable of the draft with the scan's reading as default
- field: stackit_security_group.retail_app_ecs_alb_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_alb_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_alb_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_alb_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
-
Render Established
The draft writes 1 resource of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_alb_this: written as an active resource (terraform/security.tf, lines 53-60)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:53-60
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_alb_this
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 3 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_alb_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_alb_this: A name the source does not give is derived by StackToIT from the source address; check it before use.
- stackit_security_group.retail_app_ecs_alb_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_alb_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_alb_this name [derived]: source: the source group has no name of its own: AWS names it from the name_prefix "retail-store-ecs-ui-" and a random suffix (the draft does not use the prefix as the name); target: name retail-app-ecs-alb-this derived from the address module.retail_app_ecs.module.alb.aws_security_group.this[0]
- residual: stackit_security_group.retail_app_ecs_alb_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.alb_sg.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.alb_sg.aws_security_group.this is an AWS security group, declared in .terraform/modules/retail_app_ecs.alb_sg/main.tf (lines 13-32). It is switched off in the source. It is part of module.retail_app_ecs.module.alb_sg. It states 0 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/62
module.retail_app_ecs.module.alb_sg.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.alb_sg.aws_security_group.this
-
Evidence Established
The source states no rule for this unit.
In the source: .terraform/modules/retail_app_ecs.alb_sg/main.tf, lines 13-32.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/retail_app_ecs.alb_sg/main.tf lines 13-32
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.alb_sg.aws_security_group.this: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.retail_app_ecs.module.alb_sg.aws_security_group.this- proof cause: source-not-present at module.retail_app_ecs.module.alb_sg.aws_security_group.this vpc_id
- proof: UNRESOLVED/NONE at module.retail_app_ecs.module.alb_sg.aws_security_group.this vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Established
The unit stands for 1 security group with 0 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.alb_sg.aws_security_group.this: 0 rules
- it has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.alb_sg.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.alb_sg.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the group (count or for_each yields none, or it is switched off): no stackit_security_group is drafted
- plan producer: stacktoit-awssg 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix
-
Source Established
module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix is an AWS security group, declared in .terraform/modules/retail_app_ecs.alb_sg/main.tf (lines 37-60). It is part of module.retail_app_ecs.module.alb_sg. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/11
module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix
-
Evidence Open items
The source states 2 rules for this unit. 2 rules are stated exactly.
- egress any protocol to 0.0.0.0/0, ::/0
- ingress tcp port 80 from 0.0.0.0/0
- A rule that belongs to none of the groups of this unit: egress any protocol to 0.0.0.0/0, ::/0
- A rule that belongs to none of the groups of this unit: ingress tcp port 80 from 0.0.0.0/0
In the source: .terraform/modules/retail_app_ecs.alb_sg/main.tf, lines 37-60.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/retail_app_ecs.alb_sg/main.tf lines 37-60
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- incomplete set: module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0] module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules (group-choice)
- incomplete set: module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0] module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules (group-choice)
- source rule: module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules[0]
- source rule: module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules[0]
- unplaced rule: module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules[0] (group-choice)
- unplaced rule: module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules[0] (group-choice)
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0]: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix vpc_id
-
Semantic claim Open items
The engine read 10 statements the source makes about this group and decided what happens to each; 9 of them are critical settings, 9 of those still open.
- 1 not supported on STACKIT
- 8 left to a person to review
- 1 not applicable here
- 106 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/11
module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: revoke-rules-on-delete = KNOWN, NON_CRITICAL, NOT_APPLICABLE
- claim: rule-ports = KNOWN, CRITICAL, REVIEW
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: standalone-rule-empty-sources = KNOWN, CRITICAL, REVIEW
- claim: standalone-rule-other-sources = KNOWN, CRITICAL, REVIEW
- claim: standalone-rule-values = KNOWN, CRITICAL, REVIEW
- claim: stateful = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--from-port = KNOWN, CRITICAL, REVIEW
- claim: tcfp-security-group-rule--to-port = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0]: 0 rules
- 2 rules cannot be placed on one of the groups
- 2 sets whose members are not all visible statically
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 8 evidenced facts about STACKIT:
- 2 about values the API rejects
- 2 about rules or values it creates by default
- 2 about limits
- 2 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: group-description-length (LIMIT, stackit_security_group.description)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 0 rules for this unit. Of their 12 fields: 2 carried exactly, 2 needing a value you supply, 7 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: labels needs a value you supply
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: project_id needs a value you supply
- 4 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.default_egress.ipv4 = SAFE_OMISSION: the source restricts IPv4 egress, and STACKIT creates an allow-all IPv4 egress rule on this group that the draft does not manage; that rule acts on the network interface that lists the group, and no block of the draft lists this one (its members are module.retail_app_ecs.module.alb.aws_lb.this (aws_lb, written without a security group)), so there is no effect to decide about; if you attach the group to an interface by hand, that rule applies to the interface until it is deleted (stackit security-group rule list, then delete with the security group id): decide then
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.default_egress.ipv6 = SAFE_OMISSION: the source restricts IPv6 egress, and STACKIT creates an allow-all IPv6 egress rule on this group that the draft does not manage; that rule acts on the network interface that lists the group, and no block of the draft lists this one (its members are module.retail_app_ecs.module.alb.aws_lb.this (aws_lb, written without a security group)), so there is no effect to decide about; if you attach the group to an interface by hand, that rule applies to the interface until it is deleted (stackit security-group rule list, then delete with the security group id): decide then
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.labels = VARIABLE_REQUIRED: the source reads a variable for its tags; the labels are a variable of the draft with the scan's reading as default
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- manual action:
DEC-SEC-STACKITSG-ACTION-INCOMPLETE(aliasawssg:incomplete:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix:group module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0]:rules:module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules) (BEFORE_PILOT): Re-create the rules beyond the known set of group module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0] (rules, module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules) - manual action:
DEC-SEC-STACKITSG-ACTION-INCOMPLETE(aliasawssg:incomplete:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix:group module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0]:rules:module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules) (BEFORE_PILOT): Re-create the rules beyond the known set of group module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0] (rules, module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules) - manual action:
DEC-SEC-STACKITSG-ACTION-UNPLACED(aliasawssg:unplaced:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix:module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules[0]) (BEFORE_PILOT): Place the source rule module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules[0] on the security group it belongs to and write it - manual action:
DEC-SEC-STACKITSG-ACTION-UNPLACED(aliasawssg:unplaced:module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix:module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules[0]) (BEFORE_PILOT): Place the source rule module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules[0] on the security group it belongs to and write it - plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
-
Render Established
The draft writes 1 resource of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: written as an active resource (terraform/security.tf, lines 31-39)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:31-39
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 0 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 7 remaining differences between this unit and its STACKIT target. None is accepted yet.
- module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix: A rule or a related resource is not written, because writing it as it is would allow more than the source does or its values are not visible; a person re-creates or checks it. (2 times)
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: The source may allow more rules than are visible statically; only the visible ones are planned. (2 times)
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: A name the source does not give is derived by StackToIT from the source address; check it before use.
- stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix rule module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules[0] [rule withheld]: source: an allow rule of the unit's security group; target: no rule is produced: it cannot be attributed to a group (group-choice)
- residual: module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix rule module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules[0] [rule withheld]: source: an allow rule of the unit's security group; target: no rule is produced: it cannot be attributed to a group (group-choice)
- residual: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules [rules beyond the known set]: source: the source allows more than the entries that are visible statically; target: only the known entries are produced; an unknown number of unknown entries of module.retail_app_ecs.module.alb_sg.aws_security_group_rule.egress_rules are not (group-choice)
- residual: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules [rules beyond the known set]: source: the source allows more than the entries that are visible statically; target: only the known entries are produced; an unknown number of unknown entries of module.retail_app_ecs.module.alb_sg.aws_security_group_rule.ingress_rules are not (group-choice)
- residual: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix name [derived]: source: the source group has no name of its own: AWS names it from the name_prefix "retail-store-ecs-ui-" and a random suffix (the draft does not use the prefix as the name); target: name retail-app-ecs-alb-sg-this-name-prefix derived from the address module.retail_app_ecs.module.alb_sg.aws_security_group.this_name_prefix[0]
- residual: stackit_security_group.retail_app_ecs_alb_sg_this_name_prefix vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.carts_service.aws_ecs_service.this
-
Source Established
module.retail_app_ecs.module.carts_service.aws_ecs_service.this is a container service (it keeps container tasks running), declared in ../../lib/ecs/service/ecs.tf (lines 136-175). It is part of module.retail_app_ecs.module.carts_service. It names 2 identities it runs as. This trace follows the identity of the workload: which identity it runs as and what the plan does with it on STACKIT.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/29
module.retail_app_ecs.module.carts_service.aws_ecs_service.this- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_service
- unit: module.retail_app_ecs.module.carts_service.aws_ecs_service.this
-
Evidence Established
The source names 2 identities this workload runs as.
- the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): runs as module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role (a role)
- the application's identity inside a container task: runs as module.retail_app_ecs.module.carts_service.aws_iam_role.task_role (a role)
In the source: ../../lib/ecs/service/ecs.tf, lines 136-175.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/ecs.tf lines 136-175
- binding: module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this#execution_role_arn (EXECUTION_ROLE, EXECUTION, KNOWN)
- binding: module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this#task_role_arn (TASK_ROLE, TASK, KNOWN)
-
Resolution proof Established
2 references are resolved for this unit: 2 proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- a step to the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): refers to module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role, proven by a direct reference
- a step to the application's identity inside a container task: refers to module.retail_app_ecs.module.carts_service.aws_iam_role.task_role, proven by a direct reference
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.carts_service.aws_ecs_service.this- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this execution_role_arn
- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this task_role_arn
-
Semantic claim Open items
The engine read 16 statements the source makes about this workload and decided what happens to each; 16 of them are critical settings, 16 of those still open.
- 16 left to a person to review
- 107 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/29
module.retail_app_ecs.module.carts_service.aws_ecs_service.this- claim: linked-dependency:aws_dynamodb_table = KNOWN, CRITICAL, REVIEW
- claim: service-connect-values = KNOWN, CRITICAL, REVIEW
- claim: service-desired-count = KNOWN, CRITICAL, REVIEW
- claim: service-discovery = KNOWN, CRITICAL, REVIEW
- claim: service-execute-command = KNOWN, CRITICAL, REVIEW
- claim: service-network-placement = KNOWN, CRITICAL, REVIEW
- claim: service-public-ip-setting = KNOWN, CRITICAL, REVIEW
- claim: service-task-definition = KNOWN, CRITICAL, REVIEW
- claim: task-definition = KNOWN, CRITICAL, REVIEW
- claim: td-container-definitions = KNOWN, CRITICAL, REVIEW
- claim: td-container-image-registry = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-plaintext-secret-env = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-secret-references = UNKNOWN, CRITICAL, REVIEW
- claim: td-execution-role-arn = KNOWN, CRITICAL, REVIEW
- claim: td-network-mode = KNOWN, CRITICAL, REVIEW
- claim: td-task-role-arn = KNOWN, CRITICAL, REVIEW
-
Intent Open items
This workload is not made of servers, so no service account is attached to it: the identities it names are stated as facts and left to a person.
- The unit is a container service (it keeps container tasks running)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity:module.retail_app_ecs.module.carts_service.aws_ecs_service.this- intent family: IDENTITY
- intent: identity:module.retail_app_ecs.module.carts_service.aws_ecs_service.this
-
Target capability Established
The target is a STACKIT service account (stackit_service_account) attached to a server: a server takes one service account, and the account holds the roles the workload needs.
- Service: available
- API: write supported
- Terraform: resource available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity.server-service-account- capability: identity.server-service-account
- provider version: 0.121.0
-
Transformation Open items
No STACKIT service account is attached to this workload: it is not made of servers (the draft writes service accounts for servers, and the identity of a container, a function or a cluster is stated as a fact), or the source does not decide which identity it runs as, so nothing is attached and a person decides.
- 2 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitsa:facts:module.retail_app_ecs.module.carts_service.aws_ecs_service.this:module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this#execution_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.carts_service.aws_ecs_service.this pulls images, injects secrets and writes logs: the platform agent's role has no STACKIT counterpart to attach - manual action: alias
stackitsa:facts:module.retail_app_ecs.module.carts_service.aws_ecs_service.this:module.retail_app_ecs.module.carts_service.aws_ecs_task_definition.this#task_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.carts_service.aws_ecs_service.this gets its application identity on STACKIT (a service account of its own, workload federation): the draft does not write it - no target: MANUAL_REVIEW: module.retail_app_ecs.module.carts_service.aws_ecs_service.this is a container service: its 2 identity binding(s) are facts only, and no service account is attached for it (the draft writes service accounts for servers (the EC2 family); the identities of containers, functions and clusters are stated as facts and left to a person)
- plan producer: stacktoit-stackitsa 0.1.0
-
Render Nothing to show
The identity plan writes no STACKIT resource for this unit, so nothing is rendered from it. The blocks the draft holds for the workload itself are written by another generator, which records no plan.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The identity plan writes no resource for this unit, so the checks over the identity part of the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: attach-complete ok=true: 0 attachment block(s) written as resources, each with a project, a region, a server and a written account
- check: final-artifact ok=true: the service account resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role
-
Source Established
module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 14-18). It is part of module.retail_app_ecs.module.carts_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role (../../lib/ecs/service/iam.tf:14) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/4
module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_carts_service_task_execution_role (from the policies of module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_carts_service_task_execution_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-58f6779c70bf
- recorded: trace: TR-935427f3024d
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/4
module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-ecs = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 18-23); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_carts_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 9-12); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_execution_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_execution_role
- block in the draft: stackit_service_account.retail_app_ecs_carts_service_task_execution_role
- block in the draft: terraform/identity.tf:18-23
- block in the draft: terraform/identity.tf:9-12
- trace: TR-58f6779c70bf
- trace: TR-935427f3024d
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.carts_service.aws_iam_role.task_execution_role is "retail-app-ecs-carts-service-task-execution-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.carts_service.aws_iam_role.task_role
-
Source Established
module.retail_app_ecs.module.carts_service.aws_iam_role.task_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 31-35). It is part of module.retail_app_ecs.module.carts_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.carts_service.aws_iam_role.task_role (../../lib/ecs/service/iam.tf:31) — RECONFIGURE / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/12
module.retail_app_ecs.module.carts_service.aws_iam_role.task_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.carts_service.aws_iam_role.task_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_carts_service_task_role (from the policies of module.retail_app_ecs.module.carts_service.aws_iam_role.task_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_carts_service_task_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: linked-dependency-unread
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-74ede57c41f1
- recorded: trace: TR-eb88a52a7e37
-
Semantic claim Open items
The engine read 7 statements the source makes about this resource and decided what happens to each; 7 of them are critical settings, 6 of those still open.
- 6 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/12
module.retail_app_ecs.module.carts_service.aws_iam_role.task_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-customer-policy = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: linked-dependency:aws_dynamodb_table = KNOWN, CRITICAL, REVIEW
- claim: permissions = UNKNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_role: written as an active resource (terraform/identity.tf, lines 41-46); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_carts_service_task_role: written as an active resource (terraform/identity.tf, lines 32-35); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_carts_service_task_role
- block in the draft: stackit_service_account.retail_app_ecs_carts_service_task_role
- block in the draft: terraform/identity.tf:32-35
- block in the draft: terraform/identity.tf:41-46
- trace: TR-74ede57c41f1
- trace: TR-eb88a52a7e37
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 2 findings, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.carts_service.aws_iam_role.task_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions boundary. The …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: This unit names module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this (aws_dynamodb_table), whose own decision the target does not carry (it is REDESIGN), and the semantic contract of aws_iam_role does not read aws_dynamodb_table, so what the reference becomes is not assessed.
- Open: the name of module.retail_app_ecs.module.carts_service.aws_iam_role.task_role is "retail-app-ecs-carts-service-task-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same name is …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.carts_service.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.carts_service.aws_security_group.this is an AWS security group, declared in ../../lib/ecs/service/sg.tf (lines 1-18). It is part of module.retail_app_ecs.module.carts_service. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/13
module.retail_app_ecs.module.carts_service.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.carts_service.aws_security_group.this
-
Evidence Established
The source states 2 rules for this unit. 2 rules are stated exactly.
- ingress tcp port 8080 from 0.0.0.0/0
- egress any protocol to 0.0.0.0/0
In the source: ../../lib/ecs/service/sg.tf, lines 1-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/sg.tf lines 1-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.retail_app_ecs.module.carts_service.aws_security_group.this#egress#0#909db684902e
- source rule: module.retail_app_ecs.module.carts_service.aws_security_group.this#ingress#0#3d8f71de8dab
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.carts_service.aws_security_group.this: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.carts_service.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.carts_service.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.carts_service.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 4 left to a person to review
- 2 carried into the draft and listed in the ledger
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/13
module.retail_app_ecs.module.carts_service.aws_security_group.this- claim: egress-rule-protocol = KNOWN, CRITICAL, REVIEW
- claim: egress-sources = KNOWN, CRITICAL, REVIEW
- claim: ingress-sources = KNOWN, CRITICAL, LEDGER
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, LEDGER
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.carts_service.aws_security_group.this: 2 rules
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.carts_service.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.carts_service.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 14 evidenced facts about STACKIT:
- 4 about values the API rejects
- 3 about rules or values it creates by default
- 3 about limits
- 4 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: ether-type-default-ipv4 (DEFAULT_RULE, stackit_security_group_rule.ether_type)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: ip-range-family-must-match-ether-type (REJECTS, stackit_security_group_rule.ip_range)
- constraint relied on: port-range-bounds (LIMIT, stackit_security_group_rule.port_range)
- constraint relied on: port-range-is-destination-port (SEMANTIC, stackit_security_group_rule.port_range)
- constraint relied on: protocol-name-values (LIMIT, stackit_security_group_rule.protocol.name)
- constraint relied on: protocol-name-xor-number (REJECTS, stackit_security_group_rule.protocol.name)
- constraint relied on: remote-security-group-by-id (SEMANTIC, stackit_security_group_rule.remote_security_group_id)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 1 rule for this unit. Of their 19 fields: 7 carried exactly, 3 needing a value you supply, 8 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_carts_service_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_carts_service_this: name needs a value you supply
- project_id needs a value you supply (on 2 resources)
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_carts_service_this- decision:
DEC-GEN-CONVERT-POD-SEGMENTATION/module.retail_app_ecs.module.carts_service.aws_security_group.this(aliasconvert:module.retail_app_ecs.module.carts_service.aws_security_group.this:security-group:POD_SEGMENTATION) - field: stackit_security_group.retail_app_ecs_carts_service_this.default_egress.ipv4 = SAFE_OMISSION: the source allows all IPv4 egress, which is the allow-all IPv4 egress rule STACKIT creates on every new group: it is covered by the STACKIT default egress rules and not produced (a duplicate is rejected with HTTP 409)
- field: stackit_security_group.retail_app_ecs_carts_service_this.default_egress.ipv6 = SAFE_OMISSION: the network has no IPv6 prefix (its VPC module.vpc.module.vpc.aws_vpc.this assigns no IPv6 CIDR block and the estate associates none), and the drafted STACKIT network has none either, so the allow-all IPv6 egress rule STACKIT creates on every new group acts on no traffic, whatever IPv6 egress rules the source lists; if an IPv6 prefix is added to the network later, delete that rule (stackit security-group rule list, then delete with the security group id) or write the equivalent rules of the source: decide then
- field: stackit_security_group.retail_app_ecs_carts_service_this.labels = SAFE_OMISSION: the source group sets no tags, so there are no labels to write
- field: stackit_security_group.retail_app_ecs_carts_service_this.name = VARIABLE_REQUIRED: the source value comes from an overridable root variable (var.environment_name)
- field: stackit_security_group.retail_app_ecs_carts_service_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_carts_service_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_carts_service_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_carts_service_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_carts_service_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_carts_service_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_carts_service_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- field: stackit_security_group_rule.retail_app_ecs_carts_service_this_ingress_1.project_id = VARIABLE_REQUIRED: the STACKIT project the rule belongs to
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
- plan rule: awssg.rule
-
Render Established
The draft writes 2 resources of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_carts_service_this: written as an active resource (terraform/security.tf, lines 74-77)
- stackit_security_group_rule.retail_app_ecs_carts_service_this_ingress_1: written as an active resource (terraform/security.tf, lines 79-92)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:74-77
- block in the draft: terraform/security.tf:79-92
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_carts_service_this
- resource address: stackit_security_group_rule.retail_app_ecs_carts_service_this_ingress_1
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 1 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_carts_service_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_carts_service_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_carts_service_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_carts_service_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.catalog_service.aws_ecs_service.this
-
Source Established
module.retail_app_ecs.module.catalog_service.aws_ecs_service.this is a container service (it keeps container tasks running), declared in ../../lib/ecs/service/ecs.tf (lines 136-175). It is part of module.retail_app_ecs.module.catalog_service. It names 2 identities it runs as. This trace follows the identity of the workload: which identity it runs as and what the plan does with it on STACKIT.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/40
module.retail_app_ecs.module.catalog_service.aws_ecs_service.this- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_service
- unit: module.retail_app_ecs.module.catalog_service.aws_ecs_service.this
-
Evidence Established
The source names 2 identities this workload runs as.
- the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): runs as module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role (a role)
- the application's identity inside a container task: runs as module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role (a role)
In the source: ../../lib/ecs/service/ecs.tf, lines 136-175.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/ecs.tf lines 136-175
- binding: module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this#execution_role_arn (EXECUTION_ROLE, EXECUTION, KNOWN)
- binding: module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this#task_role_arn (TASK_ROLE, TASK, KNOWN)
-
Resolution proof Established
2 references are resolved for this unit: 2 proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- a step to the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): refers to module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role, proven by a direct reference
- a step to the application's identity inside a container task: refers to module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role, proven by a direct reference
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.catalog_service.aws_ecs_service.this- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this execution_role_arn
- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this task_role_arn
-
Semantic claim Open items
The engine read 16 statements the source makes about this workload and decided what happens to each; 16 of them are critical settings, 16 of those still open.
- 16 left to a person to review
- 107 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/40
module.retail_app_ecs.module.catalog_service.aws_ecs_service.this- claim: linked-dependency:aws_secretsmanager_secret_version = KNOWN, CRITICAL, REVIEW
- claim: service-connect-values = KNOWN, CRITICAL, REVIEW
- claim: service-desired-count = KNOWN, CRITICAL, REVIEW
- claim: service-discovery = KNOWN, CRITICAL, REVIEW
- claim: service-execute-command = KNOWN, CRITICAL, REVIEW
- claim: service-network-placement = KNOWN, CRITICAL, REVIEW
- claim: service-public-ip-setting = KNOWN, CRITICAL, REVIEW
- claim: service-task-definition = KNOWN, CRITICAL, REVIEW
- claim: task-definition = KNOWN, CRITICAL, REVIEW
- claim: td-container-definitions = KNOWN, CRITICAL, REVIEW
- claim: td-container-image-registry = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-plaintext-secret-env = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-secret-references = UNKNOWN, CRITICAL, REVIEW
- claim: td-execution-role-arn = KNOWN, CRITICAL, REVIEW
- claim: td-network-mode = KNOWN, CRITICAL, REVIEW
- claim: td-task-role-arn = KNOWN, CRITICAL, REVIEW
-
Intent Open items
This workload is not made of servers, so no service account is attached to it: the identities it names are stated as facts and left to a person.
- The unit is a container service (it keeps container tasks running)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity:module.retail_app_ecs.module.catalog_service.aws_ecs_service.this- intent family: IDENTITY
- intent: identity:module.retail_app_ecs.module.catalog_service.aws_ecs_service.this
-
Target capability Established
The target is a STACKIT service account (stackit_service_account) attached to a server: a server takes one service account, and the account holds the roles the workload needs.
- Service: available
- API: write supported
- Terraform: resource available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity.server-service-account- capability: identity.server-service-account
- provider version: 0.121.0
-
Transformation Open items
No STACKIT service account is attached to this workload: it is not made of servers (the draft writes service accounts for servers, and the identity of a container, a function or a cluster is stated as a fact), or the source does not decide which identity it runs as, so nothing is attached and a person decides.
- 2 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitsa:facts:module.retail_app_ecs.module.catalog_service.aws_ecs_service.this:module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this#execution_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.catalog_service.aws_ecs_service.this pulls images, injects secrets and writes logs: the platform agent's role has no STACKIT counterpart to attach - manual action: alias
stackitsa:facts:module.retail_app_ecs.module.catalog_service.aws_ecs_service.this:module.retail_app_ecs.module.catalog_service.aws_ecs_task_definition.this#task_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.catalog_service.aws_ecs_service.this gets its application identity on STACKIT (a service account of its own, workload federation): the draft does not write it - no target: MANUAL_REVIEW: module.retail_app_ecs.module.catalog_service.aws_ecs_service.this is a container service: its 2 identity binding(s) are facts only, and no service account is attached for it (the draft writes service accounts for servers (the EC2 family); the identities of containers, functions and clusters are stated as facts and left to a person)
- plan producer: stacktoit-stackitsa 0.1.0
-
Render Nothing to show
The identity plan writes no STACKIT resource for this unit, so nothing is rendered from it. The blocks the draft holds for the workload itself are written by another generator, which records no plan.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The identity plan writes no resource for this unit, so the checks over the identity part of the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: attach-complete ok=true: 0 attachment block(s) written as resources, each with a project, a region, a server and a written account
- check: final-artifact ok=true: the service account resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role
-
Source Established
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 14-18). It is part of module.retail_app_ecs.module.catalog_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role (../../lib/ecs/service/iam.tf:14) — RECONFIGURE / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/38
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_catalog_service_task_execution_role (from the policies of module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_catalog_service_task_execution_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: linked-dependency-unread
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-089026082d6f
- recorded: trace: TR-2eebb342bc5c
-
Semantic claim Open items
The engine read 7 statements the source makes about this resource and decided what happens to each; 7 of them are critical settings, 6 of those still open.
- 6 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/38
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-ecs = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: linked-dependency:aws_secretsmanager_secret = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 65-70); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_catalog_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 56-59); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_execution_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_execution_role
- block in the draft: stackit_service_account.retail_app_ecs_catalog_service_task_execution_role
- block in the draft: terraform/identity.tf:56-59
- block in the draft: terraform/identity.tf:65-70
- trace: TR-089026082d6f
- trace: TR-2eebb342bc5c
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 3 findings, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: This unit names module.retail_app_ecs.aws_secretsmanager_secret.catalog_db (aws_secretsmanager_secret), whose own decision the target does not carry (it is RECONFIGURE, but the converter does not draft this aws_secretsmanager_secret (the generator skips this case, or only records it …
- warning: This unit names module.retail_app_ecs.aws_secretsmanager_secret.catalog_opensearch (aws_secretsmanager_secret), whose own decision the target does not carry (it is RECONFIGURE, but the converter does not draft this aws_secretsmanager_secret (the generator skips this case, or only records …
- Open: the name of module.retail_app_ecs.module.catalog_service.aws_iam_role.task_execution_role is "retail-app-ecs-catalog-service-task-execution-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role
-
Source Established
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 31-35). It is part of module.retail_app_ecs.module.catalog_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role (../../lib/ecs/service/iam.tf:31) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/14
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_catalog_service_task_role (from the policies of module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_catalog_service_task_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-cf63149db4be
- recorded: trace: TR-e48f32c8ead8
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/14
module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-customer-policy = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_role: written as an active resource (terraform/identity.tf, lines 87-92); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_catalog_service_task_role: written as an active resource (terraform/identity.tf, lines 78-81); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_catalog_service_task_role
- block in the draft: stackit_service_account.retail_app_ecs_catalog_service_task_role
- block in the draft: terraform/identity.tf:78-81
- block in the draft: terraform/identity.tf:87-92
- trace: TR-cf63149db4be
- trace: TR-e48f32c8ead8
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions boundary. …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.catalog_service.aws_iam_role.task_role is "retail-app-ecs-catalog-service-task-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same name is …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.catalog_service.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.catalog_service.aws_security_group.this is an AWS security group, declared in ../../lib/ecs/service/sg.tf (lines 1-18). It is part of module.retail_app_ecs.module.catalog_service. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/15
module.retail_app_ecs.module.catalog_service.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.catalog_service.aws_security_group.this
-
Evidence Established
The source states 2 rules for this unit. 2 rules are stated exactly.
- ingress tcp port 8080 from 0.0.0.0/0
- egress any protocol to 0.0.0.0/0
In the source: ../../lib/ecs/service/sg.tf, lines 1-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/sg.tf lines 1-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.retail_app_ecs.module.catalog_service.aws_security_group.this#egress#0#909db684902e
- source rule: module.retail_app_ecs.module.catalog_service.aws_security_group.this#ingress#0#3d8f71de8dab
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.catalog_service.aws_security_group.this: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.catalog_service.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.catalog_service.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.catalog_service.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 4 left to a person to review
- 2 carried into the draft and listed in the ledger
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/15
module.retail_app_ecs.module.catalog_service.aws_security_group.this- claim: egress-rule-protocol = KNOWN, CRITICAL, REVIEW
- claim: egress-sources = KNOWN, CRITICAL, REVIEW
- claim: ingress-sources = KNOWN, CRITICAL, LEDGER
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, LEDGER
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.catalog_service.aws_security_group.this: 2 rules
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.catalog_service.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.catalog_service.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 14 evidenced facts about STACKIT:
- 4 about values the API rejects
- 3 about rules or values it creates by default
- 3 about limits
- 4 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: ether-type-default-ipv4 (DEFAULT_RULE, stackit_security_group_rule.ether_type)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: ip-range-family-must-match-ether-type (REJECTS, stackit_security_group_rule.ip_range)
- constraint relied on: port-range-bounds (LIMIT, stackit_security_group_rule.port_range)
- constraint relied on: port-range-is-destination-port (SEMANTIC, stackit_security_group_rule.port_range)
- constraint relied on: protocol-name-values (LIMIT, stackit_security_group_rule.protocol.name)
- constraint relied on: protocol-name-xor-number (REJECTS, stackit_security_group_rule.protocol.name)
- constraint relied on: remote-security-group-by-id (SEMANTIC, stackit_security_group_rule.remote_security_group_id)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 1 rule for this unit. Of their 19 fields: 7 carried exactly, 3 needing a value you supply, 8 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_catalog_service_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_catalog_service_this: name needs a value you supply
- project_id needs a value you supply (on 2 resources)
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_catalog_service_this- decision:
DEC-GEN-CONVERT-POD-SEGMENTATION/module.retail_app_ecs.module.catalog_service.aws_security_group.this(aliasconvert:module.retail_app_ecs.module.catalog_service.aws_security_group.this:security-group:POD_SEGMENTATION) - field: stackit_security_group.retail_app_ecs_catalog_service_this.default_egress.ipv4 = SAFE_OMISSION: the source allows all IPv4 egress, which is the allow-all IPv4 egress rule STACKIT creates on every new group: it is covered by the STACKIT default egress rules and not produced (a duplicate is rejected with HTTP 409)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.default_egress.ipv6 = SAFE_OMISSION: the network has no IPv6 prefix (its VPC module.vpc.module.vpc.aws_vpc.this assigns no IPv6 CIDR block and the estate associates none), and the drafted STACKIT network has none either, so the allow-all IPv6 egress rule STACKIT creates on every new group acts on no traffic, whatever IPv6 egress rules the source lists; if an IPv6 prefix is added to the network later, delete that rule (stackit security-group rule list, then delete with the security group id) or write the equivalent rules of the source: decide then
- field: stackit_security_group.retail_app_ecs_catalog_service_this.labels = SAFE_OMISSION: the source group sets no tags, so there are no labels to write
- field: stackit_security_group.retail_app_ecs_catalog_service_this.name = VARIABLE_REQUIRED: the source value comes from an overridable root variable (var.environment_name)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_catalog_service_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_catalog_service_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- field: stackit_security_group_rule.retail_app_ecs_catalog_service_this_ingress_1.project_id = VARIABLE_REQUIRED: the STACKIT project the rule belongs to
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
- plan rule: awssg.rule
-
Render Established
The draft writes 2 resources of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_catalog_service_this: written as an active resource (terraform/security.tf, lines 106-109)
- stackit_security_group_rule.retail_app_ecs_catalog_service_this_ingress_1: written as an active resource (terraform/security.tf, lines 111-124)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:106-109
- block in the draft: terraform/security.tf:111-124
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_catalog_service_this
- resource address: stackit_security_group_rule.retail_app_ecs_catalog_service_this_ingress_1
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 1 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_catalog_service_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_catalog_service_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_catalog_service_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_catalog_service_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.checkout_service.aws_ecs_service.this
-
Source Established
module.retail_app_ecs.module.checkout_service.aws_ecs_service.this is a container service (it keeps container tasks running), declared in ../../lib/ecs/service/ecs.tf (lines 136-175). It is part of module.retail_app_ecs.module.checkout_service. It names 2 identities it runs as. This trace follows the identity of the workload: which identity it runs as and what the plan does with it on STACKIT.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/42
module.retail_app_ecs.module.checkout_service.aws_ecs_service.this- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_service
- unit: module.retail_app_ecs.module.checkout_service.aws_ecs_service.this
-
Evidence Established
The source names 2 identities this workload runs as.
- the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): runs as module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role (a role)
- the application's identity inside a container task: runs as module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role (a role)
In the source: ../../lib/ecs/service/ecs.tf, lines 136-175.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/ecs.tf lines 136-175
- binding: module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this#execution_role_arn (EXECUTION_ROLE, EXECUTION, KNOWN)
- binding: module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this#task_role_arn (TASK_ROLE, TASK, KNOWN)
-
Resolution proof Established
2 references are resolved for this unit: 2 proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- a step to the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): refers to module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role, proven by a direct reference
- a step to the application's identity inside a container task: refers to module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role, proven by a direct reference
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.checkout_service.aws_ecs_service.this- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this execution_role_arn
- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this task_role_arn
-
Semantic claim Open items
The engine read 15 statements the source makes about this workload and decided what happens to each; 15 of them are critical settings, 15 of those still open.
- 15 left to a person to review
- 107 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/42
module.retail_app_ecs.module.checkout_service.aws_ecs_service.this- claim: service-connect-values = KNOWN, CRITICAL, REVIEW
- claim: service-desired-count = KNOWN, CRITICAL, REVIEW
- claim: service-discovery = KNOWN, CRITICAL, REVIEW
- claim: service-execute-command = KNOWN, CRITICAL, REVIEW
- claim: service-network-placement = KNOWN, CRITICAL, REVIEW
- claim: service-public-ip-setting = KNOWN, CRITICAL, REVIEW
- claim: service-task-definition = KNOWN, CRITICAL, REVIEW
- claim: task-definition = KNOWN, CRITICAL, REVIEW
- claim: td-container-definitions = KNOWN, CRITICAL, REVIEW
- claim: td-container-image-registry = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-plaintext-secret-env = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-secret-references = UNKNOWN, CRITICAL, REVIEW
- claim: td-execution-role-arn = KNOWN, CRITICAL, REVIEW
- claim: td-network-mode = KNOWN, CRITICAL, REVIEW
- claim: td-task-role-arn = KNOWN, CRITICAL, REVIEW
-
Intent Open items
This workload is not made of servers, so no service account is attached to it: the identities it names are stated as facts and left to a person.
- The unit is a container service (it keeps container tasks running)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity:module.retail_app_ecs.module.checkout_service.aws_ecs_service.this- intent family: IDENTITY
- intent: identity:module.retail_app_ecs.module.checkout_service.aws_ecs_service.this
-
Target capability Established
The target is a STACKIT service account (stackit_service_account) attached to a server: a server takes one service account, and the account holds the roles the workload needs.
- Service: available
- API: write supported
- Terraform: resource available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity.server-service-account- capability: identity.server-service-account
- provider version: 0.121.0
-
Transformation Open items
No STACKIT service account is attached to this workload: it is not made of servers (the draft writes service accounts for servers, and the identity of a container, a function or a cluster is stated as a fact), or the source does not decide which identity it runs as, so nothing is attached and a person decides.
- 2 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitsa:facts:module.retail_app_ecs.module.checkout_service.aws_ecs_service.this:module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this#execution_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.checkout_service.aws_ecs_service.this pulls images, injects secrets and writes logs: the platform agent's role has no STACKIT counterpart to attach - manual action: alias
stackitsa:facts:module.retail_app_ecs.module.checkout_service.aws_ecs_service.this:module.retail_app_ecs.module.checkout_service.aws_ecs_task_definition.this#task_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.checkout_service.aws_ecs_service.this gets its application identity on STACKIT (a service account of its own, workload federation): the draft does not write it - no target: MANUAL_REVIEW: module.retail_app_ecs.module.checkout_service.aws_ecs_service.this is a container service: its 2 identity binding(s) are facts only, and no service account is attached for it (the draft writes service accounts for servers (the EC2 family); the identities of containers, functions and clusters are stated as facts and left to a person)
- plan producer: stacktoit-stackitsa 0.1.0
-
Render Nothing to show
The identity plan writes no STACKIT resource for this unit, so nothing is rendered from it. The blocks the draft holds for the workload itself are written by another generator, which records no plan.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The identity plan writes no resource for this unit, so the checks over the identity part of the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: attach-complete ok=true: 0 attachment block(s) written as resources, each with a project, a region, a server and a written account
- check: final-artifact ok=true: the service account resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role
-
Source Established
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 14-18). It is part of module.retail_app_ecs.module.checkout_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role (../../lib/ecs/service/iam.tf:14) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/5
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_checkout_service_task_execution_role (from the policies of module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_checkout_service_task_execution_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-101825075cda
- recorded: trace: TR-b9a8861fdbd3
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/5
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-ecs = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 109-114); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_checkout_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 100-103); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_execution_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_execution_role
- block in the draft: stackit_service_account.retail_app_ecs_checkout_service_task_execution_role
- block in the draft: terraform/identity.tf:100-103
- block in the draft: terraform/identity.tf:109-114
- trace: TR-101825075cda
- trace: TR-b9a8861fdbd3
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.checkout_service.aws_iam_role.task_execution_role is "retail-app-ecs-checkout-service-task-execution-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role
-
Source Established
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 31-35). It is part of module.retail_app_ecs.module.checkout_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role (../../lib/ecs/service/iam.tf:31) — RECONFIGURE / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/16
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_checkout_service_task_role (from the policies of module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_checkout_service_task_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: linked-dependency-unread
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-822b8a98ff0d
- recorded: trace: TR-8e7b4456f29a
-
Semantic claim Open items
The engine read 7 statements the source makes about this resource and decided what happens to each; 7 of them are critical settings, 6 of those still open.
- 6 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/16
module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-customer-policy = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: linked-dependency:aws_dynamodb_table = KNOWN, CRITICAL, REVIEW
- claim: permissions = UNKNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_role: written as an active resource (terraform/identity.tf, lines 132-137); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_checkout_service_task_role: written as an active resource (terraform/identity.tf, lines 123-126); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_checkout_service_task_role
- block in the draft: stackit_service_account.retail_app_ecs_checkout_service_task_role
- block in the draft: terraform/identity.tf:123-126
- block in the draft: terraform/identity.tf:132-137
- trace: TR-822b8a98ff0d
- trace: TR-8e7b4456f29a
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 2 findings, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions boundary. …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: This unit names module.dependencies.module.dynamodb_carts.aws_dynamodb_table.this (aws_dynamodb_table), whose own decision the target does not carry (it is REDESIGN), and the semantic contract of aws_iam_role does not read aws_dynamodb_table, so what the reference becomes is not assessed.
- Open: the name of module.retail_app_ecs.module.checkout_service.aws_iam_role.task_role is "retail-app-ecs-checkout-service-task-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same name is …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.checkout_service.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.checkout_service.aws_security_group.this is an AWS security group, declared in ../../lib/ecs/service/sg.tf (lines 1-18). It is part of module.retail_app_ecs.module.checkout_service. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/17
module.retail_app_ecs.module.checkout_service.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.checkout_service.aws_security_group.this
-
Evidence Established
The source states 2 rules for this unit. 2 rules are stated exactly.
- ingress tcp port 8080 from 0.0.0.0/0
- egress any protocol to 0.0.0.0/0
In the source: ../../lib/ecs/service/sg.tf, lines 1-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/sg.tf lines 1-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.retail_app_ecs.module.checkout_service.aws_security_group.this#egress#0#909db684902e
- source rule: module.retail_app_ecs.module.checkout_service.aws_security_group.this#ingress#0#3d8f71de8dab
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.checkout_service.aws_security_group.this: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.checkout_service.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.checkout_service.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.checkout_service.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 4 left to a person to review
- 2 carried into the draft and listed in the ledger
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/17
module.retail_app_ecs.module.checkout_service.aws_security_group.this- claim: egress-rule-protocol = KNOWN, CRITICAL, REVIEW
- claim: egress-sources = KNOWN, CRITICAL, REVIEW
- claim: ingress-sources = KNOWN, CRITICAL, LEDGER
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, LEDGER
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.checkout_service.aws_security_group.this: 2 rules
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.checkout_service.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.checkout_service.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 14 evidenced facts about STACKIT:
- 4 about values the API rejects
- 3 about rules or values it creates by default
- 3 about limits
- 4 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: ether-type-default-ipv4 (DEFAULT_RULE, stackit_security_group_rule.ether_type)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: ip-range-family-must-match-ether-type (REJECTS, stackit_security_group_rule.ip_range)
- constraint relied on: port-range-bounds (LIMIT, stackit_security_group_rule.port_range)
- constraint relied on: port-range-is-destination-port (SEMANTIC, stackit_security_group_rule.port_range)
- constraint relied on: protocol-name-values (LIMIT, stackit_security_group_rule.protocol.name)
- constraint relied on: protocol-name-xor-number (REJECTS, stackit_security_group_rule.protocol.name)
- constraint relied on: remote-security-group-by-id (SEMANTIC, stackit_security_group_rule.remote_security_group_id)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 1 rule for this unit. Of their 19 fields: 7 carried exactly, 3 needing a value you supply, 8 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_checkout_service_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_checkout_service_this: name needs a value you supply
- project_id needs a value you supply (on 2 resources)
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_checkout_service_this- decision:
DEC-GEN-CONVERT-POD-SEGMENTATION/module.retail_app_ecs.module.checkout_service.aws_security_group.this(aliasconvert:module.retail_app_ecs.module.checkout_service.aws_security_group.this:security-group:POD_SEGMENTATION) - field: stackit_security_group.retail_app_ecs_checkout_service_this.default_egress.ipv4 = SAFE_OMISSION: the source allows all IPv4 egress, which is the allow-all IPv4 egress rule STACKIT creates on every new group: it is covered by the STACKIT default egress rules and not produced (a duplicate is rejected with HTTP 409)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.default_egress.ipv6 = SAFE_OMISSION: the network has no IPv6 prefix (its VPC module.vpc.module.vpc.aws_vpc.this assigns no IPv6 CIDR block and the estate associates none), and the drafted STACKIT network has none either, so the allow-all IPv6 egress rule STACKIT creates on every new group acts on no traffic, whatever IPv6 egress rules the source lists; if an IPv6 prefix is added to the network later, delete that rule (stackit security-group rule list, then delete with the security group id) or write the equivalent rules of the source: decide then
- field: stackit_security_group.retail_app_ecs_checkout_service_this.labels = SAFE_OMISSION: the source group sets no tags, so there are no labels to write
- field: stackit_security_group.retail_app_ecs_checkout_service_this.name = VARIABLE_REQUIRED: the source value comes from an overridable root variable (var.environment_name)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_checkout_service_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_checkout_service_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- field: stackit_security_group_rule.retail_app_ecs_checkout_service_this_ingress_1.project_id = VARIABLE_REQUIRED: the STACKIT project the rule belongs to
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
- plan rule: awssg.rule
-
Render Established
The draft writes 2 resources of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_checkout_service_this: written as an active resource (terraform/security.tf, lines 138-141)
- stackit_security_group_rule.retail_app_ecs_checkout_service_this_ingress_1: written as an active resource (terraform/security.tf, lines 143-156)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:138-141
- block in the draft: terraform/security.tf:143-156
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_checkout_service_this
- resource address: stackit_security_group_rule.retail_app_ecs_checkout_service_this_ingress_1
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 1 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_checkout_service_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_checkout_service_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_checkout_service_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_checkout_service_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.orders_service.aws_ecs_service.this
-
Source Established
module.retail_app_ecs.module.orders_service.aws_ecs_service.this is a container service (it keeps container tasks running), declared in ../../lib/ecs/service/ecs.tf (lines 136-175). It is part of module.retail_app_ecs.module.orders_service. It names 2 identities it runs as. This trace follows the identity of the workload: which identity it runs as and what the plan does with it on STACKIT.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/41
module.retail_app_ecs.module.orders_service.aws_ecs_service.this- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_service
- unit: module.retail_app_ecs.module.orders_service.aws_ecs_service.this
-
Evidence Established
The source names 2 identities this workload runs as.
- the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): runs as module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role (a role)
- the application's identity inside a container task: runs as module.retail_app_ecs.module.orders_service.aws_iam_role.task_role (a role)
In the source: ../../lib/ecs/service/ecs.tf, lines 136-175.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/ecs.tf lines 136-175
- binding: module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this#execution_role_arn (EXECUTION_ROLE, EXECUTION, KNOWN)
- binding: module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this#task_role_arn (TASK_ROLE, TASK, KNOWN)
-
Resolution proof Established
2 references are resolved for this unit: 2 proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- a step to the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): refers to module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role, proven by a direct reference
- a step to the application's identity inside a container task: refers to module.retail_app_ecs.module.orders_service.aws_iam_role.task_role, proven by a direct reference
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.orders_service.aws_ecs_service.this- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this execution_role_arn
- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this task_role_arn
-
Semantic claim Open items
The engine read 16 statements the source makes about this workload and decided what happens to each; 16 of them are critical settings, 16 of those still open.
- 16 left to a person to review
- 107 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/41
module.retail_app_ecs.module.orders_service.aws_ecs_service.this- claim: linked-dependency:aws_secretsmanager_secret_version = KNOWN, CRITICAL, REVIEW
- claim: service-connect-values = KNOWN, CRITICAL, REVIEW
- claim: service-desired-count = KNOWN, CRITICAL, REVIEW
- claim: service-discovery = KNOWN, CRITICAL, REVIEW
- claim: service-execute-command = KNOWN, CRITICAL, REVIEW
- claim: service-network-placement = KNOWN, CRITICAL, REVIEW
- claim: service-public-ip-setting = KNOWN, CRITICAL, REVIEW
- claim: service-task-definition = KNOWN, CRITICAL, REVIEW
- claim: task-definition = KNOWN, CRITICAL, REVIEW
- claim: td-container-definitions = KNOWN, CRITICAL, REVIEW
- claim: td-container-image-registry = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-plaintext-secret-env = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-secret-references = UNKNOWN, CRITICAL, REVIEW
- claim: td-execution-role-arn = KNOWN, CRITICAL, REVIEW
- claim: td-network-mode = KNOWN, CRITICAL, REVIEW
- claim: td-task-role-arn = KNOWN, CRITICAL, REVIEW
-
Intent Open items
This workload is not made of servers, so no service account is attached to it: the identities it names are stated as facts and left to a person.
- The unit is a container service (it keeps container tasks running)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity:module.retail_app_ecs.module.orders_service.aws_ecs_service.this- intent family: IDENTITY
- intent: identity:module.retail_app_ecs.module.orders_service.aws_ecs_service.this
-
Target capability Established
The target is a STACKIT service account (stackit_service_account) attached to a server: a server takes one service account, and the account holds the roles the workload needs.
- Service: available
- API: write supported
- Terraform: resource available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity.server-service-account- capability: identity.server-service-account
- provider version: 0.121.0
-
Transformation Open items
No STACKIT service account is attached to this workload: it is not made of servers (the draft writes service accounts for servers, and the identity of a container, a function or a cluster is stated as a fact), or the source does not decide which identity it runs as, so nothing is attached and a person decides.
- 2 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitsa:facts:module.retail_app_ecs.module.orders_service.aws_ecs_service.this:module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this#execution_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.orders_service.aws_ecs_service.this pulls images, injects secrets and writes logs: the platform agent's role has no STACKIT counterpart to attach - manual action: alias
stackitsa:facts:module.retail_app_ecs.module.orders_service.aws_ecs_service.this:module.retail_app_ecs.module.orders_service.aws_ecs_task_definition.this#task_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.orders_service.aws_ecs_service.this gets its application identity on STACKIT (a service account of its own, workload federation): the draft does not write it - no target: MANUAL_REVIEW: module.retail_app_ecs.module.orders_service.aws_ecs_service.this is a container service: its 2 identity binding(s) are facts only, and no service account is attached for it (the draft writes service accounts for servers (the EC2 family); the identities of containers, functions and clusters are stated as facts and left to a person)
- plan producer: stacktoit-stackitsa 0.1.0
-
Render Nothing to show
The identity plan writes no STACKIT resource for this unit, so nothing is rendered from it. The blocks the draft holds for the workload itself are written by another generator, which records no plan.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The identity plan writes no resource for this unit, so the checks over the identity part of the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: attach-complete ok=true: 0 attachment block(s) written as resources, each with a project, a region, a server and a written account
- check: final-artifact ok=true: the service account resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role
-
Source Established
module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 14-18). It is part of module.retail_app_ecs.module.orders_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role (../../lib/ecs/service/iam.tf:14) — RECONFIGURE / LOW
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/39
module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_orders_service_task_execution_role (from the policies of module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_orders_service_task_execution_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: linked-dependency-unread
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-0054e8101f59
- recorded: trace: TR-a77098085913
-
Semantic claim Open items
The engine read 7 statements the source makes about this resource and decided what happens to each; 7 of them are critical settings, 6 of those still open.
- 6 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/39
module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-ecs = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: linked-dependency:aws_secretsmanager_secret = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 156-161); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_orders_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 147-150); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_execution_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_execution_role
- block in the draft: stackit_service_account.retail_app_ecs_orders_service_task_execution_role
- block in the draft: terraform/identity.tf:147-150
- block in the draft: terraform/identity.tf:156-161
- trace: TR-0054e8101f59
- trace: TR-a77098085913
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 3 findings, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: This unit names module.retail_app_ecs.aws_secretsmanager_secret.mq (aws_secretsmanager_secret), whose own decision the target does not carry (it is RECONFIGURE, but the converter does not draft this aws_secretsmanager_secret (the generator skips this case, or only records it against a …
- warning: This unit names module.retail_app_ecs.aws_secretsmanager_secret.orders_db (aws_secretsmanager_secret), whose own decision the target does not carry (it is RECONFIGURE, but the converter does not draft this aws_secretsmanager_secret (the generator skips this case, or only records it against …
- Open: the name of module.retail_app_ecs.module.orders_service.aws_iam_role.task_execution_role is "retail-app-ecs-orders-service-task-execution-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.orders_service.aws_iam_role.task_role
-
Source Established
module.retail_app_ecs.module.orders_service.aws_iam_role.task_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 31-35). It is part of module.retail_app_ecs.module.orders_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.orders_service.aws_iam_role.task_role (../../lib/ecs/service/iam.tf:31) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/18
module.retail_app_ecs.module.orders_service.aws_iam_role.task_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.orders_service.aws_iam_role.task_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_orders_service_task_role (from the policies of module.retail_app_ecs.module.orders_service.aws_iam_role.task_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_orders_service_task_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-60af0bd02bd2
- recorded: trace: TR-cf173263597f
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/18
module.retail_app_ecs.module.orders_service.aws_iam_role.task_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-customer-policy = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_role: written as an active resource (terraform/identity.tf, lines 178-183); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_orders_service_task_role: written as an active resource (terraform/identity.tf, lines 169-172); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_orders_service_task_role
- block in the draft: stackit_service_account.retail_app_ecs_orders_service_task_role
- block in the draft: terraform/identity.tf:169-172
- block in the draft: terraform/identity.tf:178-183
- trace: TR-60af0bd02bd2
- trace: TR-cf173263597f
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.orders_service.aws_iam_role.task_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions boundary. The …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.orders_service.aws_iam_role.task_role is "retail-app-ecs-orders-service-task-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same name is …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.orders_service.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.orders_service.aws_security_group.this is an AWS security group, declared in ../../lib/ecs/service/sg.tf (lines 1-18). It is part of module.retail_app_ecs.module.orders_service. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/19
module.retail_app_ecs.module.orders_service.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.orders_service.aws_security_group.this
-
Evidence Established
The source states 2 rules for this unit. 2 rules are stated exactly.
- ingress tcp port 8080 from 0.0.0.0/0
- egress any protocol to 0.0.0.0/0
In the source: ../../lib/ecs/service/sg.tf, lines 1-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/sg.tf lines 1-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.retail_app_ecs.module.orders_service.aws_security_group.this#egress#0#909db684902e
- source rule: module.retail_app_ecs.module.orders_service.aws_security_group.this#ingress#0#3d8f71de8dab
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.orders_service.aws_security_group.this: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.orders_service.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.orders_service.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.orders_service.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 4 left to a person to review
- 2 carried into the draft and listed in the ledger
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/19
module.retail_app_ecs.module.orders_service.aws_security_group.this- claim: egress-rule-protocol = KNOWN, CRITICAL, REVIEW
- claim: egress-sources = KNOWN, CRITICAL, REVIEW
- claim: ingress-sources = KNOWN, CRITICAL, LEDGER
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, LEDGER
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.orders_service.aws_security_group.this: 2 rules
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.orders_service.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.orders_service.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 14 evidenced facts about STACKIT:
- 4 about values the API rejects
- 3 about rules or values it creates by default
- 3 about limits
- 4 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: ether-type-default-ipv4 (DEFAULT_RULE, stackit_security_group_rule.ether_type)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: ip-range-family-must-match-ether-type (REJECTS, stackit_security_group_rule.ip_range)
- constraint relied on: port-range-bounds (LIMIT, stackit_security_group_rule.port_range)
- constraint relied on: port-range-is-destination-port (SEMANTIC, stackit_security_group_rule.port_range)
- constraint relied on: protocol-name-values (LIMIT, stackit_security_group_rule.protocol.name)
- constraint relied on: protocol-name-xor-number (REJECTS, stackit_security_group_rule.protocol.name)
- constraint relied on: remote-security-group-by-id (SEMANTIC, stackit_security_group_rule.remote_security_group_id)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 1 rule for this unit. Of their 19 fields: 7 carried exactly, 3 needing a value you supply, 8 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_orders_service_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_orders_service_this: name needs a value you supply
- project_id needs a value you supply (on 2 resources)
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_orders_service_this- decision:
DEC-GEN-CONVERT-POD-SEGMENTATION/module.retail_app_ecs.module.orders_service.aws_security_group.this(aliasconvert:module.retail_app_ecs.module.orders_service.aws_security_group.this:security-group:POD_SEGMENTATION) - field: stackit_security_group.retail_app_ecs_orders_service_this.default_egress.ipv4 = SAFE_OMISSION: the source allows all IPv4 egress, which is the allow-all IPv4 egress rule STACKIT creates on every new group: it is covered by the STACKIT default egress rules and not produced (a duplicate is rejected with HTTP 409)
- field: stackit_security_group.retail_app_ecs_orders_service_this.default_egress.ipv6 = SAFE_OMISSION: the network has no IPv6 prefix (its VPC module.vpc.module.vpc.aws_vpc.this assigns no IPv6 CIDR block and the estate associates none), and the drafted STACKIT network has none either, so the allow-all IPv6 egress rule STACKIT creates on every new group acts on no traffic, whatever IPv6 egress rules the source lists; if an IPv6 prefix is added to the network later, delete that rule (stackit security-group rule list, then delete with the security group id) or write the equivalent rules of the source: decide then
- field: stackit_security_group.retail_app_ecs_orders_service_this.labels = SAFE_OMISSION: the source group sets no tags, so there are no labels to write
- field: stackit_security_group.retail_app_ecs_orders_service_this.name = VARIABLE_REQUIRED: the source value comes from an overridable root variable (var.environment_name)
- field: stackit_security_group.retail_app_ecs_orders_service_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_orders_service_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_orders_service_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_orders_service_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_orders_service_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_orders_service_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_orders_service_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- field: stackit_security_group_rule.retail_app_ecs_orders_service_this_ingress_1.project_id = VARIABLE_REQUIRED: the STACKIT project the rule belongs to
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
- plan rule: awssg.rule
-
Render Established
The draft writes 2 resources of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_orders_service_this: written as an active resource (terraform/security.tf, lines 170-173)
- stackit_security_group_rule.retail_app_ecs_orders_service_this_ingress_1: written as an active resource (terraform/security.tf, lines 175-188)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:170-173
- block in the draft: terraform/security.tf:175-188
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_orders_service_this
- resource address: stackit_security_group_rule.retail_app_ecs_orders_service_this_ingress_1
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 1 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_orders_service_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_orders_service_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_orders_service_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_orders_service_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.retail_app_ecs.module.ui_service.aws_ecs_service.this
-
Source Established
module.retail_app_ecs.module.ui_service.aws_ecs_service.this is a container service (it keeps container tasks running), declared in ../../lib/ecs/service/ecs.tf (lines 136-175). It is part of module.retail_app_ecs.module.ui_service. It names 2 identities it runs as. This trace follows the identity of the workload: which identity it runs as and what the plan does with it on STACKIT.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/43
module.retail_app_ecs.module.ui_service.aws_ecs_service.this- knowledge base case: ecs-to-ske
- knowledge base rule: aws.ecs
- source type: aws_ecs_service
- unit: module.retail_app_ecs.module.ui_service.aws_ecs_service.this
-
Evidence Established
The source names 2 identities this workload runs as.
- the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): runs as module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role (a role)
- the application's identity inside a container task: runs as module.retail_app_ecs.module.ui_service.aws_iam_role.task_role (a role)
In the source: ../../lib/ecs/service/ecs.tf, lines 136-175.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/ecs.tf lines 136-175
- binding: module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this#execution_role_arn (EXECUTION_ROLE, EXECUTION, KNOWN)
- binding: module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this#task_role_arn (TASK_ROLE, TASK, KNOWN)
-
Resolution proof Established
2 references are resolved for this unit: 2 proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- a step to the platform agent's identity that starts the workload (it pulls images, injects secrets and writes logs): refers to module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role, proven by a direct reference
- a step to the application's identity inside a container task: refers to module.retail_app_ecs.module.ui_service.aws_iam_role.task_role, proven by a direct reference
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.ui_service.aws_ecs_service.this- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this execution_role_arn
- proof: DIRECT_REFERENCE/EXACT at module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this task_role_arn
-
Semantic claim Open items
The engine read 16 statements the source makes about this workload and decided what happens to each; 16 of them are critical settings, 16 of those still open.
- 16 left to a person to review
- 106 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/43
module.retail_app_ecs.module.ui_service.aws_ecs_service.this- claim: service-connect-values = KNOWN, CRITICAL, REVIEW
- claim: service-desired-count = KNOWN, CRITICAL, REVIEW
- claim: service-discovery = KNOWN, CRITICAL, REVIEW
- claim: service-execute-command = KNOWN, CRITICAL, REVIEW
- claim: service-load-balancer-target = UNKNOWN, CRITICAL, REVIEW
- claim: service-network-placement = KNOWN, CRITICAL, REVIEW
- claim: service-public-ip-setting = KNOWN, CRITICAL, REVIEW
- claim: service-task-definition = KNOWN, CRITICAL, REVIEW
- claim: task-definition = KNOWN, CRITICAL, REVIEW
- claim: td-container-definitions = KNOWN, CRITICAL, REVIEW
- claim: td-container-image-registry = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-plaintext-secret-env = UNKNOWN, CRITICAL, REVIEW
- claim: td-container-secret-references = UNKNOWN, CRITICAL, REVIEW
- claim: td-execution-role-arn = KNOWN, CRITICAL, REVIEW
- claim: td-network-mode = KNOWN, CRITICAL, REVIEW
- claim: td-task-role-arn = KNOWN, CRITICAL, REVIEW
-
Intent Open items
This workload is not made of servers, so no service account is attached to it: the identities it names are stated as facts and left to a person.
- The unit is a container service (it keeps container tasks running)
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity:module.retail_app_ecs.module.ui_service.aws_ecs_service.this- intent family: IDENTITY
- intent: identity:module.retail_app_ecs.module.ui_service.aws_ecs_service.this
-
Target capability Established
The target is a STACKIT service account (stackit_service_account) attached to a server: a server takes one service account, and the account holds the roles the workload needs.
- Service: available
- API: write supported
- Terraform: resource available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
identity.server-service-account- capability: identity.server-service-account
- provider version: 0.121.0
-
Transformation Open items
No STACKIT service account is attached to this workload: it is not made of servers (the draft writes service accounts for servers, and the identity of a container, a function or a cluster is stated as a fact), or the source does not decide which identity it runs as, so nothing is attached and a person decides.
- 2 manual actions, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitsa:facts:module.retail_app_ecs.module.ui_service.aws_ecs_service.this:module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this#execution_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.ui_service.aws_ecs_service.this pulls images, injects secrets and writes logs: the platform agent's role has no STACKIT counterpart to attach - manual action: alias
stackitsa:facts:module.retail_app_ecs.module.ui_service.aws_ecs_service.this:module.retail_app_ecs.module.ui_service.aws_ecs_task_definition.this#task_role_arn(BEFORE_PILOT): Decide how module.retail_app_ecs.module.ui_service.aws_ecs_service.this gets its application identity on STACKIT (a service account of its own, workload federation): the draft does not write it - no target: MANUAL_REVIEW: module.retail_app_ecs.module.ui_service.aws_ecs_service.this is a container service: its 2 identity binding(s) are facts only, and no service account is attached for it (the draft writes service accounts for servers (the EC2 family); the identities of containers, functions and clusters are stated as facts and left to a person)
- plan producer: stacktoit-stackitsa 0.1.0
-
Render Nothing to show
The identity plan writes no STACKIT resource for this unit, so nothing is rendered from it. The blocks the draft holds for the workload itself are written by another generator, which records no plan.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The identity plan writes no resource for this unit, so the checks over the identity part of the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: attach-complete ok=true: 0 attachment block(s) written as resources, each with a project, a region, a server and a written account
- check: final-artifact ok=true: the service account resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role
-
Source Established
module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 14-18). It is part of module.retail_app_ecs.module.ui_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role (../../lib/ecs/service/iam.tf:14) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/6
module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_ui_service_task_execution_role (from the policies of module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_ui_service_task_execution_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-02dcd9e3db54
- recorded: trace: TR-be8af2d2983d
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/6
module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-ecs = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 200-205); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_ui_service_task_execution_role: written as an active resource (terraform/identity.tf, lines 191-194); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_execution_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_execution_role
- block in the draft: stackit_service_account.retail_app_ecs_ui_service_task_execution_role
- block in the draft: terraform/identity.tf:191-194
- block in the draft: terraform/identity.tf:200-205
- trace: TR-02dcd9e3db54
- trace: TR-be8af2d2983d
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.ui_service.aws_iam_role.task_execution_role is "retail-app-ecs-ui-service-task-execution-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.ui_service.aws_iam_role.task_role
-
Source Established
module.retail_app_ecs.module.ui_service.aws_iam_role.task_role is a resource of the source, declared in ../../lib/ecs/service/iam.tf (lines 31-35). It is part of module.retail_app_ecs.module.ui_service. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.retail_app_ecs.module.ui_service.aws_iam_role.task_role (../../lib/ecs/service/iam.tf:31) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/20
module.retail_app_ecs.module.ui_service.aws_iam_role.task_role- knowledge base case: role-workload-execution
- knowledge base rule: aws.iam_role
- source type: aws_iam_role
- unit: module.retail_app_ecs.module.ui_service.aws_iam_role.task_role
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- Role assignments of service account retail_app_ecs_ui_service_task_role (from the policies of module.retail_app_ecs.module.ui_service.aws_iam_role.task_role); provider experiment "iam".
- AWS actions do not translate into STACKIT roles one to one: the roles are var.retail_app_ecs_ui_service_task_role_project_roles, chosen by the architect.
- TARGET MATURITY: EXPERIMENTAL — stackit_authorization_project_role_assignment is part of the experimental feature "iam" of the pinned STACKIT provider: "likely going to undergo significant changes or be removed in the future" (enabled in terraform.tf experiments).
- The permissions of the source policies become the project role assignments below (provider experiment "iam").
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: rule line: rule aws.iam_role/role-workload-execution · KB 0.384.0 · target maturity EXPERIMENTAL · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-14c0a005bdbf
- recorded: trace: TR-759ef9228645
-
Semantic claim Open items
The engine read 6 statements the source makes about this resource and decided what happens to each; 6 of them are critical settings, 5 of those still open.
- 5 left to a person to review
- 1 not applicable here
- 97 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/20
module.retail_app_ecs.module.ui_service.aws_iam_role.task_role- claim: facet-link-role = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: iam-managed-customer-policy = KNOWN, CRITICAL, REVIEW
- claim: iam-trust-service-workload = KNOWN, CRITICAL, REVIEW
- claim: permissions = KNOWN, CRITICAL, REVIEW
- claim: tcfp-iam-role-policy-attachment--policy-arn = KNOWN, CRITICAL, REVIEW
- claim: trust = KNOWN, CRITICAL, REVIEW
-
Render Established
The draft holds 2 blocks for this unit, written as active Terraform.
- stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_role: written as an active resource (terraform/identity.tf, lines 222-227); the whole comment of the block is in engineering/trace/identity.md
- stackit_service_account.retail_app_ecs_ui_service_task_role: written as an active resource (terraform/identity.tf, lines 213-216); the whole comment of the block is in engineering/trace/identity.md
In terraform/identity.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/identity.tf
stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_role- block in the draft: stackit_authorization_project_role_assignment.retail_app_ecs_ui_service_task_role
- block in the draft: stackit_service_account.retail_app_ecs_ui_service_task_role
- block in the draft: terraform/identity.tf:213-216
- block in the draft: terraform/identity.tf:222-227
- trace: TR-14c0a005bdbf
- trace: TR-759ef9228645
-
Residual difference Open items
The draft states, for this unit: 1 property it does not carry, 1 finding, 1 open item. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.retail_app_ecs.module.ui_service.aws_iam_role.task_role): assume_role_policy, name = (reads a variable; its default is not printed) — stackit_service_account has a name and a project only (pinned provider): no trust policy, path, session duration or permissions boundary. The …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- Open: the name of module.retail_app_ecs.module.ui_service.aws_iam_role.task_role is "retail-app-ecs-ui-service-task-role": a STACKIT service account name has at most 20 characters (lowercase letters, digits and single dashes) and is unique in a project (a second account of the same name is refused), so …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
module.retail_app_ecs.module.ui_service.aws_security_group.this
-
Source Established
module.retail_app_ecs.module.ui_service.aws_security_group.this is an AWS security group, declared in ../../lib/ecs/service/sg.tf (lines 1-18). It is part of module.retail_app_ecs.module.ui_service. It states 2 rules.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/21
module.retail_app_ecs.module.ui_service.aws_security_group.this- knowledge base case: sg
- knowledge base rule: aws.security_group
- source type: aws_security_group
- unit: module.retail_app_ecs.module.ui_service.aws_security_group.this
-
Evidence Established
The source states 2 rules for this unit. 2 rules are stated exactly.
- ingress tcp port 8080 from 0.0.0.0/0
- egress any protocol to 0.0.0.0/0
In the source: ../../lib/ecs/service/sg.tf, lines 1-18.
Expert: identifiers
Artefact: SOURCE_FILE ../../lib/ecs/service/sg.tf lines 1-18
- evidence of the stateful assumption: docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-connection-tracking.html
- source rule: module.retail_app_ecs.module.ui_service.aws_security_group.this#egress#0#909db684902e
- source rule: module.retail_app_ecs.module.ui_service.aws_security_group.this#ingress#0#3d8f71de8dab
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 named but not proven. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of module.retail_app_ecs.module.ui_service.aws_security_group.this: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.retail_app_ecs.module.ui_service.aws_security_group.this- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.retail_app_ecs.module.ui_service.aws_security_group.this vpc_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.retail_app_ecs.module.ui_service.aws_security_group.this vpc_id
-
Semantic claim Open items
The engine read 7 statements the source makes about this group and decided what happens to each; 7 of them are critical settings, 7 of those still open.
- 1 not supported on STACKIT
- 4 left to a person to review
- 2 carried into the draft and listed in the ledger
- 109 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/21
module.retail_app_ecs.module.ui_service.aws_security_group.this- claim: egress-rule-protocol = KNOWN, CRITICAL, REVIEW
- claim: egress-sources = KNOWN, CRITICAL, REVIEW
- claim: ingress-sources = KNOWN, CRITICAL, LEDGER
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: rule-ports = KNOWN, CRITICAL, LEDGER
- claim: security-group-vpc-membership = KNOWN, CRITICAL, UNSUPPORTED
- claim: stateful = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for 1 security group with 2 rules in all. The policy is read as AWS reads it: groups are stateful, so the answer to an allowed flow is allowed too.
- Group module.retail_app_ecs.module.ui_service.aws_security_group.this: 2 rules
- 1 value that a variable or the instances decide
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
security:module.retail_app_ecs.module.ui_service.aws_security_group.this- intent family: SECURITY_POLICY
- intent: security:module.retail_app_ecs.module.ui_service.aws_security_group.this
-
Target capability Established
The target is the STACKIT security group (stackit_security_group and stackit_security_group_rule): a project-scoped group and, separately, each of its rules.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
- The plan of this unit relies on 14 evidenced facts about STACKIT:
- 4 about values the API rejects
- 3 about rules or values it creates by default
- 3 about limits
- 4 about how it behaves
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.security-group- capability: network.security-group
- constraint relied on: default-egress-rules (DEFAULT_RULE, api:SecurityGroup.rules)
- constraint relied on: duplicate-default-egress-rule-rejected (REJECTS, stackit_security_group_rule)
- constraint relied on: ether-type-default-ipv4 (DEFAULT_RULE, stackit_security_group_rule.ether_type)
- constraint relied on: group-is-project-scoped (SEMANTIC, stackit_security_group.project_id)
- constraint relied on: group-labels-format (LIMIT, stackit_security_group.labels)
- constraint relied on: group-name-validator (REJECTS, stackit_security_group.name)
- constraint relied on: ip-range-family-must-match-ether-type (REJECTS, stackit_security_group_rule.ip_range)
- constraint relied on: port-range-bounds (LIMIT, stackit_security_group_rule.port_range)
- constraint relied on: port-range-is-destination-port (SEMANTIC, stackit_security_group_rule.port_range)
- constraint relied on: protocol-name-values (LIMIT, stackit_security_group_rule.protocol.name)
- constraint relied on: protocol-name-xor-number (REJECTS, stackit_security_group_rule.protocol.name)
- constraint relied on: remote-security-group-by-id (SEMANTIC, stackit_security_group_rule.remote_security_group_id)
- constraint relied on: stateful-default-true (DEFAULT_RULE, stackit_security_group.stateful)
- constraint relied on: stateful-return-traffic (SEMANTIC, stackit_security_group.stateful)
- known issue: backend-security-group-rule-port-range-min-zero-rejected
- known issue: backend-security-group-rule-port-range-zero-zero-normalised
- provider version: 0.121.0
-
Transformation Open items
The plan holds 1 group and 1 rule for this unit. Of their 19 fields: 7 carried exactly, 3 needing a value you supply, 8 left out on purpose, 1 without a STACKIT equivalent.
- stackit_security_group.retail_app_ecs_ui_service_this: vpc_id has no STACKIT equivalent
- stackit_security_group.retail_app_ecs_ui_service_this: name needs a value you supply
- project_id needs a value you supply (on 2 resources)
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
stackit_security_group.retail_app_ecs_ui_service_this- decision:
DEC-GEN-CONVERT-POD-SEGMENTATION/module.retail_app_ecs.module.ui_service.aws_security_group.this(aliasconvert:module.retail_app_ecs.module.ui_service.aws_security_group.this:security-group:POD_SEGMENTATION) - field: stackit_security_group.retail_app_ecs_ui_service_this.default_egress.ipv4 = SAFE_OMISSION: the source allows all IPv4 egress, which is the allow-all IPv4 egress rule STACKIT creates on every new group: it is covered by the STACKIT default egress rules and not produced (a duplicate is rejected with HTTP 409)
- field: stackit_security_group.retail_app_ecs_ui_service_this.default_egress.ipv6 = SAFE_OMISSION: the network has no IPv6 prefix (its VPC module.vpc.module.vpc.aws_vpc.this assigns no IPv6 CIDR block and the estate associates none), and the drafted STACKIT network has none either, so the allow-all IPv6 egress rule STACKIT creates on every new group acts on no traffic, whatever IPv6 egress rules the source lists; if an IPv6 prefix is added to the network later, delete that rule (stackit security-group rule list, then delete with the security group id) or write the equivalent rules of the source: decide then
- field: stackit_security_group.retail_app_ecs_ui_service_this.labels = SAFE_OMISSION: the source group sets no tags, so there are no labels to write
- field: stackit_security_group.retail_app_ecs_ui_service_this.name = VARIABLE_REQUIRED: the source value comes from an overridable root variable (var.environment_name)
- field: stackit_security_group.retail_app_ecs_ui_service_this.name_prefix = SAFE_OMISSION: NOT CARRIED when the source sets it: AWS makes a unique name from the prefix; the STACKIT group takes the name field (the source's name, or one derived from the address), and a name allows nothing (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_ui_service_this.project_id = VARIABLE_REQUIRED: the STACKIT project the group belongs to (a group is project-scoped)
- field: stackit_security_group.retail_app_ecs_ui_service_this.revoke_rules_on_delete = SAFE_OMISSION: NOT CARRIED when the source sets it: it makes AWS revoke the rules of a group before deleting it; a STACKIT group has no such attribute and no revoke-rules step (the pinned provider), and it states nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_ui_service_this.stateful = SAFE_OMISSION: the source group is stateful (AWS tracks connections) and a STACKIT group created without stateful is stateful: the attribute is not written
- field: stackit_security_group.retail_app_ecs_ui_service_this.tags_all = SAFE_OMISSION: tags_all is the tags merged with the provider's default tags and is computed by the AWS provider; a STACKIT group has no such attribute, and the effective tags are written as its labels (the tags that are not labels are named on the statement tags)
- field: stackit_security_group.retail_app_ecs_ui_service_this.timeouts = SAFE_OMISSION: NOT CARRIED when the source sets it: the timeouts of the AWS provider for creating and deleting the group; a STACKIT group has none, and they state nothing the group allows (NON_CRITICAL)
- field: stackit_security_group.retail_app_ecs_ui_service_this.vpc_id = UNSUPPORTED: a STACKIT security group belongs to a project, not to a network: the resource has no network attribute, so the source's VPC membership is not carried
- field: stackit_security_group_rule.retail_app_ecs_ui_service_this_ingress_1.project_id = VARIABLE_REQUIRED: the STACKIT project the rule belongs to
- plan producer: stacktoit-awssg 0.1.0
- plan rule: awssg.group
- plan rule: awssg.rule
-
Render Established
The draft writes 2 resources of this unit as active Terraform.
- stackit_security_group.retail_app_ecs_ui_service_this: written as an active resource (terraform/security.tf, lines 202-205)
- stackit_security_group_rule.retail_app_ecs_ui_service_this_ingress_1: written as an active resource (terraform/security.tf, lines 207-220)
In terraform/security.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/security.tf
- block in the draft: terraform/security.tf:202-205
- block in the draft: terraform/security.tf:207-220
- file the plan renders into: security.tf
- resource address: stackit_security_group.retail_app_ecs_ui_service_this
- resource address: stackit_security_group_rule.retail_app_ecs_ui_service_this_ingress_1
-
Validation Open items
Every check over the draft of this unit was met. The plan also asks for 1 thing to be shown on STACKIT, which only a plan or apply there can do.
- Checked: the plan is internally consistent
- Checked: the plan was written as Terraform that parses
- Checked: every rule written as a resource names exactly one source or destination, a direction and its group
- Checked: the Terraform that was written, read back, says exactly what the plan says: nothing missing, nothing added, no rule written that the plan leaves open
- Checked: the security group resources of the files that were finally written, read back, still say exactly what the plan says, after the draft was assembled
- Still to show: every rendered stackit_security_group_rule allows no more than the source rule it derives from, and the plan's open decisions are not rendered as if decided
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the security group resources of the written files read back as the plan (12 written resources, 57 attributes and 10 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (12 written resources, 57 attributes and 10 references compared in the draft)
- check: rule-has-one-remote ok=true: 1 rule block(s) written as resources, each with a direction, its group and exactly one remote
- validation requirement: alias
awssg:security-equivalence(SECURITY_EQUIVALENCE)
-
Residual difference Open items
The plan records 2 remaining differences between this unit and its STACKIT target. None is accepted yet.
- stackit_security_group.retail_app_ecs_ui_service_this: Whether the members of one group can reach each other over IPv6 without a rule was not observed on STACKIT (IPv6 networks could not be created in a STACKIT project tested on 2026-10-08); IPv4 needs an explicit rule, which the draft writes where the source has one.
- stackit_security_group.retail_app_ecs_ui_service_this: On STACKIT a security group belongs to a project, not to a network; the source's network membership is not carried.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- residual: stackit_security_group.retail_app_ecs_ui_service_this ingress [intra-group IPv6 traffic not established]: source: the members of the group reach each other only where a rule of the group allows it; target: IPv6 intra-group behaviour was not observed: an IPv6 network could not be created in the STACKIT project tested on 2026-10-08; IPv4 needs an explicit rule and has one wherever the source has a self rule
- residual: stackit_security_group.retail_app_ecs_ui_service_this vpc_id [project-scoped on STACKIT]: source: the group belongs to one VPC and can be attached only to resources in it; target: the group is project-scoped and can be attached to network interfaces of any network of the project
module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log
-
Source Established
module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log is a log group (a named store of log events with a retention of its own), declared in .terraform/modules/vpc.vpc/vpc-flow-logs.tf (lines 65-75). It is switched off in the source. It is part of module.vpc.module.vpc. This trace follows the logs of the unit: where they go on STACKIT and for how long they are kept.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/63
module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log- knowledge base case: log-group
- knowledge base rule: aws.cloudwatch_log_group
- source type: aws_cloudwatch_log_group
- unit: module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log
-
Evidence Open items
The source states the retention and 0 settings and parts of this log group.
- The source states a retention that is stated
In the source: .terraform/modules/vpc.vpc/vpc-flow-logs.tf, lines 65-75.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/vpc-flow-logs.tf lines 65-75
- retention key: retention_in_days
-
Resolution proof Nothing to show
No reference to another resource has to be resolved for this unit: the model reads the settings of the unit and of the streams and filters that belong to it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one log group and what the source states of it; the model says nothing about the target.
- The unit is a log group (a named store of log events with a retention of its own)
- Retention: the source states a retention that is stated
- The unit has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
logs:module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log- intent family: OBSERVABILITY
- intent: logs:module.vpc.module.vpc.aws_cloudwatch_log_group.flow_log
-
Target capability Established
The target is the STACKIT Logs instance (stackit_logs_instance): one instance for each retention period, because the retention is one setting of the instance.
- Service: available
- API: write supported
- Terraform: resource available, data source available
- Maturity: ga
- Entitlement: not established
- Lifecycle: not established
- Region: not established
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
observability.logs- capability: observability.logs
- provider version: 0.121.0
-
Transformation Established
No STACKIT resource is planned for this unit: the source creates no instance of it, switches it off, or states a destination that STACKIT Logs does not take, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the log source (count or for_each yields none, or it is switched off): no stackit_logs_instance is drafted
- plan producer: stacktoit-stackitlogs 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.database
-
Source Established
module.vpc.module.vpc.aws_route_table.database is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 430-445). It is switched off in the source. It is part of module.vpc.module.vpc. It states 0 static routes.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/75
module.vpc.module.vpc.aws_route_table.database- knowledge base case: rt-local-only
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.database
-
Evidence Established
The source states no static route for this unit.
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 430-445.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 430-445
No identifiers.
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.vpc.module.vpc.aws_route_table.database- proof cause: source-not-present at module.vpc.module.vpc.aws_route_table.database vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table.database vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one routing table with 0 static routes and 0 attachments. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has none
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- The table has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.database- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.database
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed on a routed network of a project outside a Network Area; the default table of a Network Area was never read) or the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the table (count or for_each yields none, or it is switched off): no stackit_routing_table is drafted
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.elasticache
-
Source Established
module.vpc.module.vpc.aws_route_table.elasticache is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 747-757). It is switched off in the source. It is part of module.vpc.module.vpc. It states 0 static routes.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/76
module.vpc.module.vpc.aws_route_table.elasticache- knowledge base case: rt-local-only
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.elasticache
-
Evidence Established
The source states no static route for this unit.
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 747-757.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 747-757
No identifiers.
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.vpc.module.vpc.aws_route_table.elasticache- proof cause: source-not-present at module.vpc.module.vpc.aws_route_table.elasticache vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table.elasticache vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one routing table with 0 static routes and 0 attachments. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has none
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- The table has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.elasticache- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.elasticache
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed on a routed network of a project outside a Network Area; the default table of a Network Area was never read) or the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the table (count or for_each yields none, or it is switched off): no stackit_routing_table is drafted
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.intra
-
Source Established
module.vpc.module.vpc.aws_route_table.intra is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 866-881). It is switched off in the source. It is part of module.vpc.module.vpc. It states 0 static routes.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/77
module.vpc.module.vpc.aws_route_table.intra- knowledge base case: rt-local-only
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.intra
-
Evidence Established
The source states no static route for this unit.
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 866-881.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 866-881
No identifiers.
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.vpc.module.vpc.aws_route_table.intra- proof cause: source-not-present at module.vpc.module.vpc.aws_route_table.intra vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table.intra vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one routing table with 0 static routes and 0 attachments. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has none
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- The table has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.intra- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.intra
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed on a routed network of a project outside a Network Area; the default table of a Network Area was never read) or the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the table (count or for_each yields none, or it is switched off): no stackit_routing_table is drafted
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.private
-
Source Established
module.vpc.module.vpc.aws_route_table.private is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 296-311). Whether it exists is decided only when OpenTofu plans. It is part of module.vpc.module.vpc. It states 1 static route.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/78
module.vpc.module.vpc.aws_route_table.private- knowledge base case: rt-default-only-nat
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.private
-
Evidence Established
The source states 1 static route for this unit. 1 route is stated exactly.
- a route resource: 0.0.0.0/0 to a NAT gateway
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 296-311.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 296-311
- source route: module.vpc.module.vpc.aws_route.private_nat_gateway[0]
-
Resolution proof Open items
5 references are resolved for this unit: 1 proven, 1 named but not proven, 3 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the table of the route resource module.vpc.module.vpc.aws_route.private_nat_gateway[0]: no resource could be named, so the reference is not resolved
- the target of a route resource: 0.0.0.0/0 to a NAT gateway: refers to module.vpc.module.vpc.aws_nat_gateway.this[0], proven by a reference to one instance
- the table of the association module.vpc.module.vpc.aws_route_table_association.private: no resource could be named, so the reference is not resolved
- what the association module.vpc.module.vpc.aws_route_table_association.private attaches the table to: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.vpc.module.vpc.aws_route_table.private- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.vpc.module.vpc.aws_route_table.private vpc_id
- proof cause: selects-collapsed at module.vpc.module.vpc.aws_route.private_nat_gateway route_table_id
- proof cause: selects-collapsed at module.vpc.module.vpc.aws_route_table_association.private route_table_id
- proof cause: selects-collapsed at module.vpc.module.vpc.aws_route_table_association.private subnet_id
- proof: INDEXED_REFERENCE/EXACT at module.vpc.module.vpc.aws_route.private_nat_gateway nat_gateway_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.vpc.module.vpc.aws_route_table.private vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route.private_nat_gateway route_table_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table_association.private route_table_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table_association.private subnet_id
-
Semantic claim Open items
The engine read 11 statements the source makes about this routing table and decided what happens to each; 11 of them are critical settings, 9 of those still open.
- 2 kept as it is
- 9 left to a person to review
- 26 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/48
module.vpc.module.vpc.aws_route_table.private- claim: associations = KNOWN, CRITICAL, REVIEW
- claim: egress-restriction = KNOWN, CRITICAL, REVIEW
- claim: inbound-none = KNOWN, CRITICAL, PRESERVED
- claim: nat-fixed-egress-address = KNOWN, CRITICAL, REVIEW
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: route-destinations = KNOWN, CRITICAL, REVIEW
- claim: route-set-completeness = KNOWN, CRITICAL, PRESERVED
- claim: route-targets = KNOWN, CRITICAL, REVIEW
- claim: routes = KNOWN, CRITICAL, REVIEW
- claim: subnet-association-target = KNOWN, CRITICAL, REVIEW
- claim: tcr-route-table-vpc-id = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for one routing table with 1 static route and 1 attachment. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has one
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- How many instances of the table exist is that is not visible statically
- Attached to a subnet: a value that is not visible statically
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.private- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.private
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed for a project outside a Network Area), but the NAT gateway's fixed egress address is lost - the network leaves by its project's shared address, which is not fixed - so an architect decides how an allow-list on that address is kept.
- 1 manual action, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- decision:
DEC-NET-STACKITROUTE-NAT-FIXED-EGRESS-ADDRESS-LOST(aliasstackitroute:module.vpc.module.vpc.aws_route_table.private:NAT_FIXED_EGRESS_ADDRESS_LOST) - manual action: alias
stackitroute:precondition-outside-area:module.vpc.module.vpc.aws_route_table.private(BEFORE_PILOT): Create the target project outside a Network Area: module.vpc.module.vpc.aws_route_table.private is replaced by STACKIT's default routing, which was observed to give a routed network the same reachability only in a project outside a Network Area - no target: NOT_DRAFTED: STACKIT's default routing replaces the table, with a loss: a route of the table sends traffic to a NAT gateway (the others, if any, to an internet gateway), and the reachability is observed on the target for a project outside a Network Area, which this draft does not write. Observed in one sandbox project outside a Network Area (tested on a STACKIT project on 2026-10-10; routing tables are refused there): a routed network reaches the internet with no route and no routing table configured, a server without a public IP through the network's shared SNAT address and a server with a public IP through its own; nothing initiated from the internet reached a server behind the network address; egress is restricted by the egress rules of security groups, not by a route; routed networks reach each other with no table. No stackit_routing_table is drafted. A NAT gateway adds what an internet route does not. Its fixed egress address is LOST (observed): the address a routed STACKIT network leaves by is the network's publicIp, one address for every routed network of the project, not fixed (it changed twice when every network of the project was deleted) and not settable (a PATCH of it answers 202 and is ignored), so a third party's allow-list on the NAT gateway's address does not survive; a STACKIT public IP per server keeps its address, the only one the probe saw stay fixed. The egress restriction (the gateway as the only way out of a private subnet) is carried by the egress rules of security groups, not by a route (observed); whether the source restricts egress that way is for the architect. The absence of inbound paths of a private subnet is observed for a server without a public IP (tcp 22, 80 and 8080 on the network address). Not observed: a Network Area and its default routing table. The outbound address of the servers an allow-list names is the architect's choice: keep the changing address, or give each server that an allow-list names a STACKIT public IP
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the routing table resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
- check: route-complete ok=true: 0 route block(s) written as resources, each with its table, a cidrv4 destination and a next hop
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.public
-
Source Established
module.vpc.module.vpc.aws_route_table.public is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 164-179). Whether it exists is decided only when OpenTofu plans. It is part of module.vpc.module.vpc. It states 1 static route.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/79
module.vpc.module.vpc.aws_route_table.public- knowledge base case: rt-default-only
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.public
-
Evidence Established
The source states 1 static route for this unit. 1 route is stated exactly.
- a route resource: 0.0.0.0/0 to an internet gateway
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 164-179.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 164-179
- source route: module.vpc.module.vpc.aws_route.public_internet_gateway
-
Resolution proof Open items
5 references are resolved for this unit: 0 proven, 3 named but not proven, 2 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: refers to module.vpc.module.vpc.aws_vpc.this, named but not proven (an expression that selects one resource)
- the table of the route resource module.vpc.module.vpc.aws_route.public_internet_gateway: refers to module.vpc.module.vpc.aws_route_table.public[count.index], named but not proven (a reference to one instance)
- the target of a route resource: 0.0.0.0/0 to an internet gateway: refers to module.vpc.module.vpc.aws_internet_gateway.this[0], named but not proven (a reference to one instance)
- the table of the association module.vpc.module.vpc.aws_route_table_association.public: no resource could be named, so the reference is not resolved
- what the association module.vpc.module.vpc.aws_route_table_association.public attaches the table to: no resource could be named, so the reference is not resolved
In engineering/review-edges.csv of this report.
Expert: identifiers
Artefact: REPORT_FILE engineering/review-edges.csv
module.vpc.module.vpc.aws_route_table.public- proof cause: kind-not-exact:PROVEN_JOIN_ONE at module.vpc.module.vpc.aws_route_table.public vpc_id
- proof cause: selects-collapsed at module.vpc.module.vpc.aws_route_table_association.public route_table_id
- proof cause: selects-collapsed at module.vpc.module.vpc.aws_route_table_association.public subnet_id
- proof cause: target-presence:instances-not-visible at module.vpc.module.vpc.aws_route.public_internet_gateway gateway_id
- proof cause: target-presence:instances-not-visible at module.vpc.module.vpc.aws_route.public_internet_gateway route_table_id
- proof: INDEXED_REFERENCE/NOT_EXACT at module.vpc.module.vpc.aws_route.public_internet_gateway gateway_id
- proof: INDEXED_REFERENCE/NOT_EXACT at module.vpc.module.vpc.aws_route.public_internet_gateway route_table_id
- proof: PROVEN_JOIN_ONE/NOT_EXACT at module.vpc.module.vpc.aws_route_table.public vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table_association.public route_table_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table_association.public subnet_id
-
Semantic claim Open items
The engine read 8 statements the source makes about this routing table and decided what happens to each; 8 of them are critical settings, 5 of those still open.
- 1 kept as it is
- 5 left to a person to review
- 2 not applicable here
- 29 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/49
module.vpc.module.vpc.aws_route_table.public- claim: associations = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: route-destinations = KNOWN, CRITICAL, REVIEW
- claim: route-set-completeness = KNOWN, CRITICAL, PRESERVED
- claim: route-targets = KNOWN, CRITICAL, REVIEW
- claim: routes = KNOWN, CRITICAL, REVIEW
- claim: subnet-association-target = KNOWN, CRITICAL, NOT_APPLICABLE
- claim: tcr-route-table-vpc-id = KNOWN, CRITICAL, REVIEW
-
Intent Open items
The unit stands for one routing table with 1 static route and 1 attachment. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has one
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- How many instances of the table exist is that is not visible statically
- Attached to a subnet: a value that is not visible statically
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.public- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.public
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed on a routed network of a project outside a Network Area; the default table of a Network Area was never read) or the source creates no instance of it, so nothing is drafted.
- 1 manual action, due before the pilot
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- manual action: alias
stackitroute:precondition-outside-area:module.vpc.module.vpc.aws_route_table.public(BEFORE_PILOT): Create the target project outside a Network Area: module.vpc.module.vpc.aws_route_table.public is replaced by STACKIT's default routing, which was observed to give a routed network the same reachability only in a project outside a Network Area - no target: NOT_DRAFTED: STACKIT's default routing replaces the table: every route of the table sends traffic to an internet gateway, and the equivalence is observed on the target for a project outside a Network Area, which this draft does not write. Observed in one sandbox project outside a Network Area (tested on a STACKIT project on 2026-10-10; routing tables are refused there): a routed network reaches the internet with no route and no routing table configured, a server without a public IP through the network's shared SNAT address and a server with a public IP through its own; nothing initiated from the internet reached a server behind the network address; egress is restricted by the egress rules of security groups, not by a route; routed networks reach each other with no table. No stackit_routing_table is drafted. Observed in one project of one region on one day, so not HIGH; not observed: a Network Area and its default routing table, where this would be open again
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes no resource for this unit, so the checks over the draft compared nothing of it.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- check: final-artifact ok=true: the routing table resources of the written files read back as the plan (0 written resources, 0 attributes and 0 references compared in the final files)
- check: plan-valid ok=true: the plan satisfies targetplan.Validate
- check: renders ok=true: the rendered files parse as HCL
- check: round-trip ok=true: the rendered files read back as the plan (0 written resources, 0 attributes and 0 references compared in the draft)
- check: route-complete ok=true: 0 route block(s) written as resources, each with its table, a cidrv4 destination and a next hop
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_route_table.redshift
-
Source Established
module.vpc.module.vpc.aws_route_table.redshift is an AWS route table, declared in .terraform/modules/vpc.vpc/main.tf (lines 610-620). It is switched off in the source. It is part of module.vpc.module.vpc. It states 0 static routes.
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/80
module.vpc.module.vpc.aws_route_table.redshift- knowledge base case: rt-local-only
- knowledge base rule: aws.route_table
- source type: aws_route_table
- unit: module.vpc.module.vpc.aws_route_table.redshift
-
Evidence Established
The source states no static route for this unit.
- Routes that reach the table at run time: nothing propagates routes into the table
- Whether the routes listed are all the table has: the routes listed are all the table has
In the source: .terraform/modules/vpc.vpc/main.tf, lines 610-620.
Expert: identifiers
Artefact: SOURCE_FILE .terraform/modules/vpc.vpc/main.tf lines 610-620
No identifiers.
-
Resolution proof Open items
1 reference is resolved for this unit: 0 proven, 1 not resolved. Only a proven reference selects a resource; the others stay open and are never guessed.
- the network of the table: no resource could be named, so the reference is not resolved
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
module.vpc.module.vpc.aws_route_table.redshift- proof cause: source-not-present at module.vpc.module.vpc.aws_route_table.redshift vpc_id
- proof: UNRESOLVED/NONE at module.vpc.module.vpc.aws_route_table.redshift vpc_id
-
Semantic claim Nothing to show
The engine made no statement about this unit: no semantic contract is available for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Intent Open items
The unit stands for one routing table with 0 static routes and 0 attachments. The routes are read as AWS reads them: the most specific destination wins, and the network's own ranges are always reachable.
- Route set: the routes listed are all the table has
- Default route for IPv4 addresses: the table has none
- Default route for IPv6 addresses: the table has none
- Routes learned at run time: nothing propagates routes into the table
- The table has 0 instances
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
route:module.vpc.module.vpc.aws_route_table.redshift- intent family: ROUTE
- intent: route:module.vpc.module.vpc.aws_route_table.redshift
-
Target capability Established
The target is the STACKIT routing table (stackit_routing_table and stackit_routing_table_route): a routing table of a Network Area and, separately, each of its routes.
- Service: partial
- API: partial
- Terraform: resource available, data source available, experimental
- Maturity: not established
- Entitlement: not established
- Lifecycle: not established
- Region: not established
- 2 known issues recorded for these resource types
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
network.routing- capability: network.routing
- known issue: provider-experimental-features-disabled-by-default
- known issue: provider-github-1751-network-area-region-route-stale-state
- provider version: 0.121.0
-
Transformation Open items
No STACKIT resource is planned for this unit: STACKIT's default routing replaces it (observed on a routed network of a project outside a Network Area; the default table of a Network Area was never read) or the source creates no instance of it, so nothing is drafted.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
- no target: NOT_DRAFTED: the source creates no instance of the table (count or for_each yields none, or it is switched off): no stackit_routing_table is drafted
- plan producer: stacktoit-stackitroute 0.1.0
-
Render Nothing to show
The draft writes no STACKIT resource for this unit, so nothing is rendered for it.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.
-
Validation Nothing to show
The draft writes nothing for this unit, so nothing was checked.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
-
Residual difference Nothing to show
The plan records no remaining difference between this unit and its STACKIT target. That is what the plan states, not a proof that the two are equivalent.
In target-plan.json of this report.
Expert: identifiers
Artefact: REPORT_FILE target-plan.json /plans
No identifiers.
module.vpc.module.vpc.aws_subnet.private
-
Source Established
module.vpc.module.vpc.aws_subnet.private is a resource of the source, declared in .terraform/modules/vpc.vpc/main.tf (lines 267-293). Whether it exists is decided only when OpenTofu plans. It is part of module.vpc.module.vpc. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.vpc.module.vpc.aws_subnet.private (.terraform/modules/vpc.vpc/main.tf:267) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/85
module.vpc.module.vpc.aws_subnet.private- knowledge base case: subnet
- knowledge base rule: aws.subnet
- source type: aws_subnet
- unit: module.vpc.module.vpc.aws_subnet.private
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- DNS: the source uses the AWS VPC resolver, which answers internal EC2 host names (module.vpc.module.vpc.aws_vpc.this enable_dns_hostnames = true); ipv4_nameservers = var.default_ipv4_nameservers resolves public names only.
- Private DNS parity not established: STACKIT documents no private DNS zone or internal name resolution (STACKIT DNS serves public zones only; the DNS Resolver product is in beta); names only the VPC resolver answers need a DNS server of your own.
- Behind the network ACL module.vpc.module.vpc.aws_default_network_acl.this (no STACKIT resource, so nothing here refuses what it refuses): not every rule of it could be read, so a deny rule may be among them (see module.vpc.module.vpc.aws_default_network_acl.this).
- Drafted, consumers not placed: decision DEC-GEN-CONVERT-WORKLOAD-PLACEMENT (alias `convert:module.vpc.module.vpc.aws_subnet.private:network:WORKLOAD_PLACEMENT`). Nothing in the draft is placed in this network, although the source places module.dependencies.aws_mq_broker.mq, …
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: finding: subnet-egress-ipv4-unproven
- recorded: finding: topology-vpc-unproven
- recorded: rule line: rule aws.subnet/subnet · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-d39d5b78739a
-
Semantic claim Open items
The engine read 9 statements the source makes about this resource and decided what happens to each; 9 of them are critical settings, 5 of those still open.
- 4 kept as it is
- 5 left to a person to review
- 87 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/50
module.vpc.module.vpc.aws_subnet.private- claim: availability-zone = UNKNOWN, CRITICAL, REVIEW
- claim: dns64 = KNOWN, CRITICAL, PRESERVED
- claim: ipv6 = KNOWN, CRITICAL, PRESERVED
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: prefix = UNKNOWN, CRITICAL, REVIEW
- claim: private-egress-ipv4 = KNOWN, CRITICAL, REVIEW
- claim: subnet-vpc-membership = KNOWN, CRITICAL, REVIEW
- claim: tc-subnet-enable-resource-name-dns-a-record-on-launch = KNOWN, CRITICAL, PRESERVED
- claim: tc-subnet-enable-resource-name-dns-aaaa-record-on-launch = KNOWN, CRITICAL, PRESERVED
-
Render Established
The draft holds 1 block for this unit, written as active Terraform.
- stackit_network.vpc_vpc_private: written as an active resource (terraform/network.tf, lines 23-29); the whole comment of the block is in engineering/trace/network.md
In terraform/network.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/network.tf
stackit_network.vpc_vpc_private- block in the draft: stackit_network.vpc_vpc_private
- block in the draft: terraform/network.tf:23-29
- trace: TR-d39d5b78739a
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 3 findings, 2 open items, 1 open decision of the converter. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.private): availability_zone, availability_zone_id — stackit_network has no availability zone (pinned provider): the network serves the region; servers and volumes choose their zone.
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.private): vpc_id — the source VPC is not generated: the network is created in the project (stackit_network also takes a vpc_id of the experimental STACKIT VPC feature, pinned provider — not used by this draft).
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.private): tags — the tags are not visible statically (a variable without a value, a computed value, a module output or an expression the scan cannot evaluate): no label is written for them. Set the labels of the stackit_network yourself where they are …
- warning: The project can be taken as one VPC's boundary only if every resource that names a VPC provably names the estate's one, and this estate does not show it: the VPC this subnet names, or the VPC another resource of the estate names (a network ACL, a flow log, a peering connection, a Cloud …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: PRIVATE_EGRESS_EQUIVALENCE_UNPROVEN (IPv4, not proven).
- Open: PRIVATE_EGRESS_EQUIVALENCE_UNPROVEN — whether the source gives this subnet an IPv4 route to the internet is not proven (table-not-proven (selects-collapsed)); the network drafted here keeps STACKIT's default gateway with its outbound source NAT, and the draft leaves its routing and gateway settings …
- Open: how many instances module.vpc.module.vpc.aws_subnet.private creates is not visible statically (its count/for_each is not known): count is var.vpc_vpc_private_count — set it to the real number and check each instance's settings.
- 1 open decision of the converter wait for a person: the unit is not ready to deploy until each is decided
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- decision:
DEC-GEN-CONVERT-WORKLOAD-PLACEMENT(aliasconvert:module.vpc.module.vpc.aws_subnet.private:network:WORKLOAD_PLACEMENT)
module.vpc.module.vpc.aws_subnet.public
-
Source Established
module.vpc.module.vpc.aws_subnet.public is a resource of the source, declared in .terraform/modules/vpc.vpc/main.tf (lines 131-158). Whether it exists is decided only when OpenTofu plans. It is part of module.vpc.module.vpc. The block that stands for it in the draft is written by a generator that records no intent and no plan, so this trace is made from the lines the draft records for it, not from a typed plan: it holds the stages those lines support and none of the others.
- from module.vpc.module.vpc.aws_subnet.public (.terraform/modules/vpc.vpc/main.tf:131) — RECONFIGURE / MEDIUM
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /units/86
module.vpc.module.vpc.aws_subnet.public- knowledge base case: subnet
- knowledge base rule: aws.subnet
- source type: aws_subnet
- unit: module.vpc.module.vpc.aws_subnet.public
-
Evidence Established
The generator that writes this unit's block states, above the block, why its values are what they are. These are the generator's own statements in the draft, not checks of the draft.
- DNS: the source uses the AWS VPC resolver, which answers internal EC2 host names (module.vpc.module.vpc.aws_vpc.this enable_dns_hostnames = true); ipv4_nameservers = var.default_ipv4_nameservers resolves public names only.
- Private DNS parity not established: STACKIT documents no private DNS zone or internal name resolution (STACKIT DNS serves public zones only; the DNS Resolver product is in beta); names only the VPC resolver answers need a DNS server of your own.
- Behind the network ACL module.vpc.module.vpc.aws_default_network_acl.this (no STACKIT resource, so nothing here refuses what it refuses): not every rule of it could be read, so a deny rule may be among them (see module.vpc.module.vpc.aws_default_network_acl.this).
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
- recorded: finding: source-provider-unpinned
- recorded: finding: subnet-egress-ipv4-unproven
- recorded: finding: subnet-route-table-undecided
- recorded: finding: topology-vpc-unproven
- recorded: rule line: rule aws.subnet/subnet · KB 0.384.0 · target maturity GA · lifecycle active · mapping maturity beta · evidence internal · review required
- recorded: trace: TR-ca04594a2ad9
-
Semantic claim Open items
The engine read 11 statements the source makes about this resource and decided what happens to each; 11 of them are critical settings, 6 of those still open.
- 5 kept as it is
- 6 left to a person to review
- 85 further statements that the source does not make (nothing to carry)
In assessment.json of this report.
Expert: identifiers
Artefact: REPORT_FILE assessment.json /kernel/units/51
module.vpc.module.vpc.aws_subnet.public- claim: availability-zone = UNKNOWN, CRITICAL, REVIEW
- claim: dns64 = KNOWN, CRITICAL, PRESERVED
- claim: effective-route-table = KNOWN, CRITICAL, REVIEW
- claim: ipv6 = KNOWN, CRITICAL, PRESERVED
- claim: network-topology-boundary = KNOWN, CRITICAL, REVIEW
- claim: prefix = UNKNOWN, CRITICAL, REVIEW
- claim: private-egress-ipv4 = KNOWN, CRITICAL, REVIEW
- claim: public-ip-on-launch = KNOWN, CRITICAL, PRESERVED
- claim: subnet-vpc-membership = KNOWN, CRITICAL, REVIEW
- claim: tc-subnet-enable-resource-name-dns-a-record-on-launch = KNOWN, CRITICAL, PRESERVED
- claim: tc-subnet-enable-resource-name-dns-aaaa-record-on-launch = KNOWN, CRITICAL, PRESERVED
-
Render Established
The draft holds 1 block for this unit, written as active Terraform.
- stackit_network.vpc_vpc_public: written as an active resource (terraform/network.tf, lines 46-52); the whole comment of the block is in engineering/trace/network.md
In terraform/network.tf of this report.
Expert: identifiers
Artefact: REPORT_FILE terraform/network.tf
stackit_network.vpc_vpc_public- block in the draft: stackit_network.vpc_vpc_public
- block in the draft: terraform/network.tf:46-52
- trace: TR-ca04594a2ad9
-
Residual difference Open items
The draft states, for this unit: 3 properties it does not carry, 4 findings, 2 open items. That is what the draft states, not a proof that the block and the source are equivalent.
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.public): availability_zone, availability_zone_id — stackit_network has no availability zone (pinned provider): the network serves the region; servers and volumes choose their zone.
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.public): vpc_id — the source VPC is not generated: the network is created in the project (stackit_network also takes a vpc_id of the experimental STACKIT VPC feature, pinned provider — not used by this draft).
- NOT CARRIED (module.vpc.module.vpc.aws_subnet.public): tags — the tags are not visible statically (a variable without a value, a computed value, a module output or an expression the scan cannot evaluate): no label is written for them. Set the labels of the stackit_network yourself where they are …
- warning: The project can be taken as one VPC's boundary only if every resource that names a VPC provably names the estate's one, and this estate does not show it: the VPC this subnet names, or the VPC another resource of the estate names (a network ACL, a flow log, a peering connection, a Cloud …
- warning: The scan cannot say which route table this subnet follows: a route table association may name it through a value the scan cannot resolve (a variable, a literal ID, a conditional, a value from a module call), an association names only some of its instances or repeats by a count or for_each …
- warning: No lock file entry pins aws (>= 3.0, >= 3.29, >= 4.18, >= 4.30, >= 4.59, >= 5.64, >= 5.79, ~> 5.0): the version the plan would use is not proven (stated once for the whole estate)
- warning: PRIVATE_EGRESS_EQUIVALENCE_UNPROVEN (IPv4, not proven).
- Open: PRIVATE_EGRESS_EQUIVALENCE_UNPROVEN — whether the source gives this subnet an IPv4 route to the internet is not proven (the route table association module.vpc.module.vpc.aws_route_table_association.public names the subnet module.vpc.module.vpc.aws_subnet.public but the scan cannot show that it …
- Open: how many instances module.vpc.module.vpc.aws_subnet.public creates is not visible statically (its count/for_each is not known): count is var.vpc_vpc_public_count — set it to the real number and check each instance's settings.
Held in memory in this build; no file contains it.
Expert: identifiers
Artefact: IN_MEMORY
No identifiers.